LXD Flaw: CVE-2026-112816 TLS Impersonation
Canonical just patched a maximum-severity flaw in LXD and MicroCloud, because an attacker could log in as a trusted client without ever holding that client...
Found 643 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Canonical just patched a maximum-severity flaw in LXD and MicroCloud, because an attacker could log in as a trusted client without ever holding that client...
If you use TeamViewer to connect to other computers, you need to update right now, because a critical flaw in the remote desktop software lets the machine...
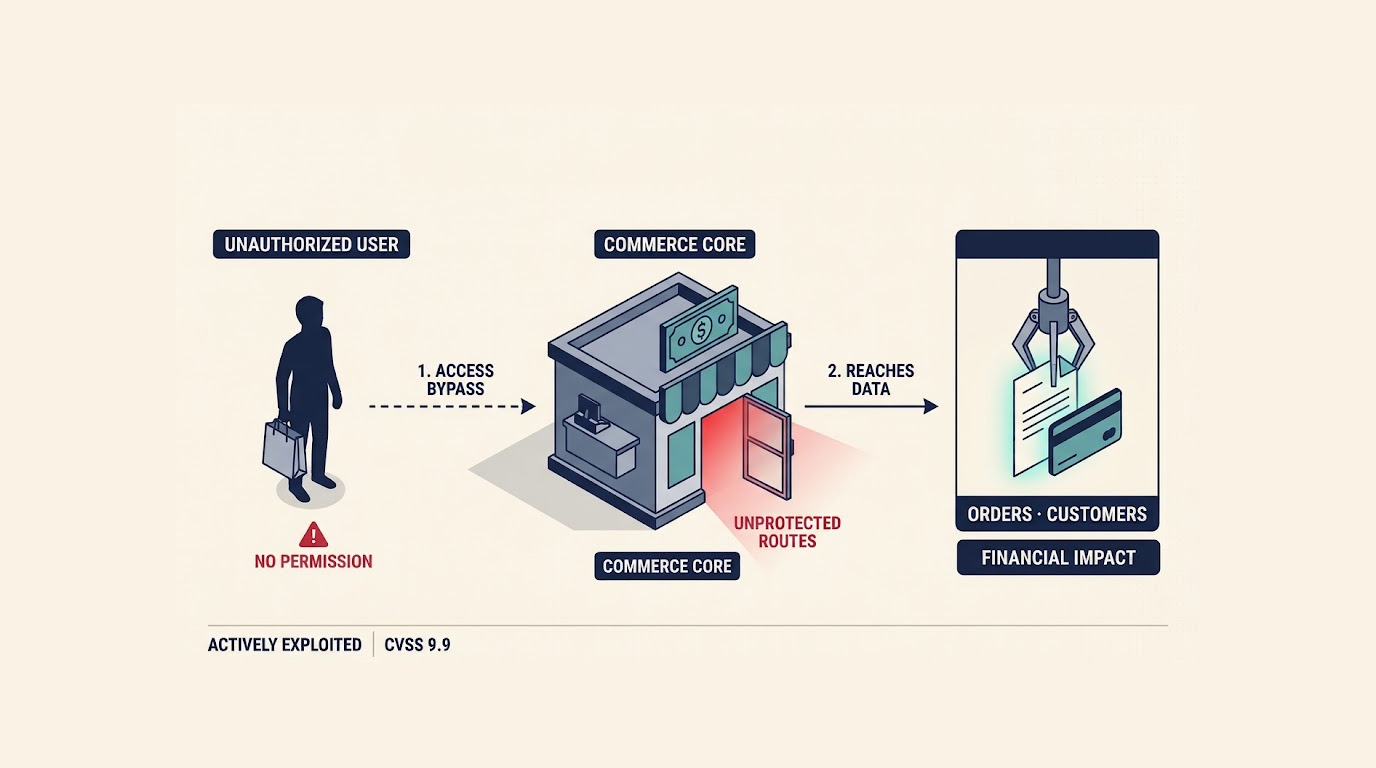
Drupal just issued an urgent warning that threat actors are actively exploiting a highly critical security flaw in its Commerce Core component, and if you...
Two incidents can look identical in the alert queue and be entirely different animals underneath, because one of them means somebody read data they shouldn...
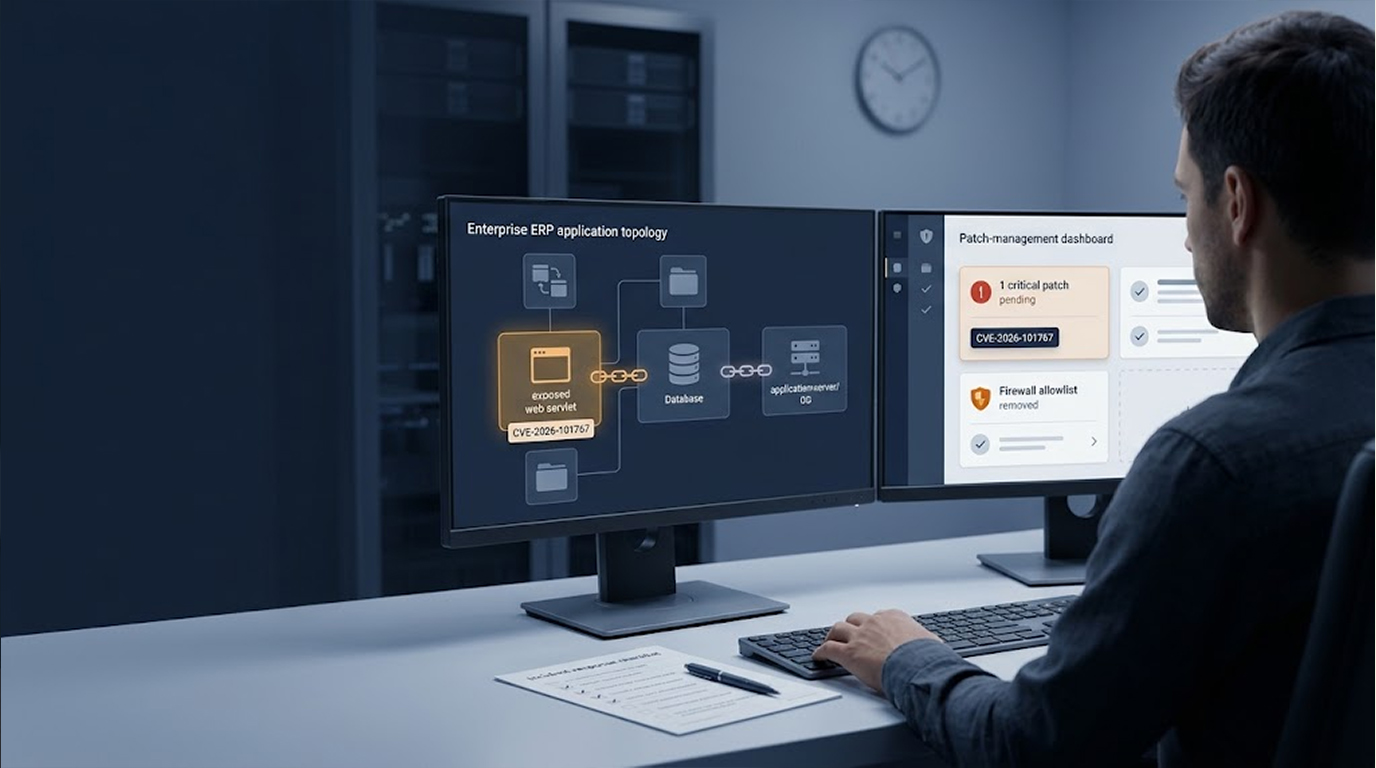
Threat actors are already probing for a newly patched critical vulnerability in Oracle E-Business Suite, because threat intelligence firm Defused Cyber jus...
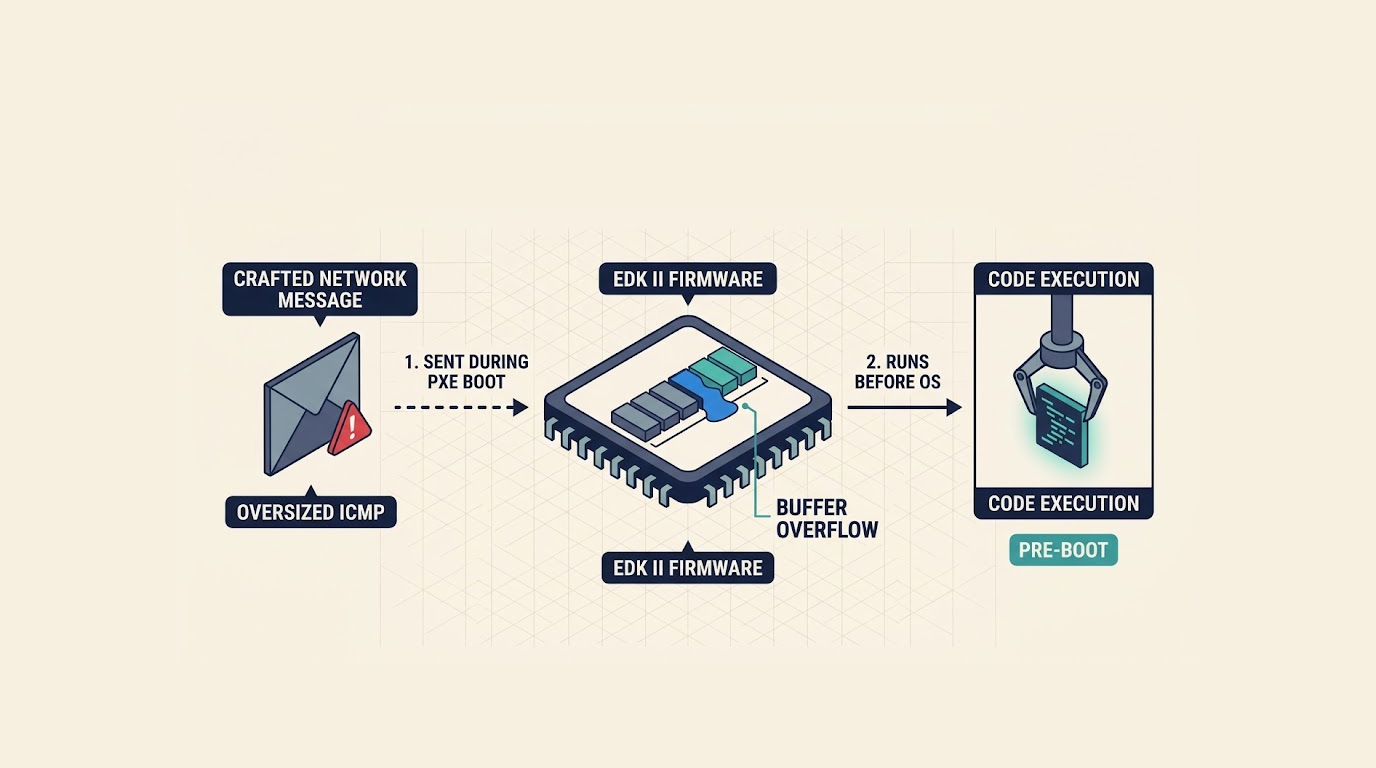
Your servers might be carrying a 16-year-old vulnerability in the firmware that boots them, because a critical buffer overflow in EDK II, the open-source c...
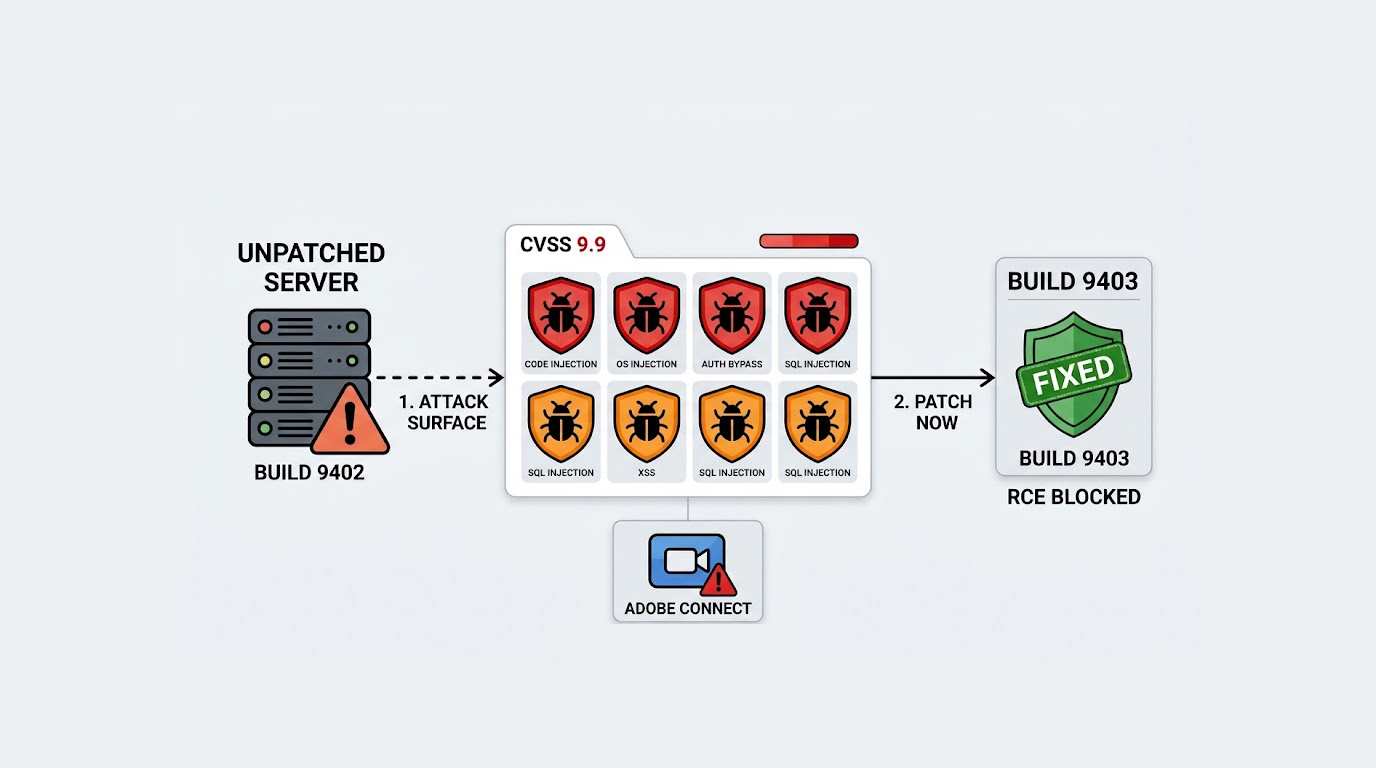
Adobe just dropped a massive security update, and if you are running Adobe Campaign Classic on Windows or Linux, you need to patch your servers right now,...
Most explanations of AI vulnerability discovery stop at the vague sentence that the model reads your code and spots weaknesses, which is unhelpful if you'r...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067