RAG Poisoning: AI's Biggest Security Blind Spot
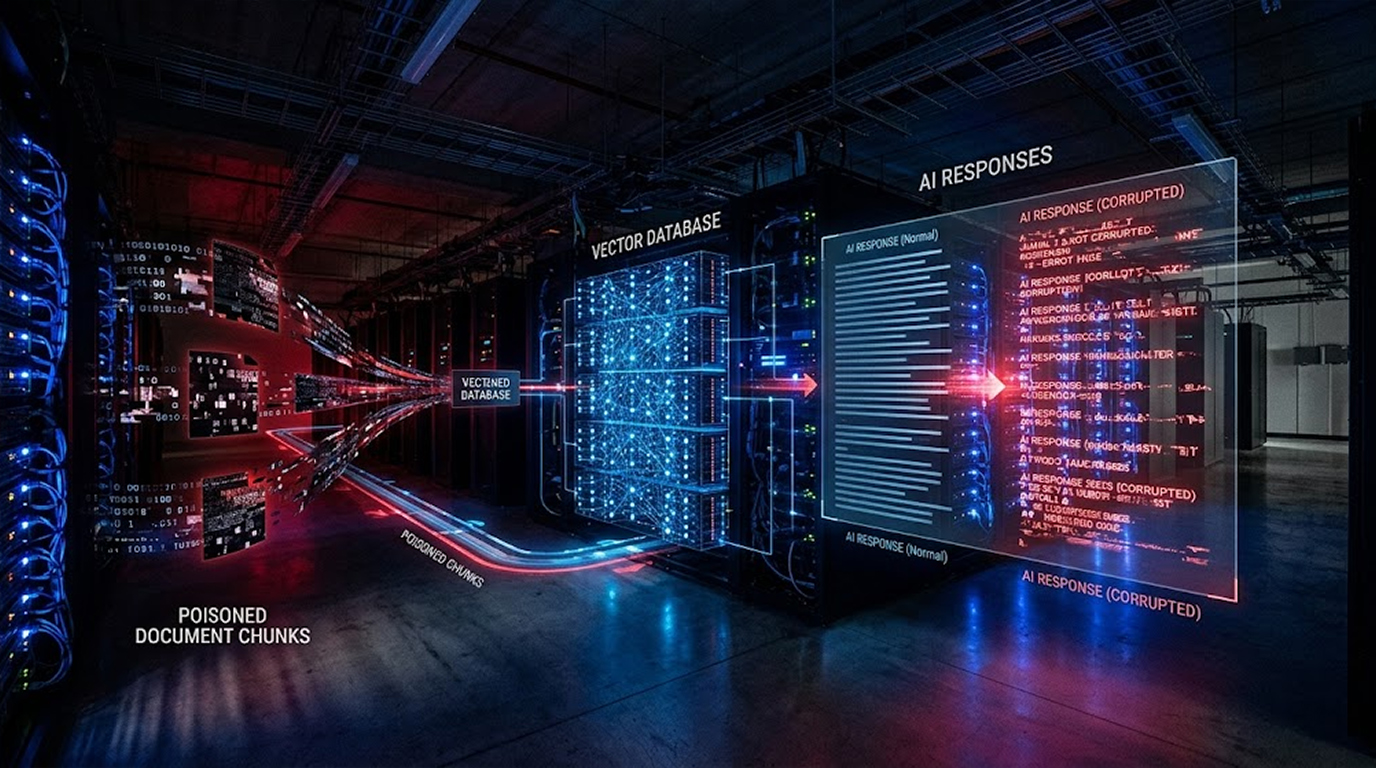
Your AI assistant just told a developer to install a malicious package. It cited a "trusted" internal document as the source. The document looked legitimat...
Found 56 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Your AI assistant just told a developer to install a malicious package. It cited a "trusted" internal document as the source. The document looked legitimat...
A massive set of 737 free VPN and proxy extensions have been discovered in the Chrome Web Store. Extensions mostly target the Russian speaking users seekin...
cPanel has released a targeted security update addressing a vulnerability that could let an authenticated hosting customer execute SQL in the database's ro...
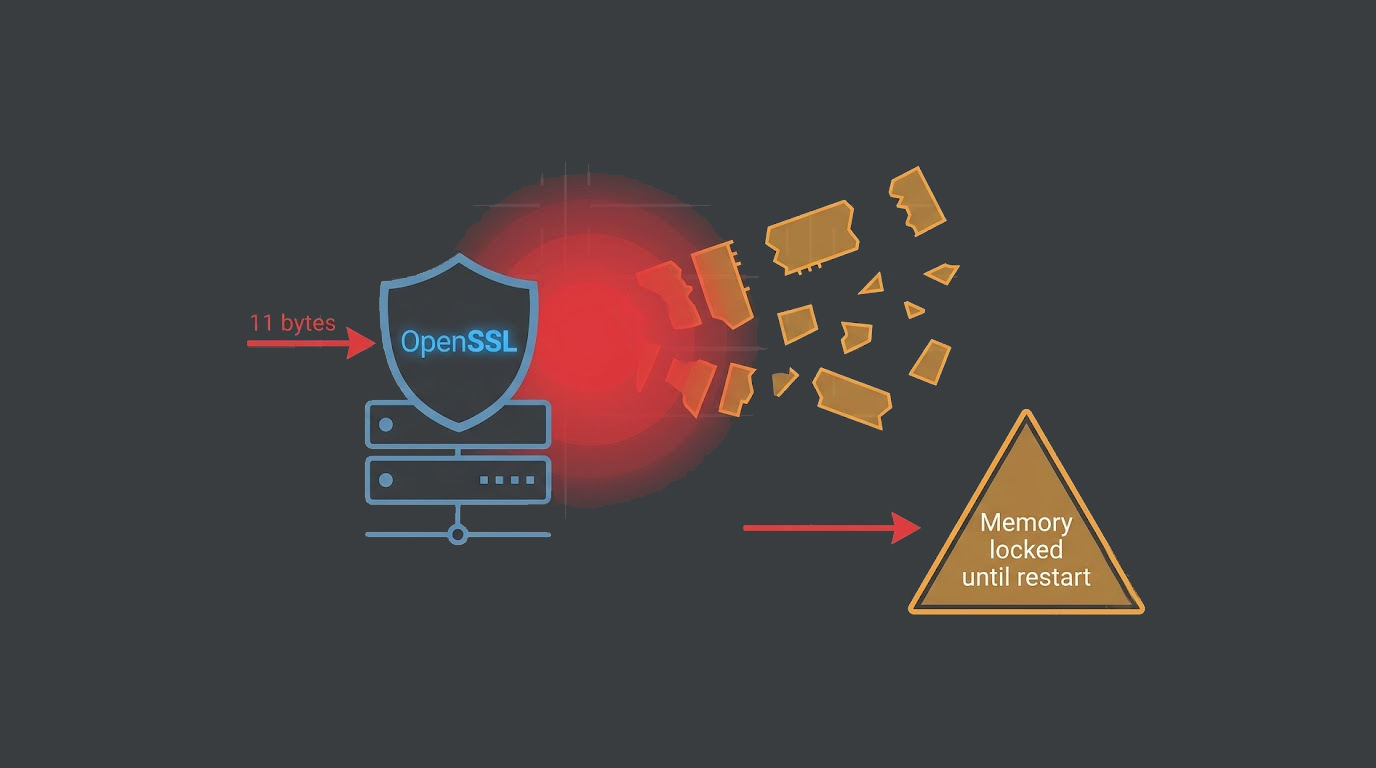
Eleven bytes. That's all it takes to make an unpatched OpenSSL server set aside up to 131 KB of memory for a message that never arrives. On systems running...
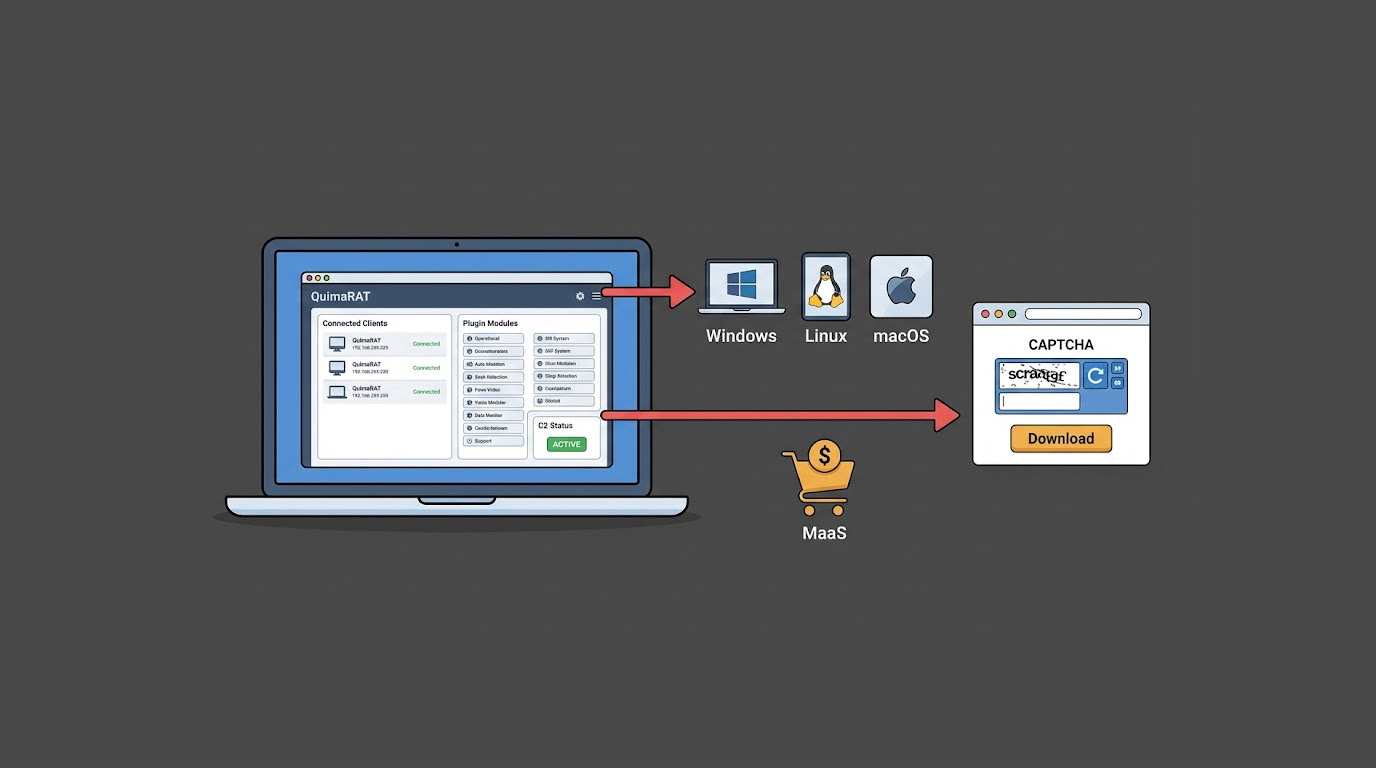
QuimaRAT, which is a new form of Java-based Remote Access Trojan, can attack systems running on Windows, Linux, and macOS platforms. The malware is offered...
In just 88 minutes, a single npm account published more than 140 malicious versions of packages in the Mastra namespace. Mastra is a popular open-source Ja...
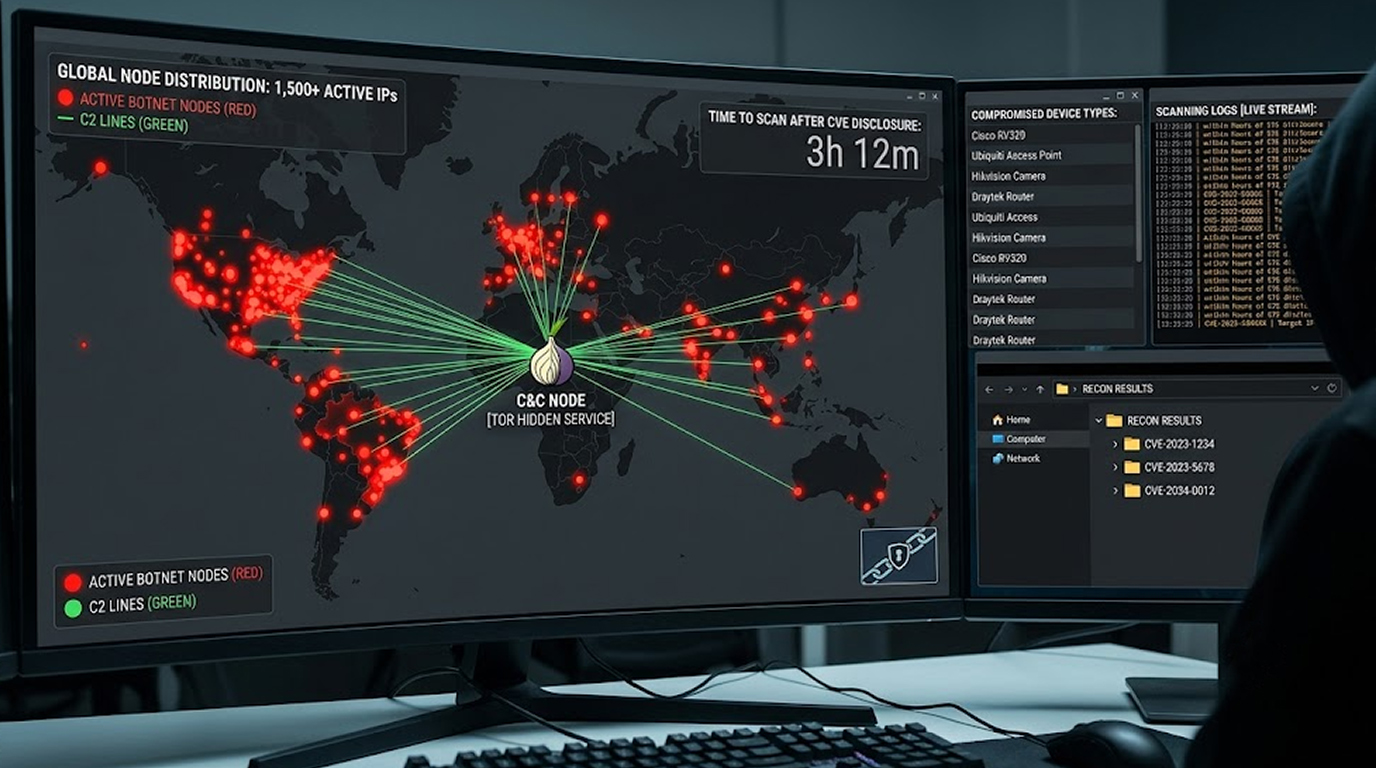
Remember the KV-botnet? The U.S. government took it down in early 2024. But the operators behind it didn't disappear. They adapted. Now a new report from...
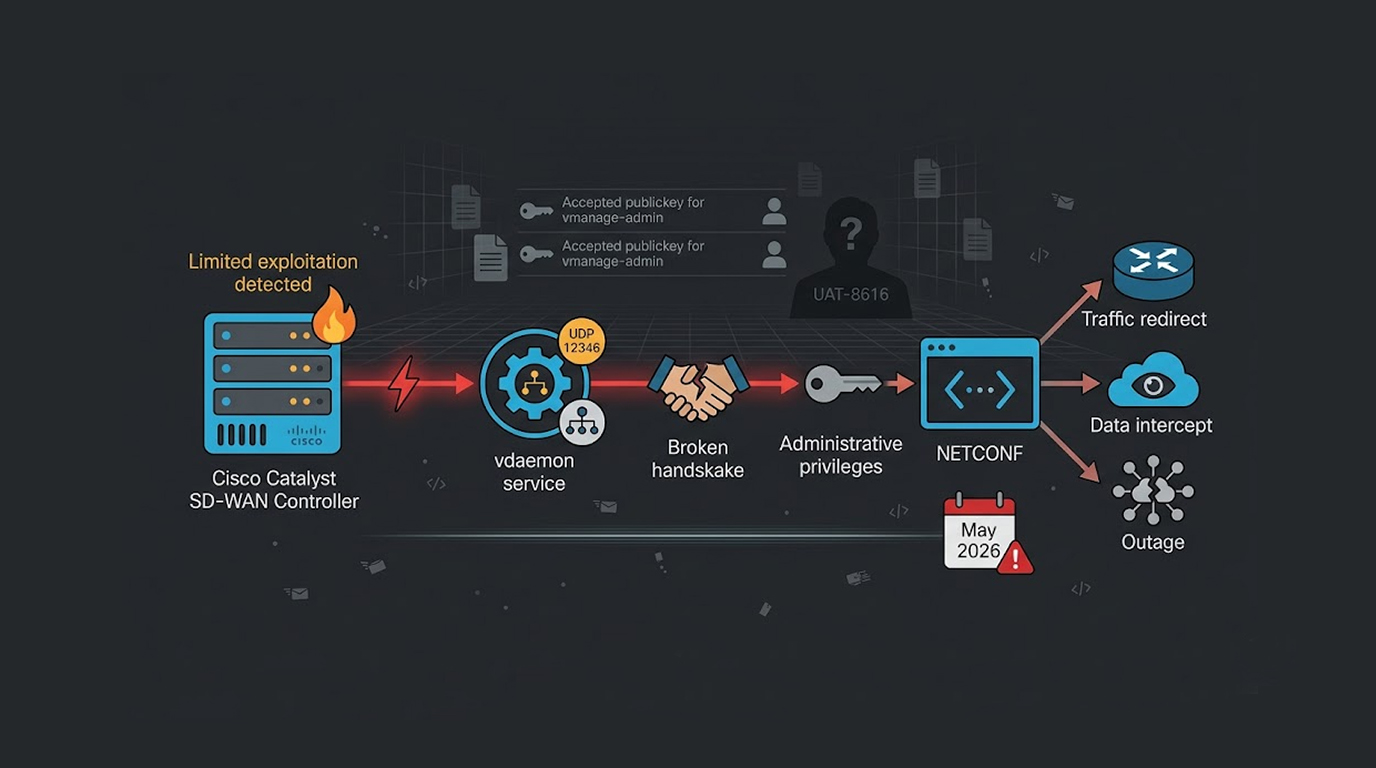
Cisco has released emergency updates for a critical vulnerability in its Catalyst SD-WAN Controller, and the flaw carries a CVSS score of 10.0 which is the...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067