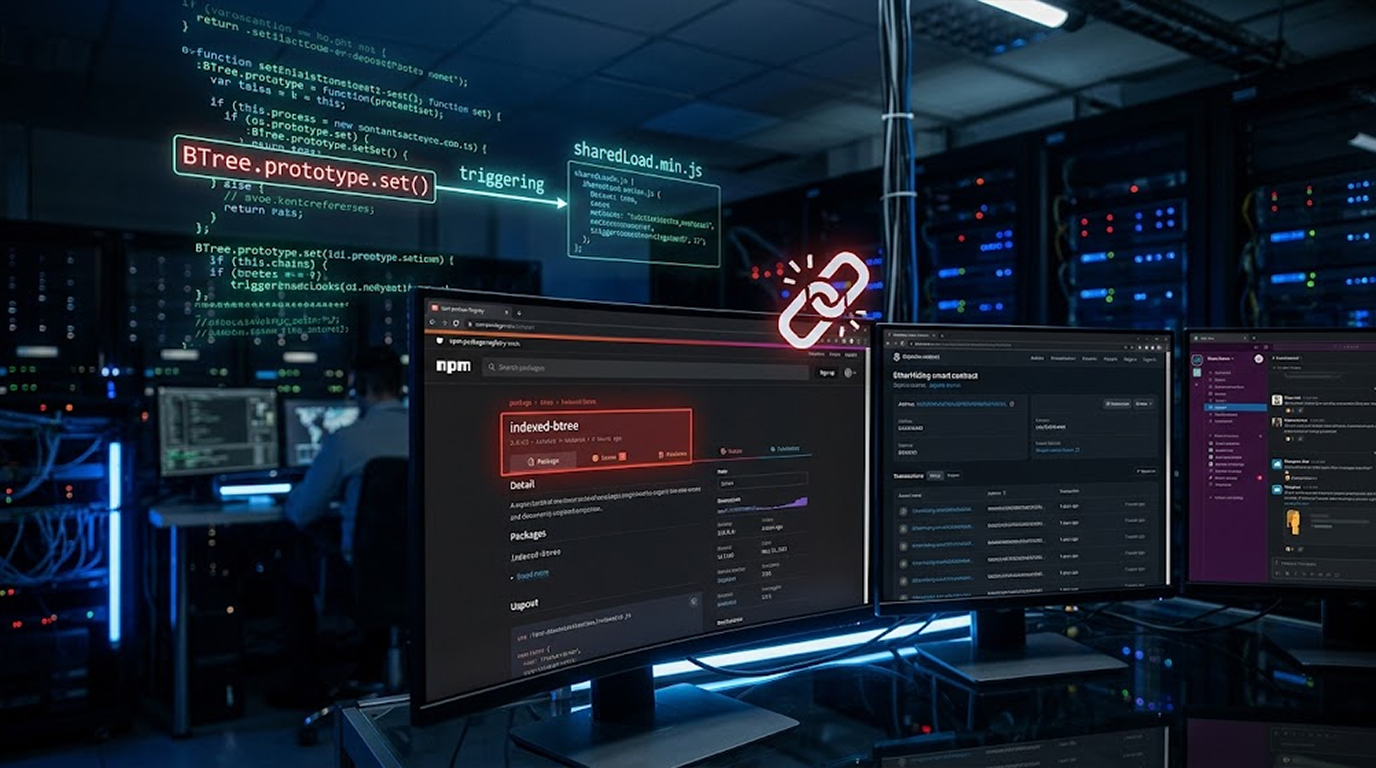
indexed-btree Malicious npm Package Uses Runtime Code
A malicious npm package called indexed-btree has been caught hiding its payload inside application code, rather than using lifecycle scripts, which is a si...
Found 183 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A malicious npm package called indexed-btree has been caught hiding its payload inside application code, rather than using lifecycle scripts, which is a si...
Three researchers at Hacktron just pulled off something wild. They used Anthropic's Claude Opus 5 to take over the ChatGPT and Codex accounts of several Op...
You build an image, you push it to a registry, you deploy it to production, and somewhere inside that image is a vulnerable package nobody noticed, sitting...
Gyazo, the image-sharing service run by Helpfeel, just disclosed a serious security breach. The numbers are big. About 23.62 million user records were expo...
Iran's intelligence service is running a malware campaign that targets dissidents, journalists, and activists around the world. And they're using Telegram...
You have probably heard the warning, do not unpickle untrusted data, and you probably nodded along because it makes sense, pickle is dangerous, we know thi...
You download a pre-trained model from a public repository, it works great in testing, and you are ready to push it to production, but here is the thing, th...
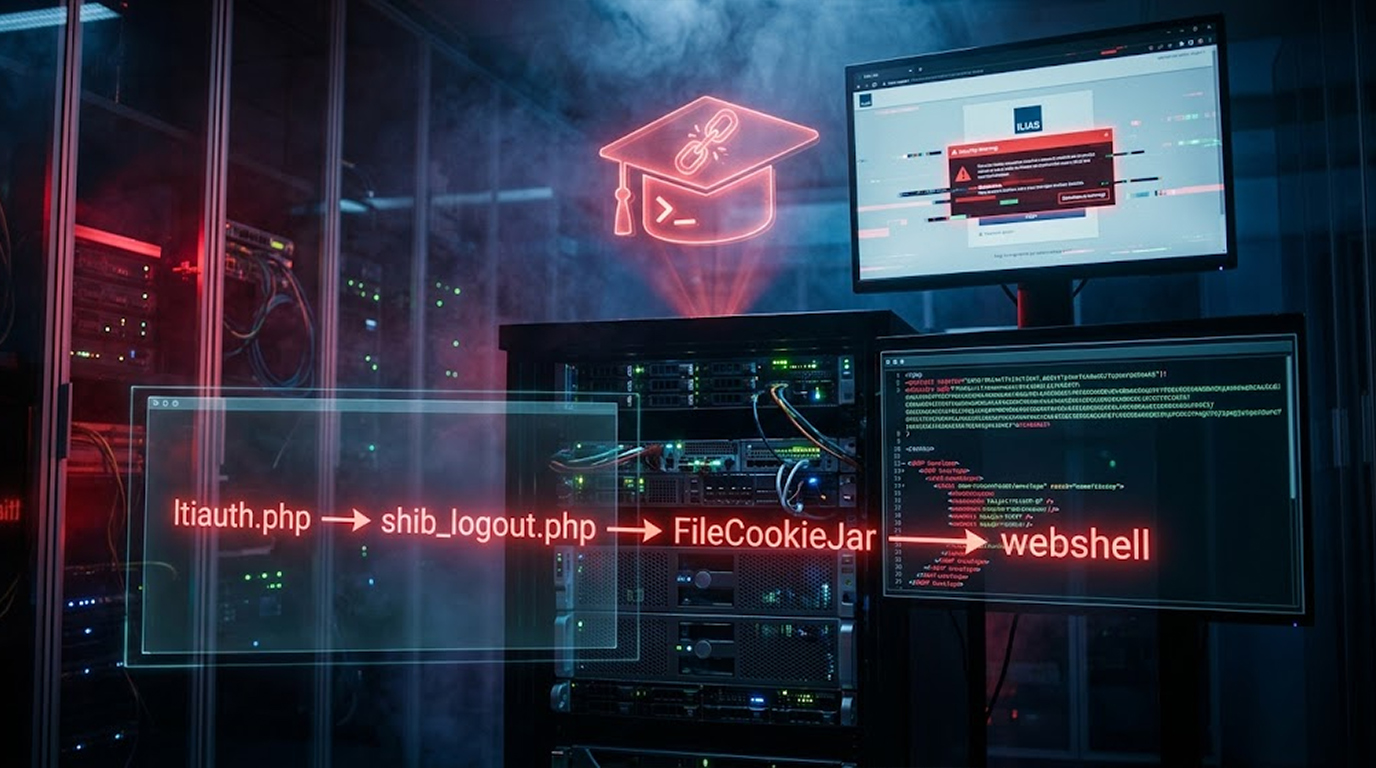
Here's a fun one. ILIAS has two endpoints that don't require authentication. One of them writes to your session. The other one reads your session back and...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067