JDY Botnet Resurgence and Expansion Hits 1,500 Devices
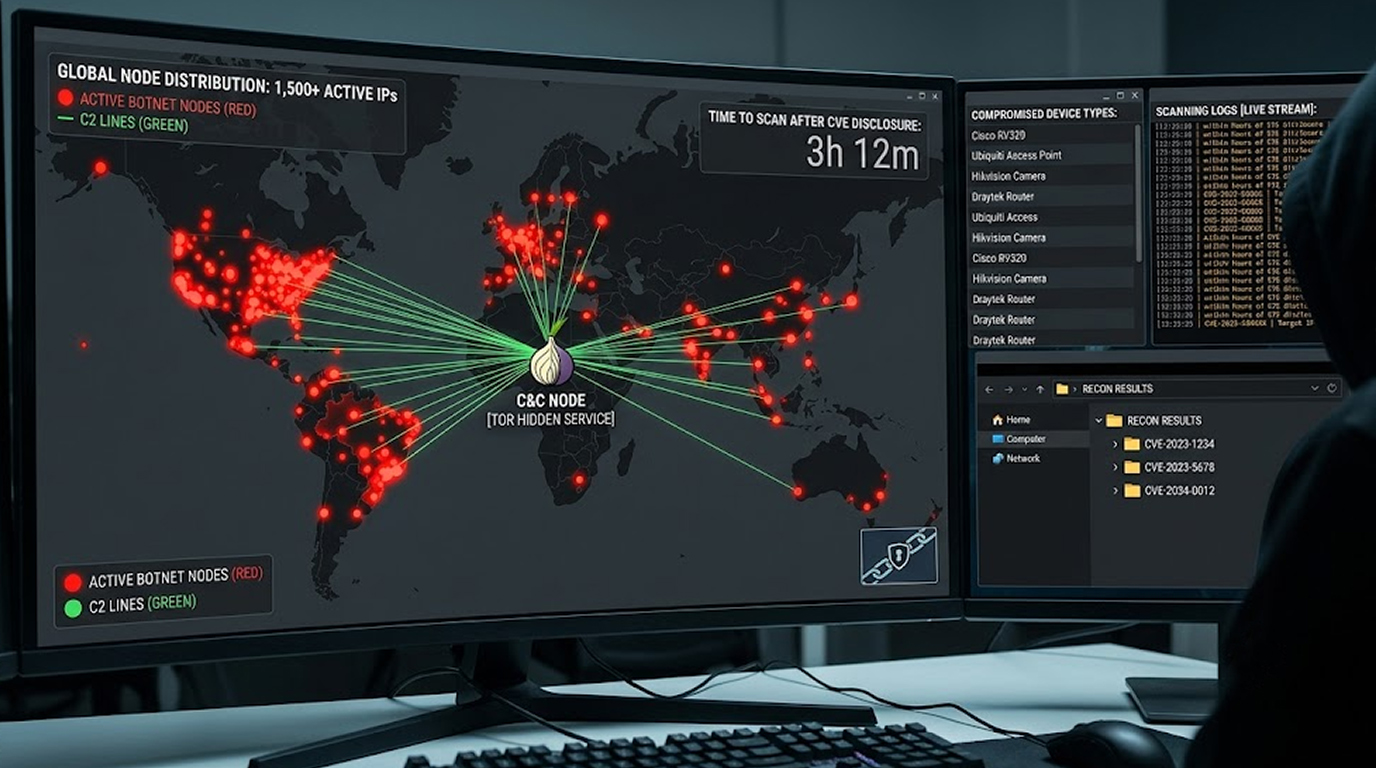
Remember the KV-botnet? The U.S. government took it down in early 2024. But the operators behind it didn't disappear. They adapted. Now a new report from...
Found 48 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Remember the KV-botnet? The U.S. government took it down in early 2024. But the operators behind it didn't disappear. They adapted. Now a new report from...
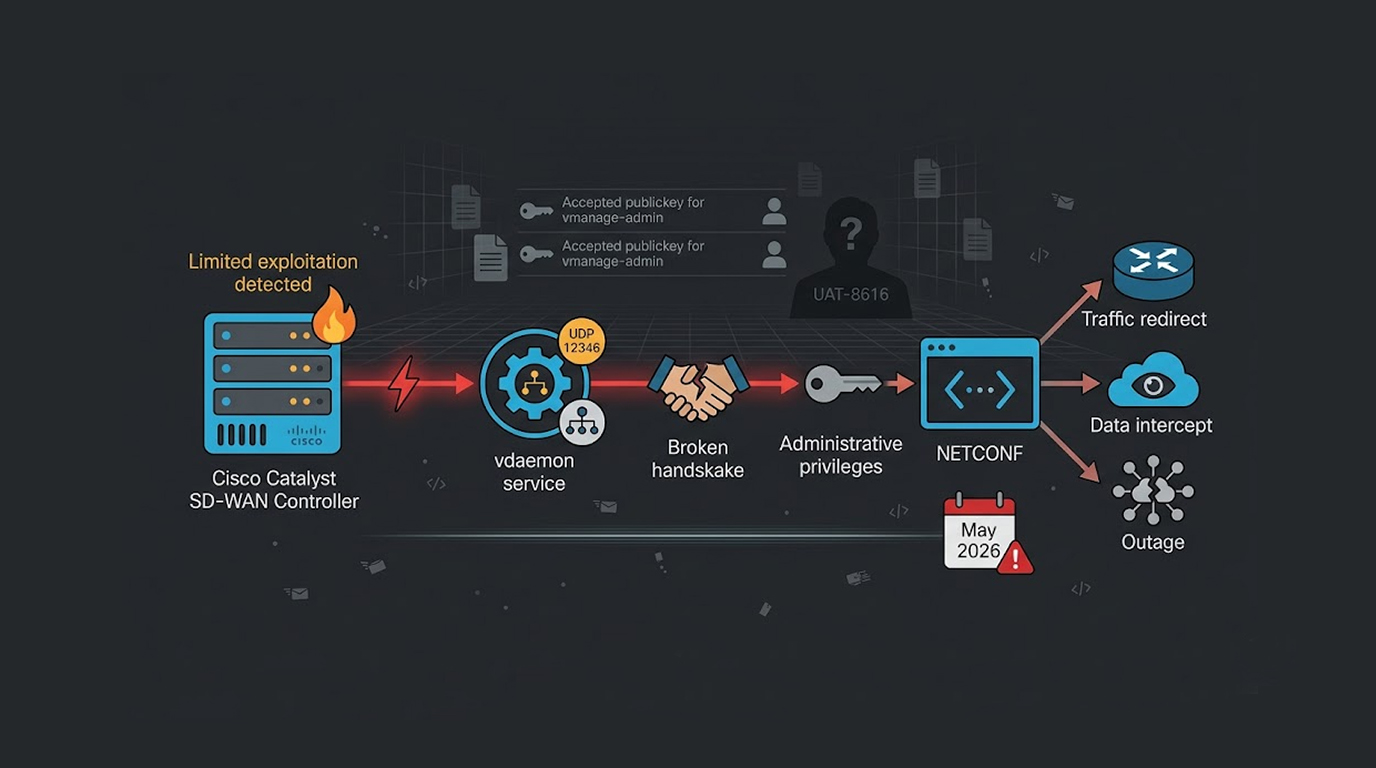
Cisco has released emergency updates for a critical vulnerability in its Catalyst SD-WAN Controller, and the flaw carries a CVSS score of 10.0 which is the...
A popular open-source workflow automation platform is being turned against its users. Threat actors have discovered how to abuse n8n, a tool designed to co...
Cybersecurity researchers at Huntress have raised the alarm about a fast-moving device code phishing campaign that is actively targeting Microsoft 365 acco...
Microsoft's threat teams have uncovered a slick credential-theft operation that's been running since mid-January 2026, where attackers trick people searchi...
In recent months, Cisco Talos has identified a new modular malware framework referred to as VoidLink. The framework was discovered to have been utilized an...
Cisco Talos just pulled back the curtain on DKnife, one of the most sophisticated adversary-in-the-middle (AitM) frameworks we've seen from China-nexus act...
Many employees use personal or unapproved accounts of ChatGPT, Claude, Gemini, Grok, Perplexity, or similar LLMs, often because the official company-...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067