Joomla JCE Unauthenticated RCE Exploit Published for CVE
A critical unauthenticated remote code execution vulnerability in the JCE extension for Joomla has been exploited. A public proof-of-concept is now availab...
Found 76 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A critical unauthenticated remote code execution vulnerability in the JCE extension for Joomla has been exploited. A public proof-of-concept is now availab...
This is one way an attacker can use to exploit websites. The dangling-byte technique is a new and innovative approach to HTTP desync that enables an attack...
PortSwigger's James Kettle has built an AI-assisted research system called HTTP Terminator that generated and proved new HTTP desynchronization techniques...
You find a great prompt on GitHub. Someone has shared a brilliant way to make your AI agent analyze code, generate documentation, or even write tests. You...
You wake up and you find a message from your bank. "Your account has been locked urgently! Please click here to prove your identity." Your heartbeat races...
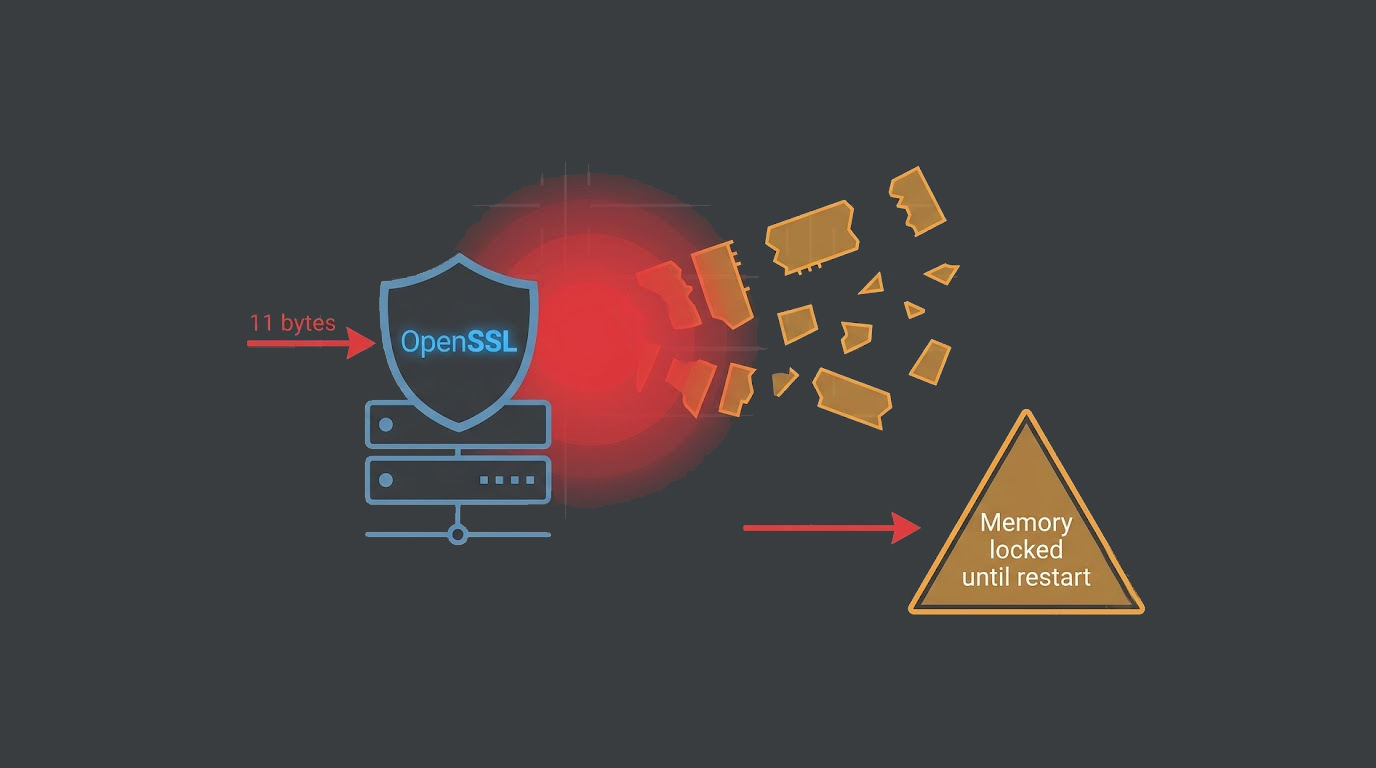
Eleven bytes. That's all it takes to make an unpatched OpenSSL server set aside up to 131 KB of memory for a message that never arrives. On systems running...
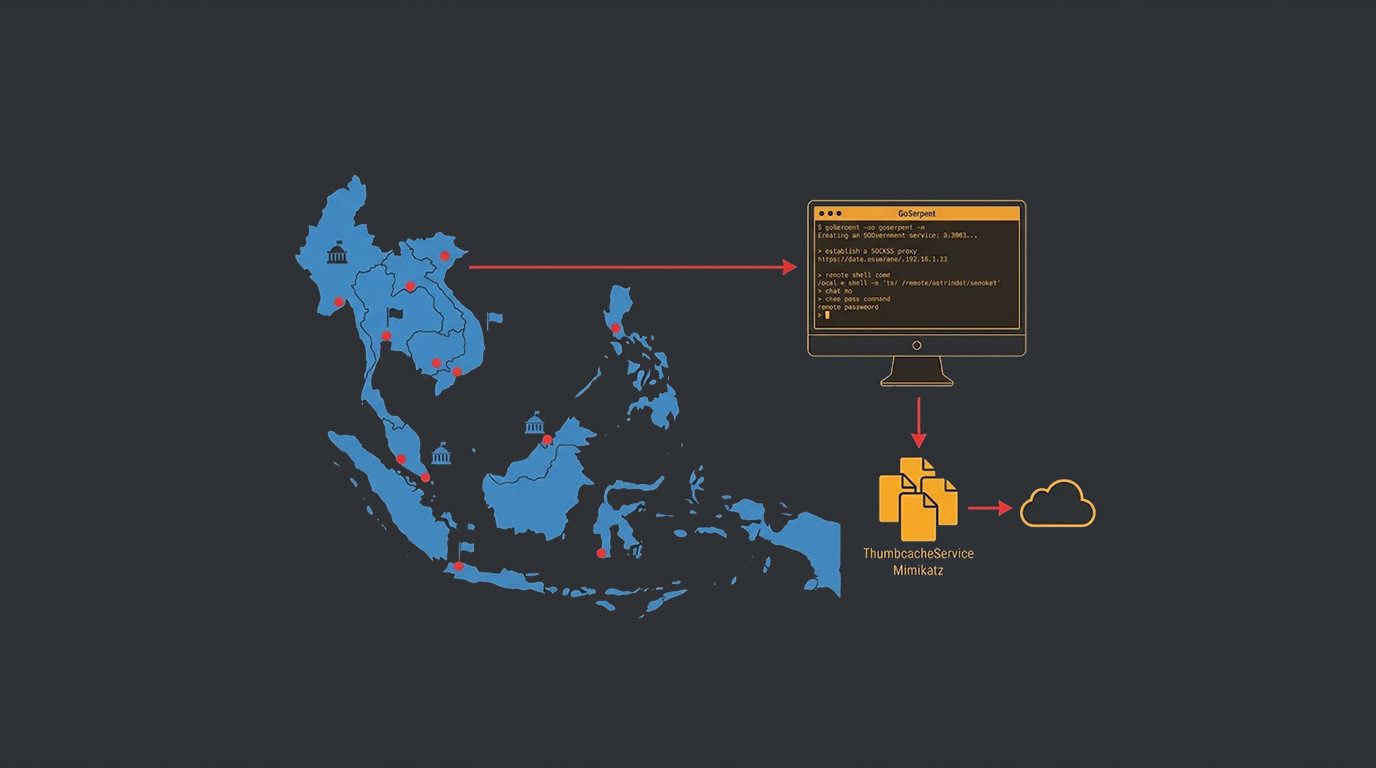
A new malware strain known as GoSerpent has been utilized in cyber attacks against targets from Southeast Asia starting in late 2025. As per Kaspersky, the...
You have done everything right. You patched your systems. You updated your software. You hardened your configurations. You are secure. But what if an atta...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067