Log Poisoning to Hidden Spam Pages
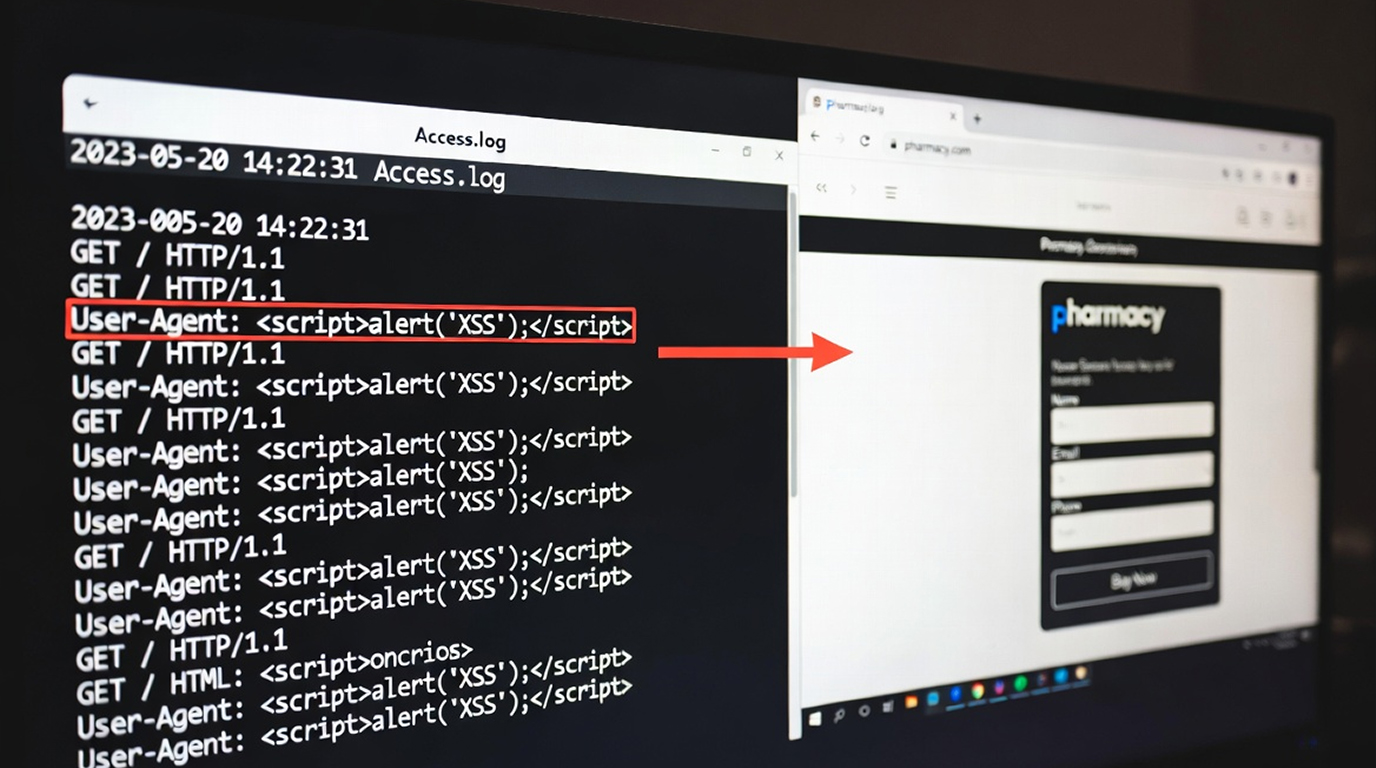
Log poisoning is a stealthy attack that is typically not given attention. However, it still creates lots of frustration for site owners. Instead of uploadi...
Found 427 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Log poisoning is a stealthy attack that is typically not given attention. However, it still creates lots of frustration for site owners. Instead of uploadi...
Your website is hacked. Here’s what matters right now. A business owner logs in.Everything looks normal. Traffic? Dropping.Customers? Complaining.G...
The postinstall script is one of the most abused features in the npm ecosystem right now (2025–2026). When you run npm install, anything listed in th...
In 2026, there is still an active known vulnerability on many WordPress sites that have seen extensive exploitation (both public and through Metasploit) an...
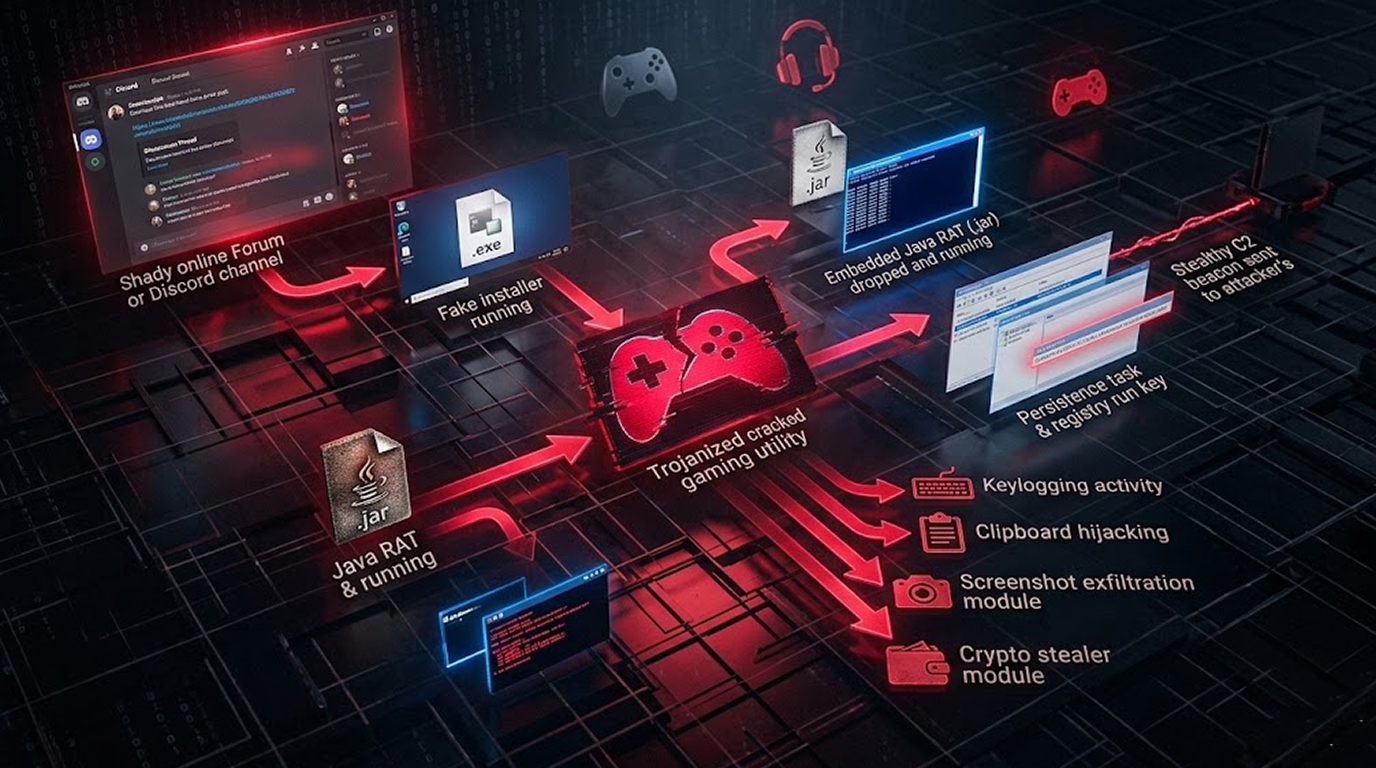
Threat actors have found a new way to hook gamers: they're slipping remote access trojans (RATs) into what look like handy gaming utilities, then spreading...
North Korean-linked hackers are running a slick, persistent operation that turns the job hunt into a security nightmare for developers. They have created p...
This is currently one of the most widespread and damaging Android infection chains targeting TikTok users, especially in regions with high TikTok engagemen...
Right now (early 2026) one of the most consistently successful phishing lures for spreading Android clipboard hijackers / wallet clippers is a very simple...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067