Grafana GitHub Token Breach Leads to Extortion Attempt
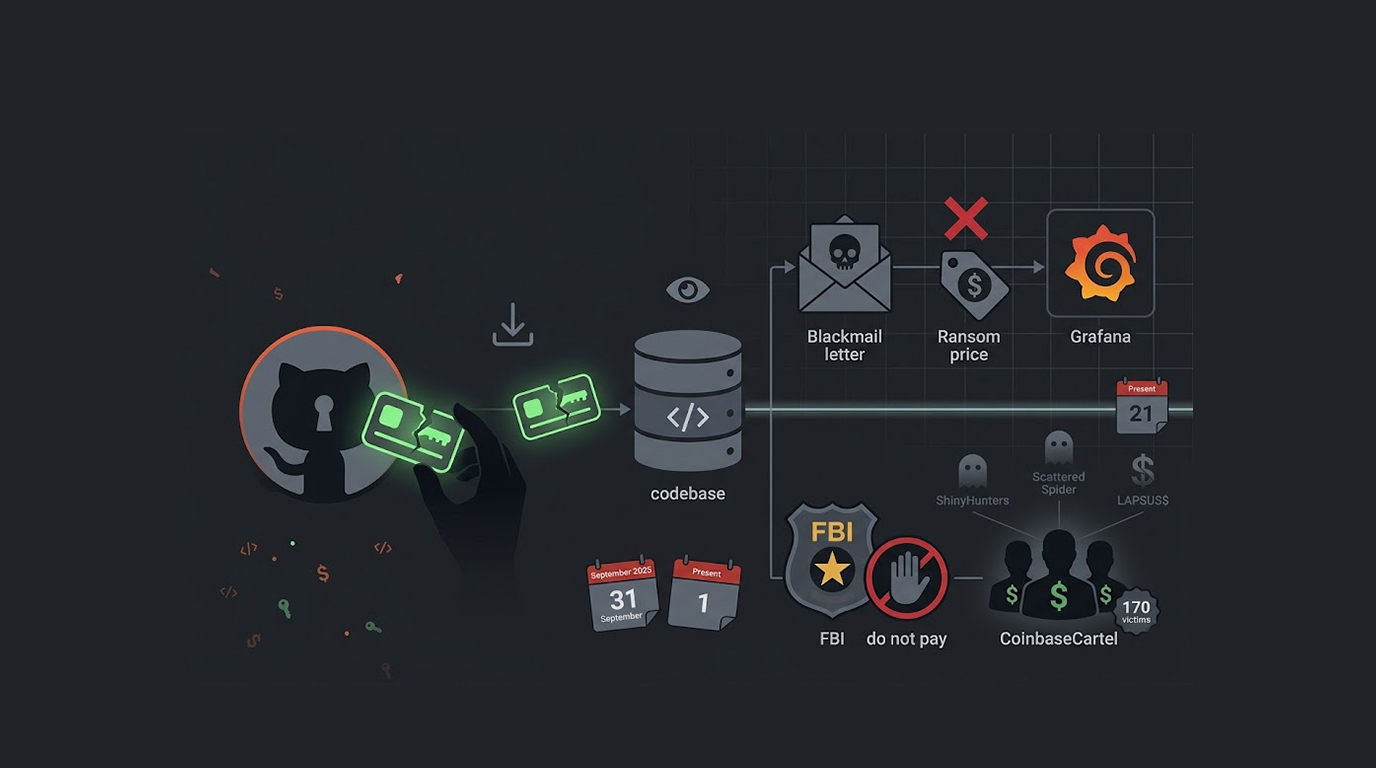
Grafana has disclosed that an unauthorized party obtained a token granting access to the company's GitHub environment, and the attacker used this access to...
Found 389 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Grafana has disclosed that an unauthorized party obtained a token granting access to the company's GitHub environment, and the attacker used this access to...
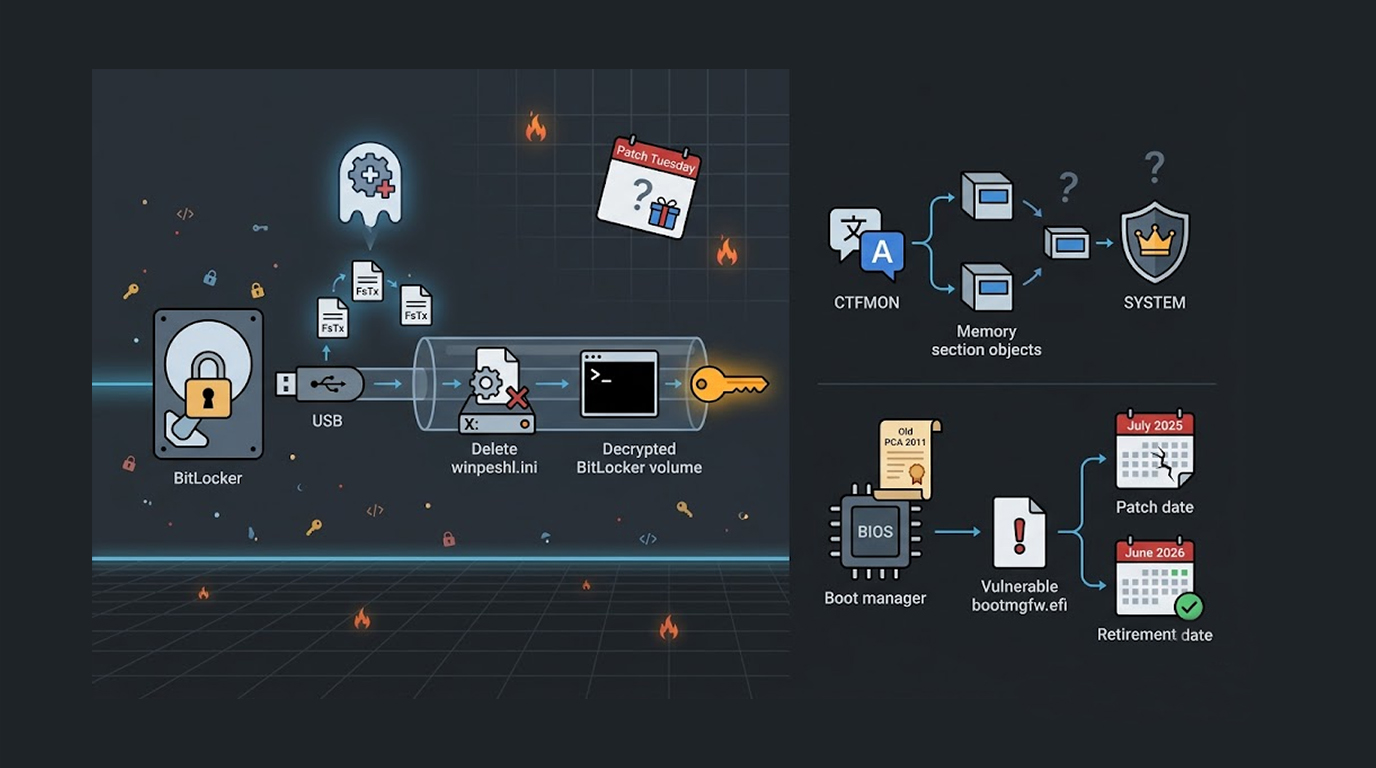
An anonymous security researcher who previously disclosed three Microsoft Defender zero-days is back with two more, and these new flaws affect BitLocker an...
You found your old phone in a drawer, it has been sitting there for a year, collecting dust.You decide to sell it, get a few pounds, clear some clutter. B...
Your network is set up like this, employees plug into the switch, servers plug into the same switch, everything can talk to everything, it is simple, it is...
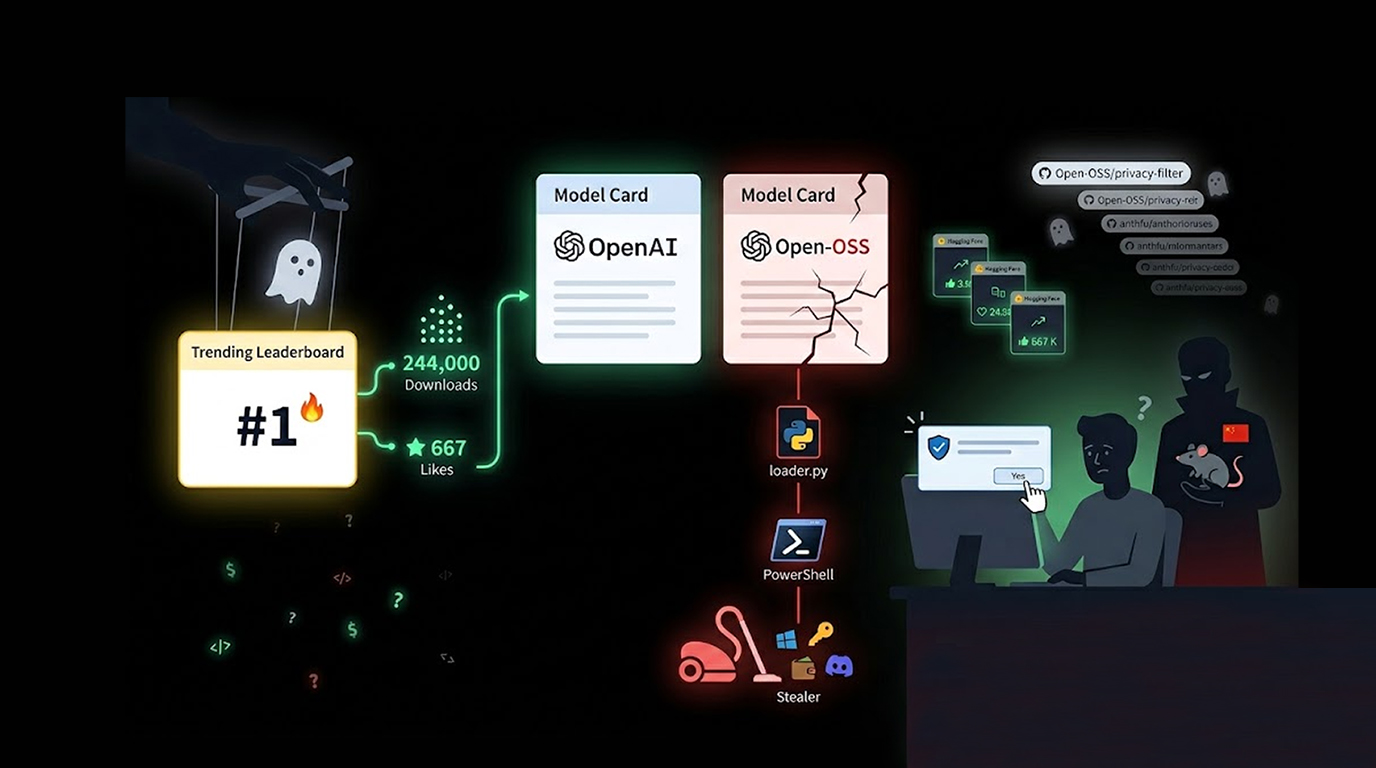
A malicious repository on Hugging Face ranked #1 on the platform by impersonating OpenAI's just-released Privacy Filter model while delivering a Rust-based...
A developer sits down at their Linux workstation, pushes code, publishes packages, and manages cloud infrastructure, but they have no idea that every keyst...
You have run Cobalt Strike for years, it works, but it is also the most signatured tool on the market, every defender knows how to spot it Havoc is differ...
Your Android TV box or smart TV could be part of a DDoS army right now. And you would never know.Security researchers at Hunt.io have uncovered a new Mirai...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067