Top SQL Injection Tools for Web Application Security Audits
If you’ve ever worked with websites or web apps, you’ve probably heard the term SQL injection (SQLi) tossed around. It’s one of those vul...
Found 183 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
If you’ve ever worked with websites or web apps, you’ve probably heard the term SQL injection (SQLi) tossed around. It’s one of those vul...
XSStrike is an open-source toolkit focused on cross-site scripting (XSS) discovery. It blends a smart payload generator, context awareness, and filtering/W...
Cybersecurity researchers are raising alarms over a supply chain attack targeting the popular npm package @solana/web3.js, widely used by Solana developers...
A newly discovered malware campaign, dubbed Horns&Hooves by Kaspersky, has been targeting private users, retailers, and service businesses primarily in...
In a concerning evolution of botnet capabilities, cybersecurity researchers have uncovered that the AndroxGh0st malware is now leveraging the Mozi botnet t...
A recent malware campaign targeting the npm (Node Package Manager) repository has raised alarms within the open-source ecosystem. Malicious packages are ac...
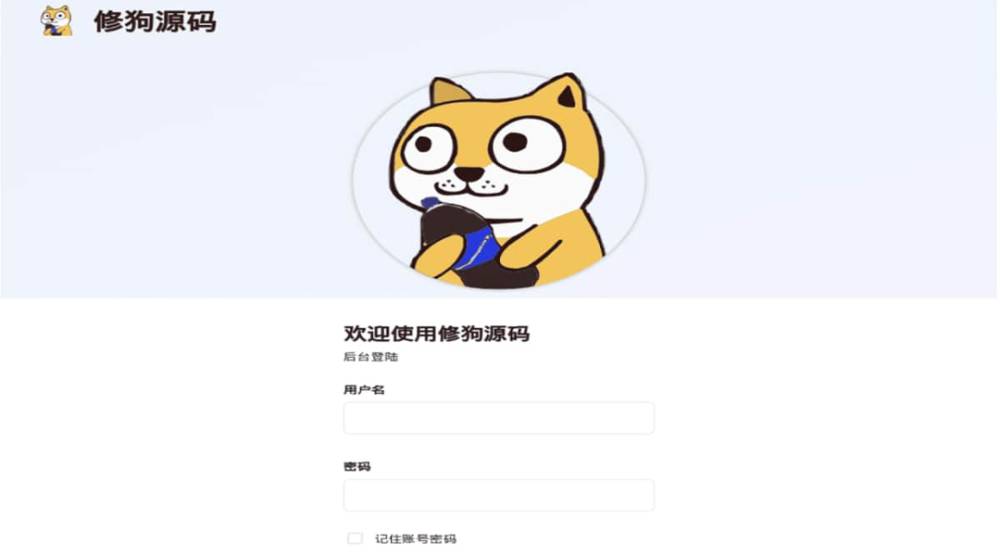
Cybersecurity researchers have revealed the existence of a sophisticated new phishing kit, Xiū gǒu, which has been used in campaigns across Australia, Japa...
A government entity and a religious organization in Taiwan recently became targets of a China-linked cyber espionage group known as Evasive Panda, which us...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067