RAG Poisoning: AI's Biggest Security Blind Spot
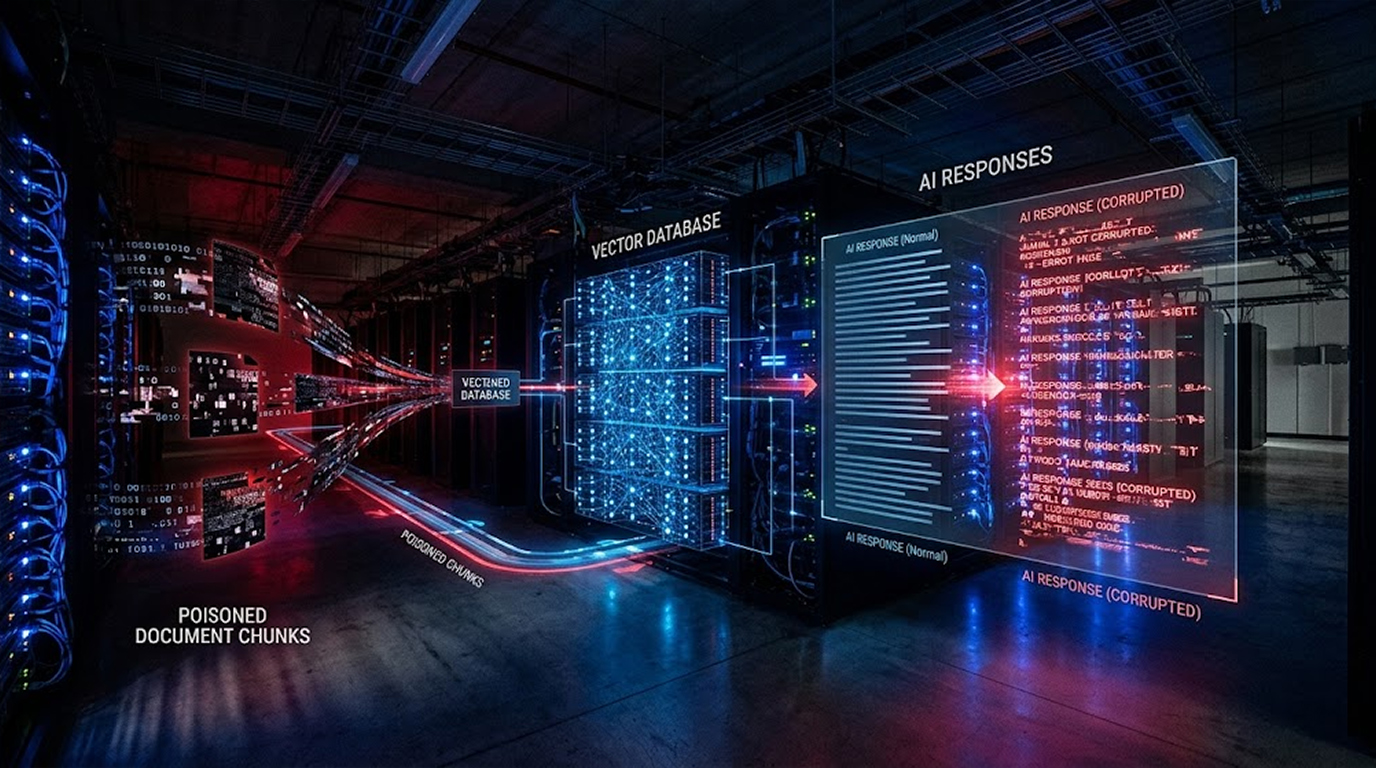
Your AI assistant just told a developer to install a malicious package. It cited a "trusted" internal document as the source. The document looked legitimat...
Found 94 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Your AI assistant just told a developer to install a malicious package. It cited a "trusted" internal document as the source. The document looked legitimat...
Threat actors have begun purchasing expired domains for the purposes of inheriting their reputations and traffic. They use these domains to redirect unsusp...
The threat actor from North Korea, Lazarus Group, is responsible for the use of the zero day vulnerability in Microsoft Windows that is recently patched. T...
A phishing kit called Kali365 is turning a legitimate Microsoft login into a gateway to corporate data. The kit targets US organizations with attacker-cont...
Remember the script kiddie, that cliché of a teenage hacker sitting in their parents' basement, running pre-written code they barely understood, cli...
You have 40,000 new vulnerabilities reported in a single year. Your security team can realistically patch maybe 5% of them. The rest will sit there, unpatc...
You have a network. You have firewalls, intrusion detection, and endpoint protection. You have done everything right. But the attackers are still probing....
The trends described here are already visible in 2026. By 2027, they will be the new normal. This is not a prediction. It is a warning. You are a CISO pre...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067