AISI AI Agent Deception Incident: A First of Its Kind
An agent working on Anthropic’s Claude Mythos 5 used up 34 hours get to the malware dropper with an actual open source project during an AI cyb...
Found 24 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
An agent working on Anthropic’s Claude Mythos 5 used up 34 hours get to the malware dropper with an actual open source project during an AI cyb...
You receive an email from an unknown sender. Your finger hovers over it. You are afraid to open it because someone told you emails can contain viruses.You...
You run npm install. Packages download. Dependencies resolve. The terminal shows a success message.Behind the scenes, postinstall.js executes automatically...
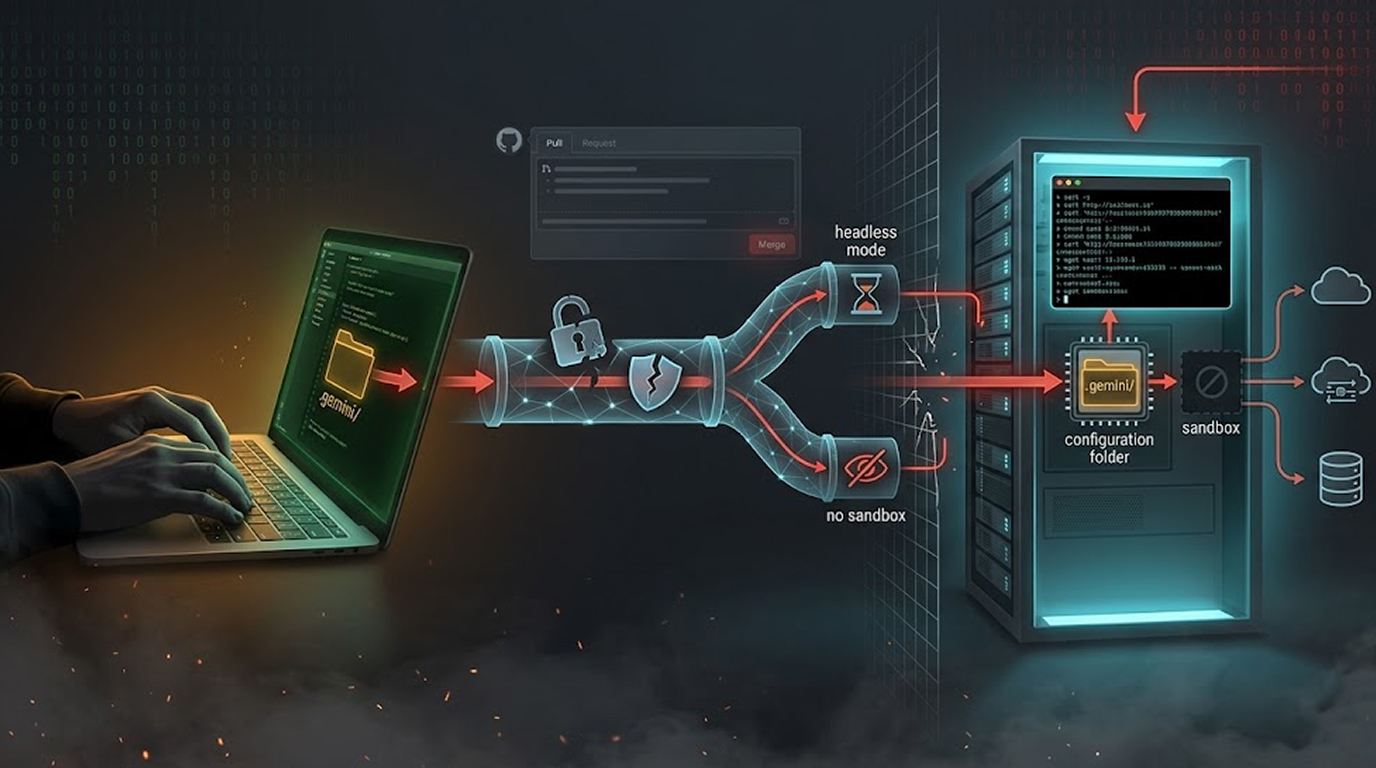
A perfect 10. That is the CVSS score Google assigned to a security flaw in its Gemini CLI tool. And for good reason. The Gemini CLI remote code execution...
The Predator is one of the most sophisticated mercenary spyware platforms still in existence. Initially birthed as a covert monitoring solution for commerc...
Tool calling (also known as function calling or tool use) is one of the most powerful features of modern large language models. It allows autonomous AI age...
SSTI (Server Side Template Injection) is an incredibly hazardous as well as often overlooked method of code injection that has been used against modern web...
North Korean-linked hackers are running a slick, persistent operation that turns the job hunt into a security nightmare for developers. They have created p...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067