App Compromise vs Host Compromise: What Changes
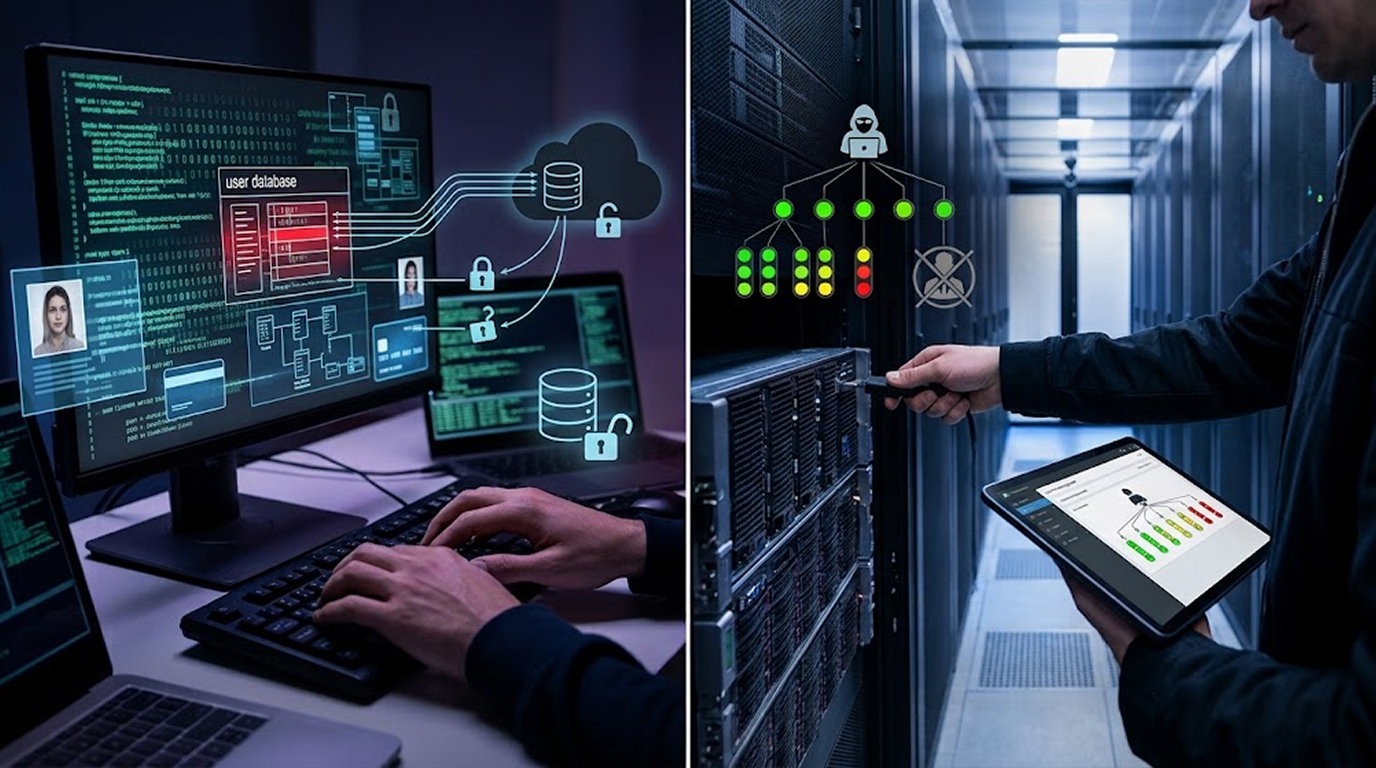
Two incidents can look identical in the alert queue and be entirely different animals underneath, because one of them means somebody read data they shouldn...
Found 246 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Two incidents can look identical in the alert queue and be entirely different animals underneath, because one of them means somebody read data they shouldn...
Attackers are actively exploiting a zero-day SQL injection flaw in Arista's VeloCloud Orchestrator, which is the central management system for VeloCloud SD...
You see the advisory, you see the severity rating, and you think you understand the risk, and then you patch it and move on, and that is where most people...
Your AI gateway might have handed over cloud keys before you ever imported the package, because the popular LiteLLM Python package was compromised in a sof...
Your repository might look clean and still be compromised, because the actor behind GhostAction has moved past injecting workflows entirely, and the new Gh...
Your npm install might have handed a stranger your browser cookies, your wallet files, and a persistent backdoor, because researchers just documented a fak...
Website Malware Removal: The Complete Guide Website malware removal is the process of identifying malicious code on a compromised website, removing infect...
Your AnyDesk deployment on Linux might be accepting root-level commands from strangers, because security researchers just published a full working exploit...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067