PromptSpy: AI Malware Targeting Developers via npm Packages
You have heard about AI being used for good. It helps doctors diagnose diseases. It writes code. It answers customer support questions. Now AI is being us...
Found 33 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You have heard about AI being used for good. It helps doctors diagnose diseases. It writes code. It answers customer support questions. Now AI is being us...
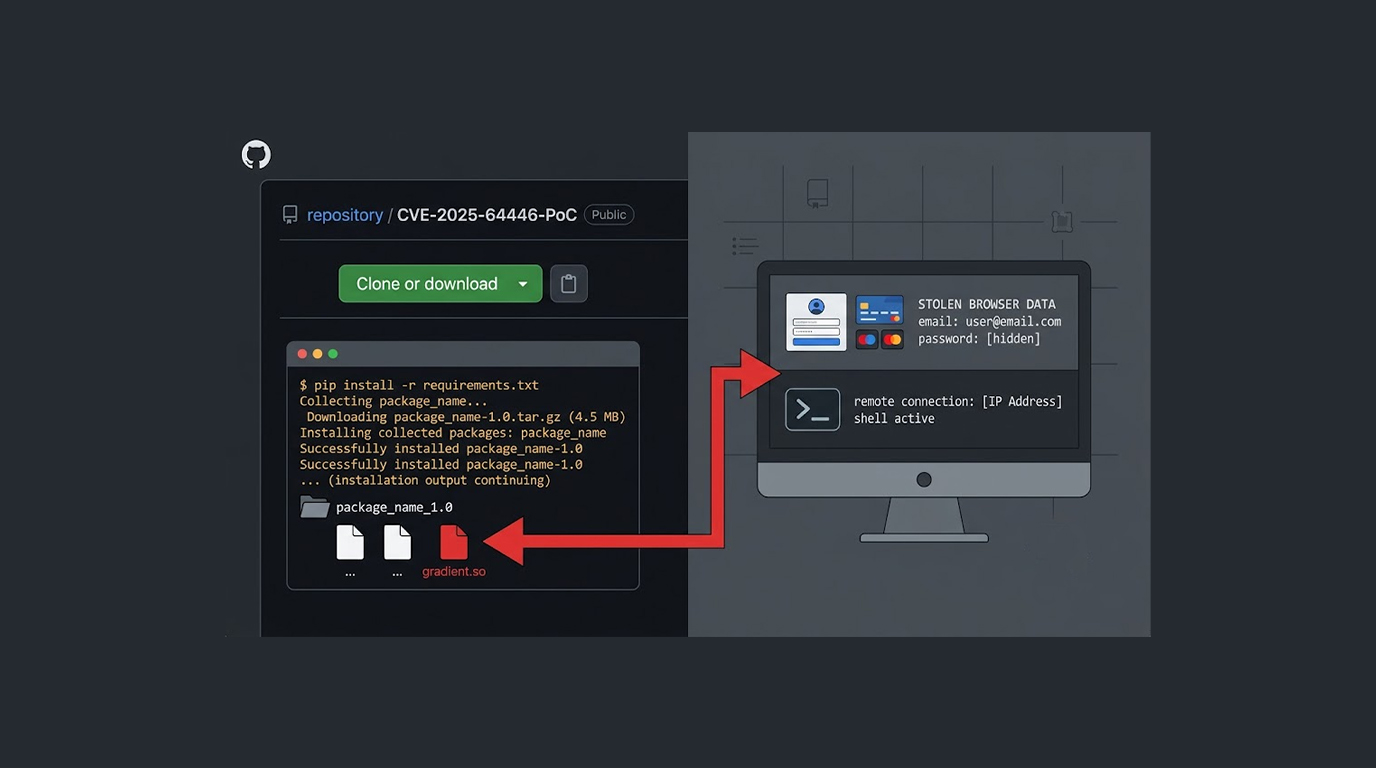
There's a new twist in the ongoing battle between researchers and attackers. Malicious actors are now planting data-stealing malware inside proof-of-concep...
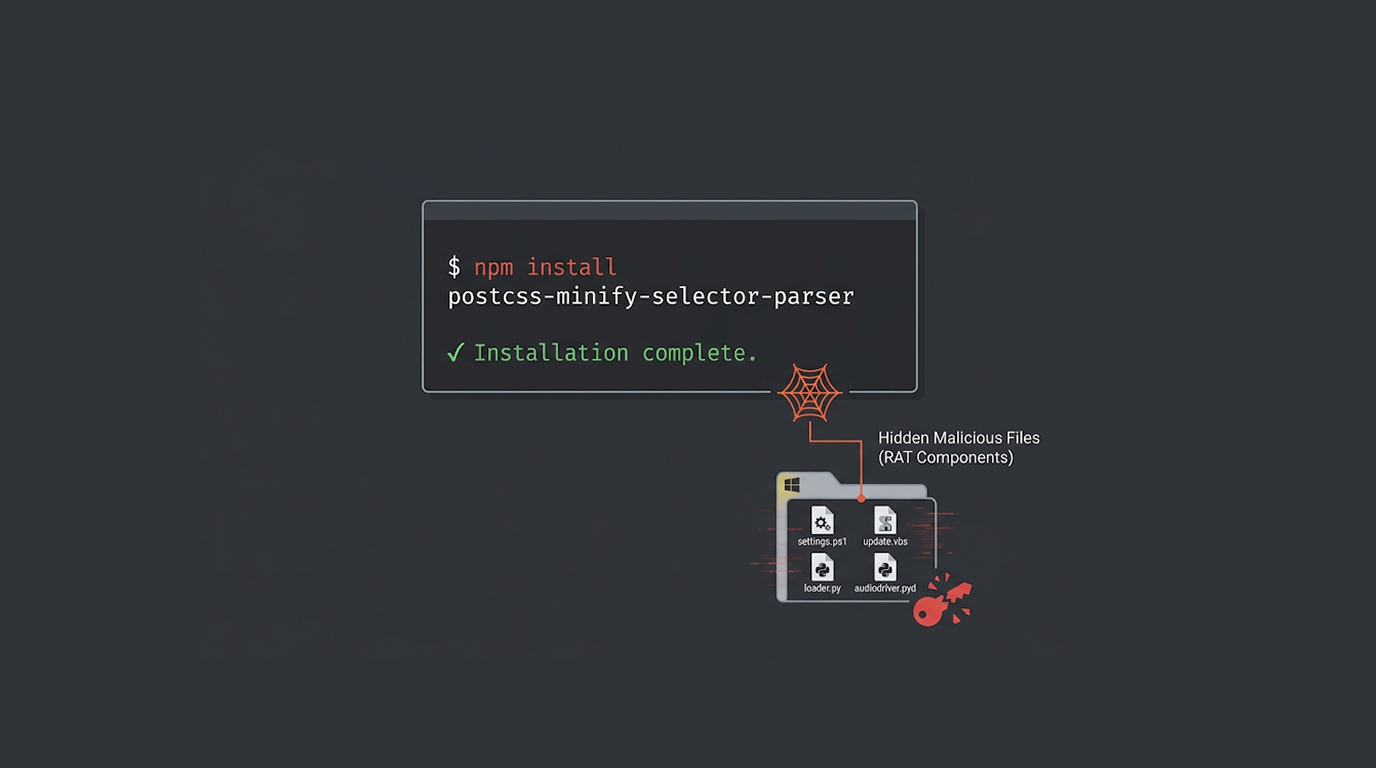
You install a package that looks like a legitimate build tool. It has a name similar to a popular library. It has hundreds of downloads. It seems safe. It...
In just 88 minutes, a single npm account published more than 140 malicious versions of packages in the Mastra namespace. Mastra is a popular open-source Ja...
The Vietnam-aligned threat actor known as OceanLotus has spent more than a decade targeting foreign entities, especially China. But something changed recen...
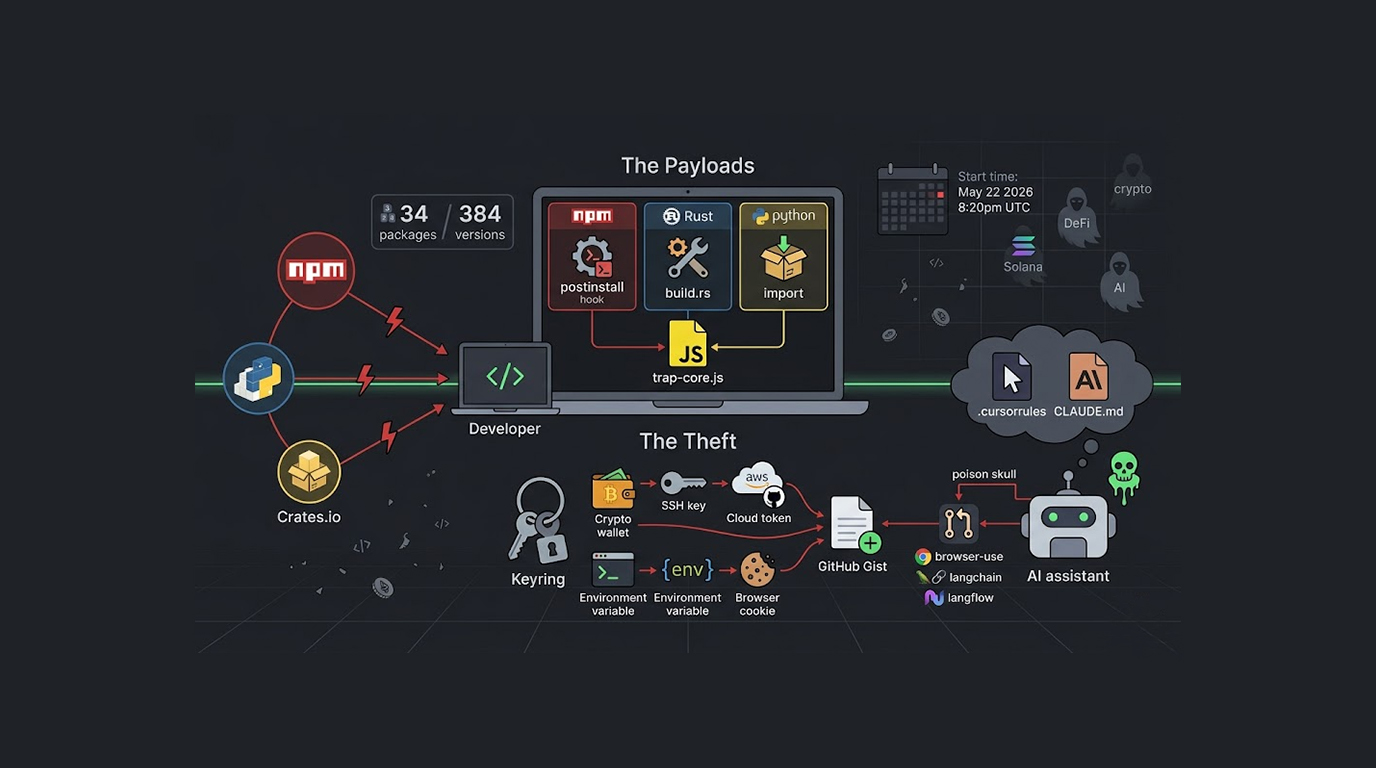
A new coordinated supply chain attack campaign has targeted three major package registries simultaneously, and the attackers are stealing developer credent...
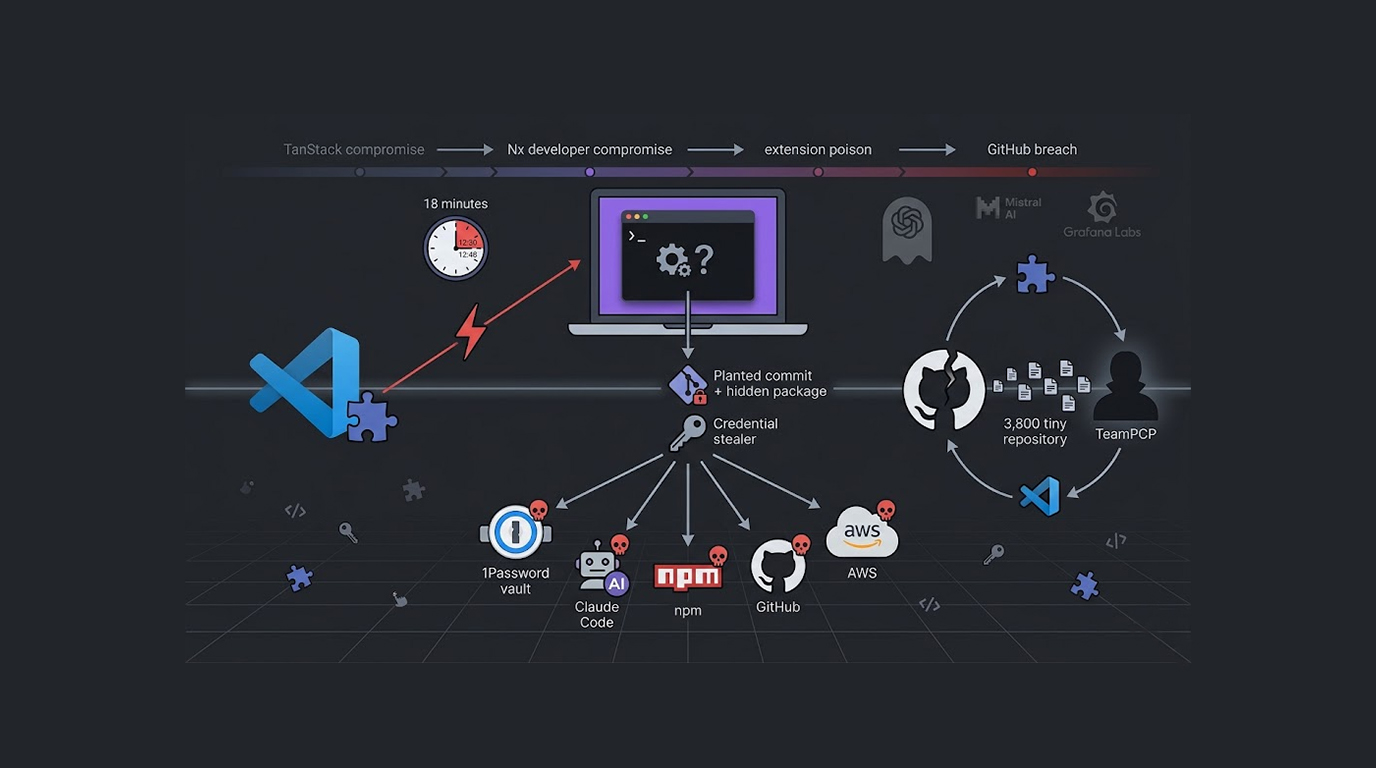
GitHub has officially confirmed that the breach of its internal repositories was the result of a compromised employee device, and the attack vector was a p...
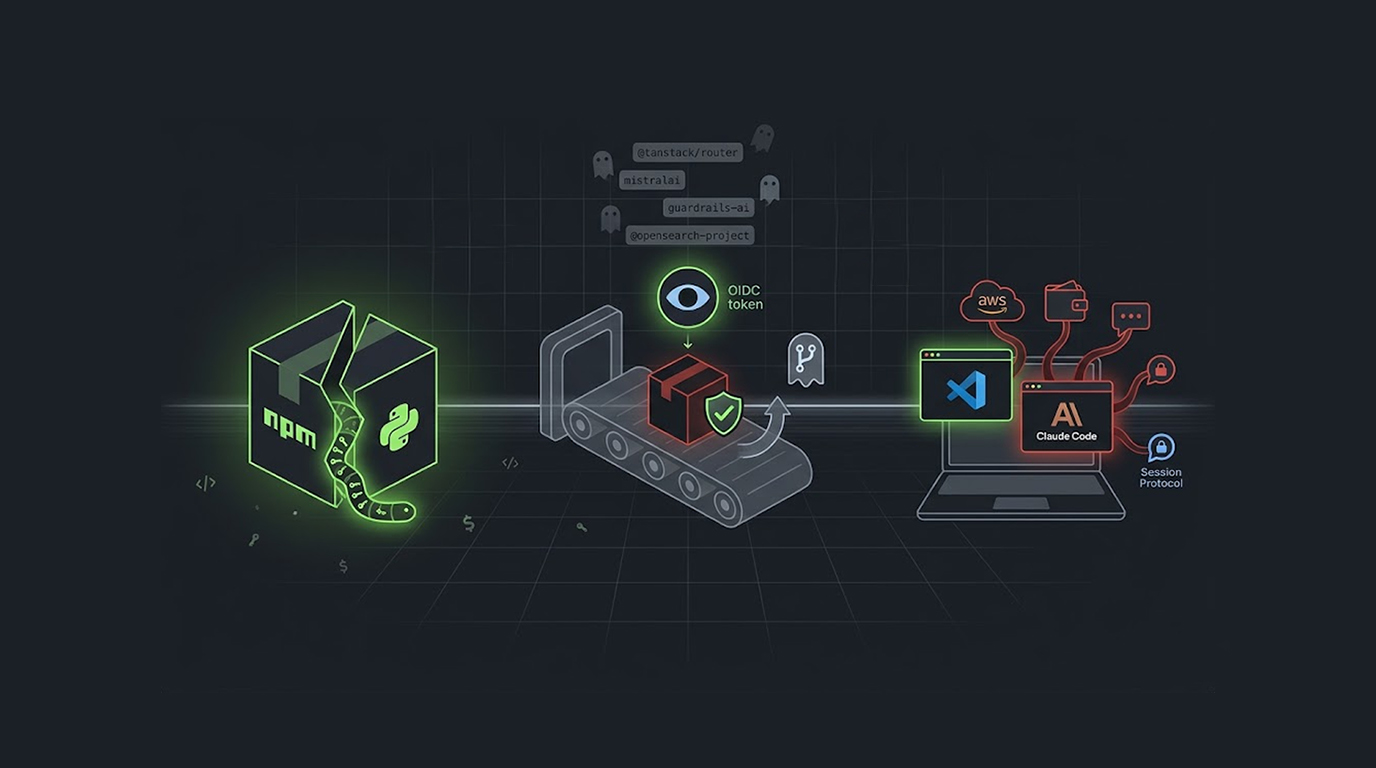
A single worm has spread across both npm and PyPI, it compromised packages from major companies like TanStack, UiPath, Mistral AI, and OpenSearch, and it u...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067