Grok Apps: 35,578 Exposed Without a Login
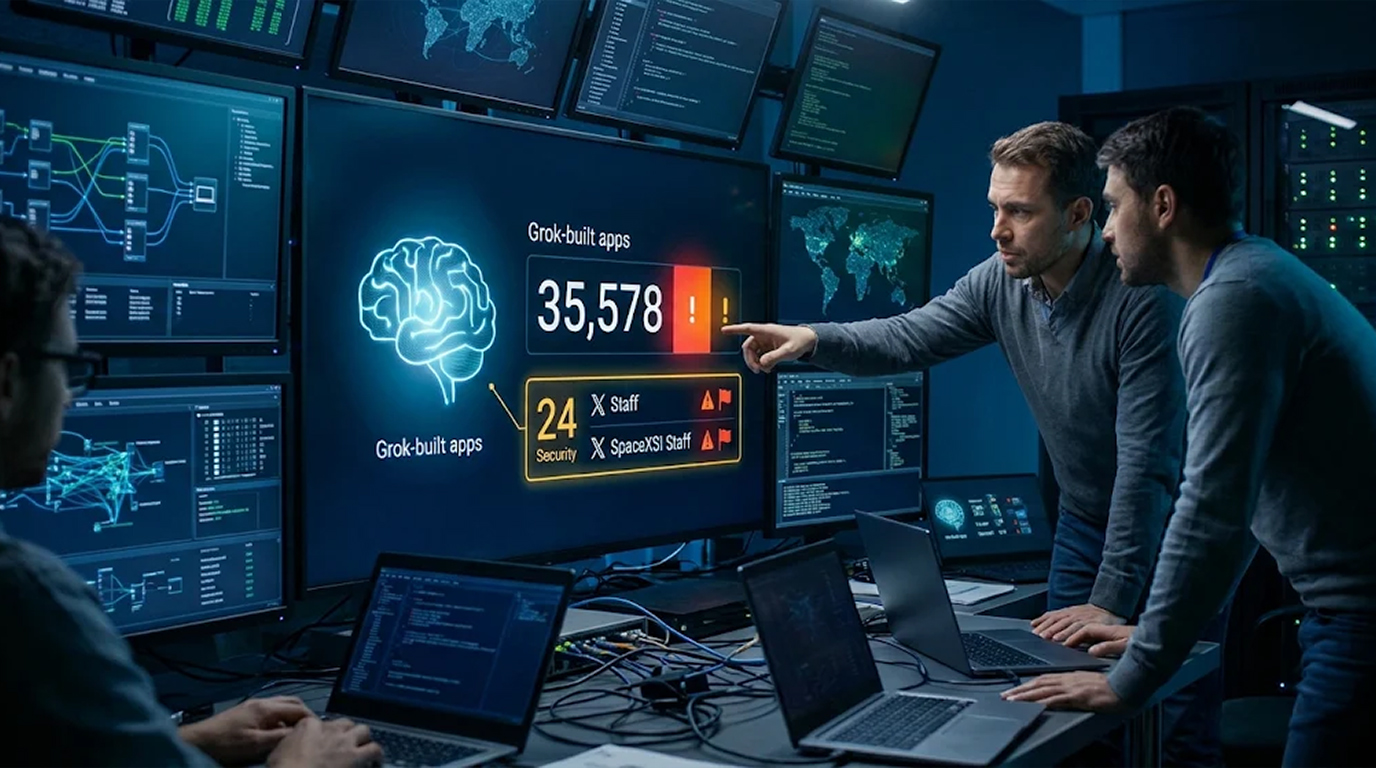
Claroc went looking for Grok-built apps and found 37,571 of them. Of that number, 35,578 were open to anyone without a sign-in. That is not a rounding err...
Found 302 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Claroc went looking for Grok-built apps and found 37,571 of them. Of that number, 35,578 were open to anyone without a sign-in. That is not a rounding err...
Most breaches you read about are loud in the way that matters to defenders, because they involve ransomware, a leak site, a demand, and a countdown, and th...
An attacker broke into AWS accounts belonging to multiple Qubole customers between October 14 and October 26, stealing stored secrets and data. The entry...
There's a design decision at the centre of Claude Desktop that determines everything about its security posture, and it's not a bug or an oversight, it's t...
There's a version of malvertising that's easy to catch, which is the one where a poisoned ad creative reaches everyone who loads the page, and a scanner so...
"Videoconferencing malware" gets used as if it describes a single thing, and it doesn't, because the software in question is abused in at least a dozen dis...
Most Active Directory attacks require credentials, which means the attacker has to steal something first, and that theft is the hard part that gets them ca...
Canonical just patched a maximum-severity flaw in LXD and MicroCloud, because an attacker could log in as a trusted client without ever holding that client...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067