VMware vCenter CVE-2026-59310 Tied to China-Nexus APT
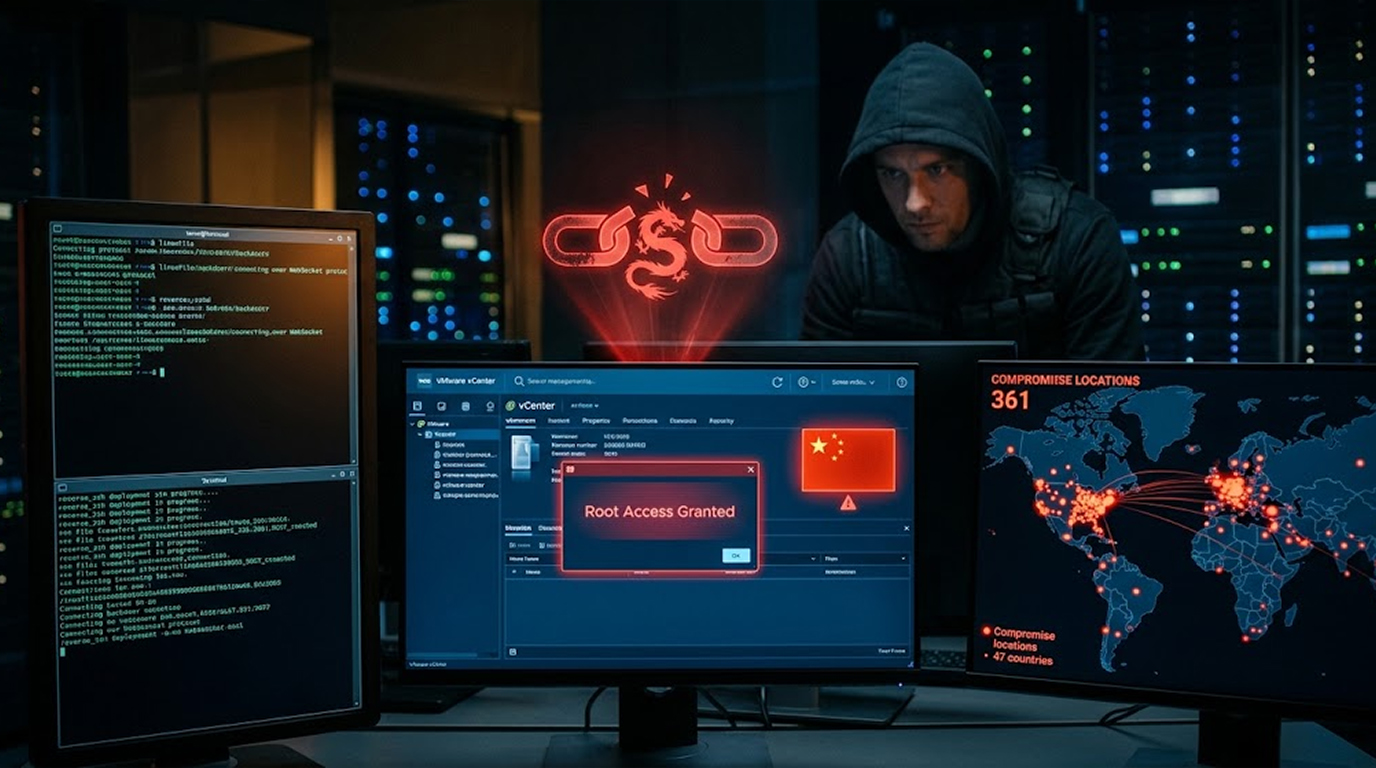
Cybersecurity researchers have linked the exploitation of a recently patched VMware vCenter vulnerability to a suspected Chinese state-sponsored hacking gr...
Found 24 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Cybersecurity researchers have linked the exploitation of a recently patched VMware vCenter vulnerability to a suspected Chinese state-sponsored hacking gr...
A critical unauthenticated remote code execution vulnerability in the JCE extension for Joomla has been exploited. A public proof-of-concept is now availab...
Cybersecurity researchers have warned of a supply chain compromise impacting WordPress plugin vendor BdThemes. The incident prompted the WordPress plugins...
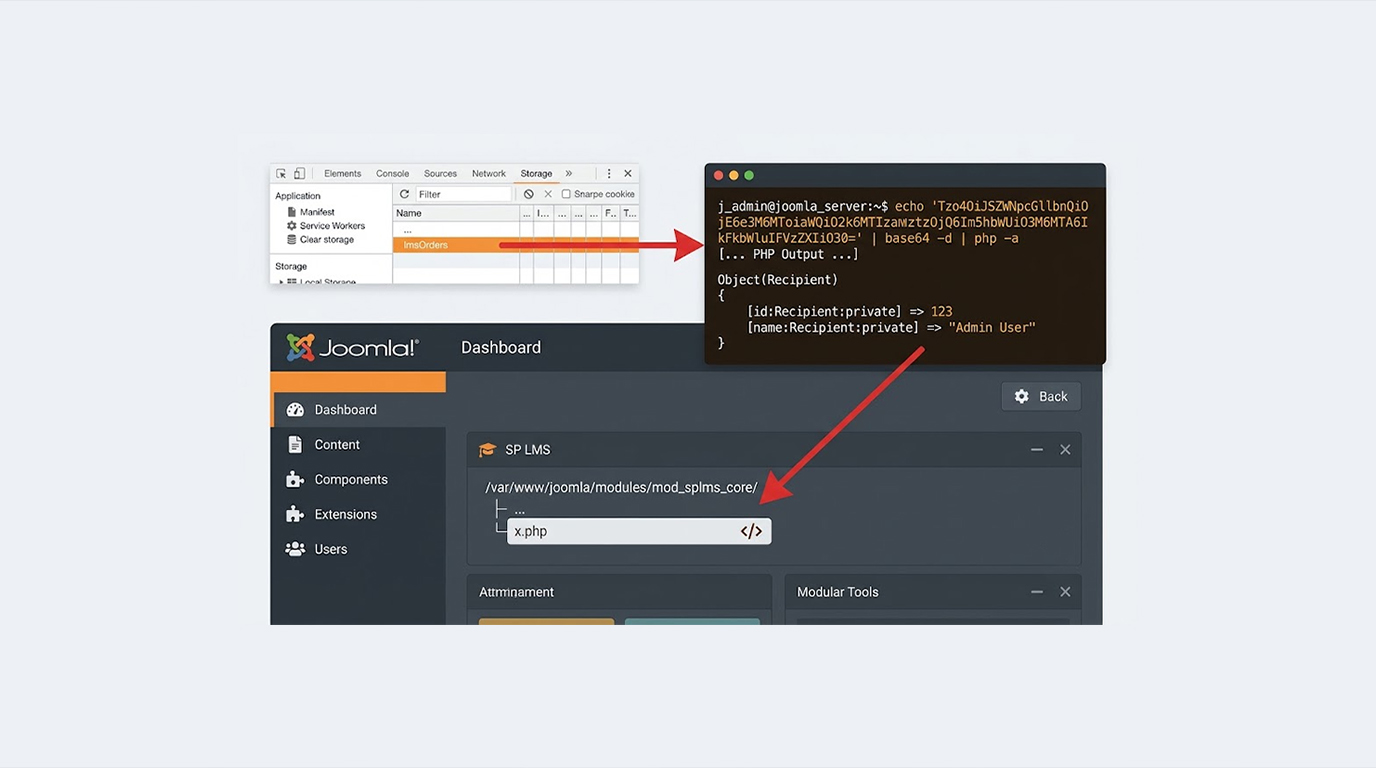
Joomla extension JoomShaper SP LMS contains an object injection vulnerability leading to remote code execution for the attacker. This vulnerability is iden...
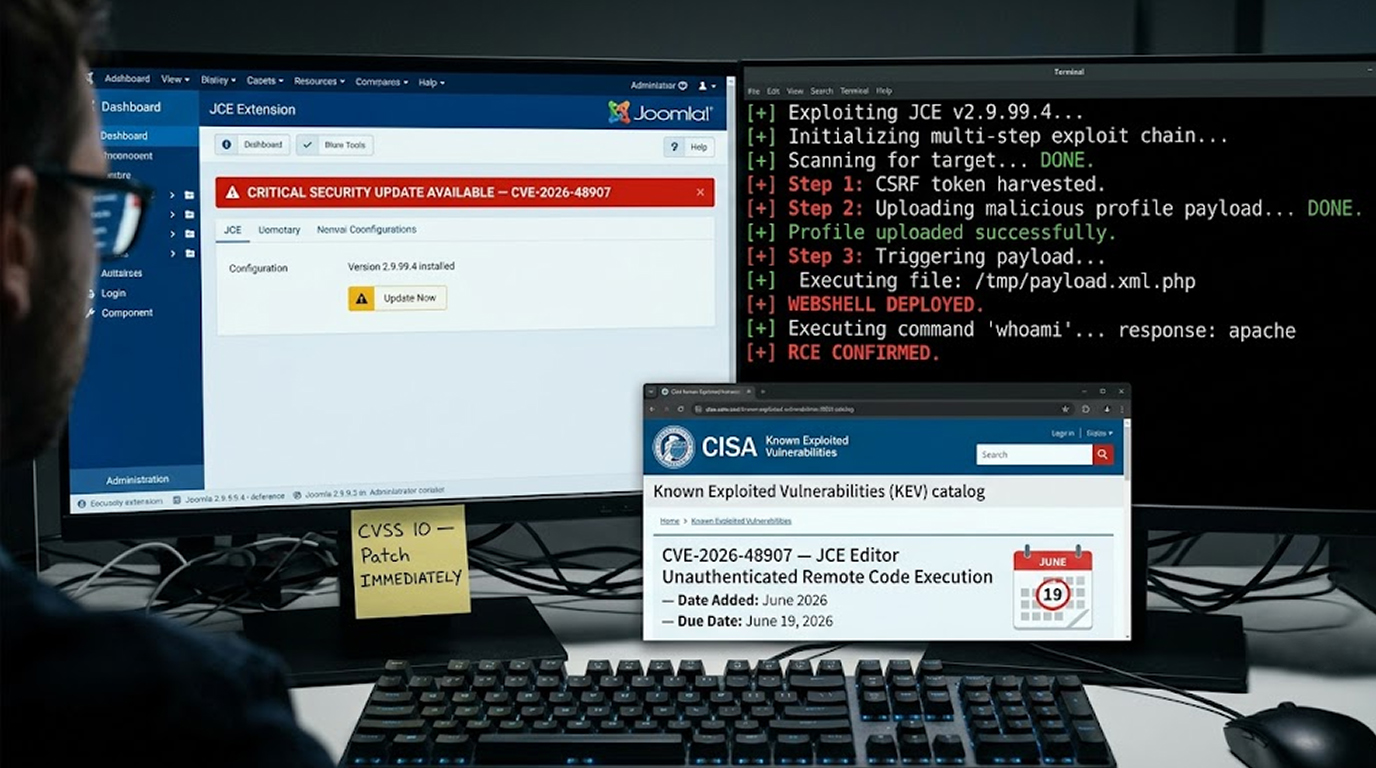
The U.S. Cybersecurity and Infrastructure Security Agency just added a maximum-severity flaw to its Known Exploited Vulnerabilities catalog. Federal agenci...
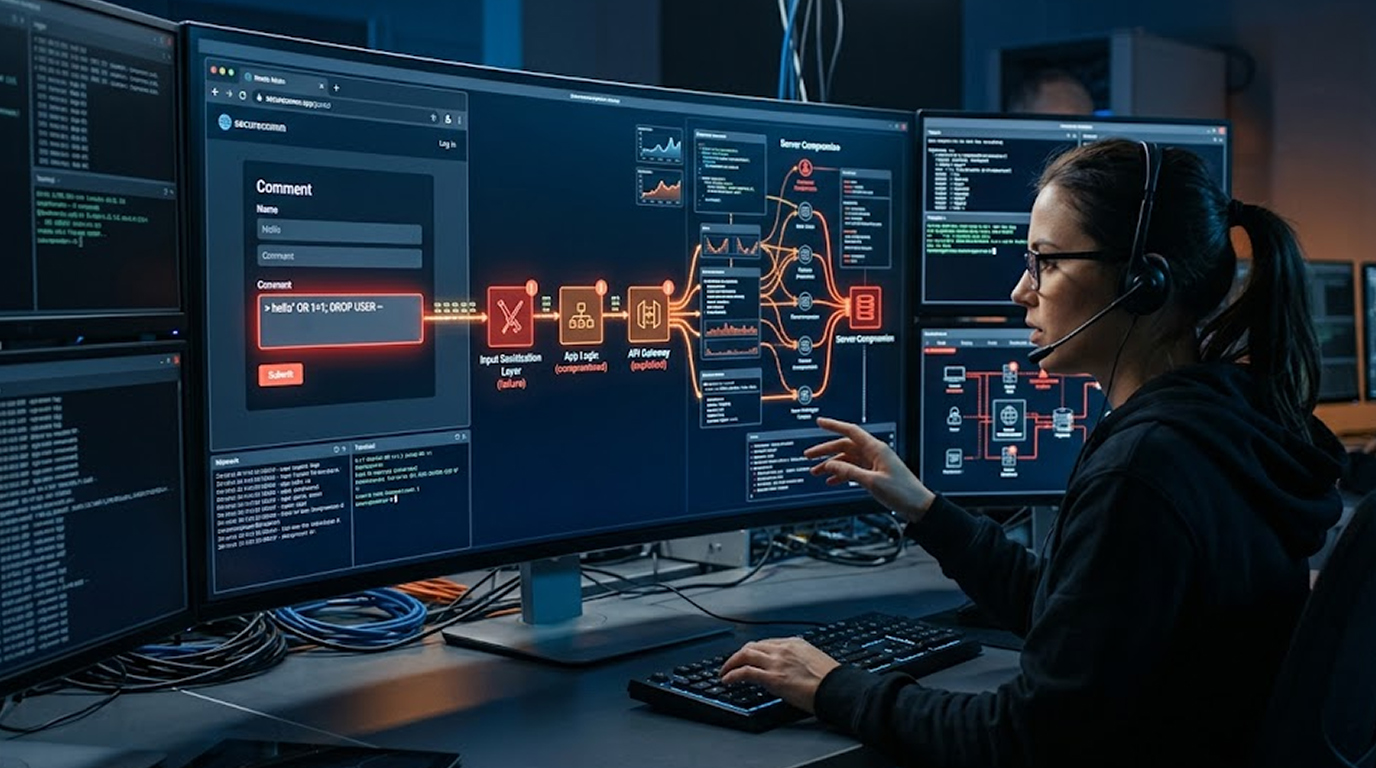
While the comment box may appear to be a benign feature of a website (i.e., a place for users to submit their feedback), at its core, it can become an entr...
As of 2026, webshells still rank among the most consistent methods attackers use to retain persistent access once they achieve RCE for the first time. Alth...
In 2026, a surprisingly large number of web servers (especially legacy PHP apps, shared hosting environments and misconfigured cloud instances) still leave...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067