Quasar Linux RAT Steals Developer Credentials for Supply Chain Attacks
A developer sits down at their Linux workstation, pushes code, publishes packages, and manages cloud infrastructure, but they have no idea that every keyst...
Found 25 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A developer sits down at their Linux workstation, pushes code, publishes packages, and manages cloud infrastructure, but they have no idea that every keyst...
A video game platform used by ethnic Koreans living along China's border with North Korea has been compromised. The attackers? A North Korean state-sponsor...
A Chinese cybercrime group is pretending to be tax authorities in two different countries. Their goal? Deliver malware that steals data, controls systems,...
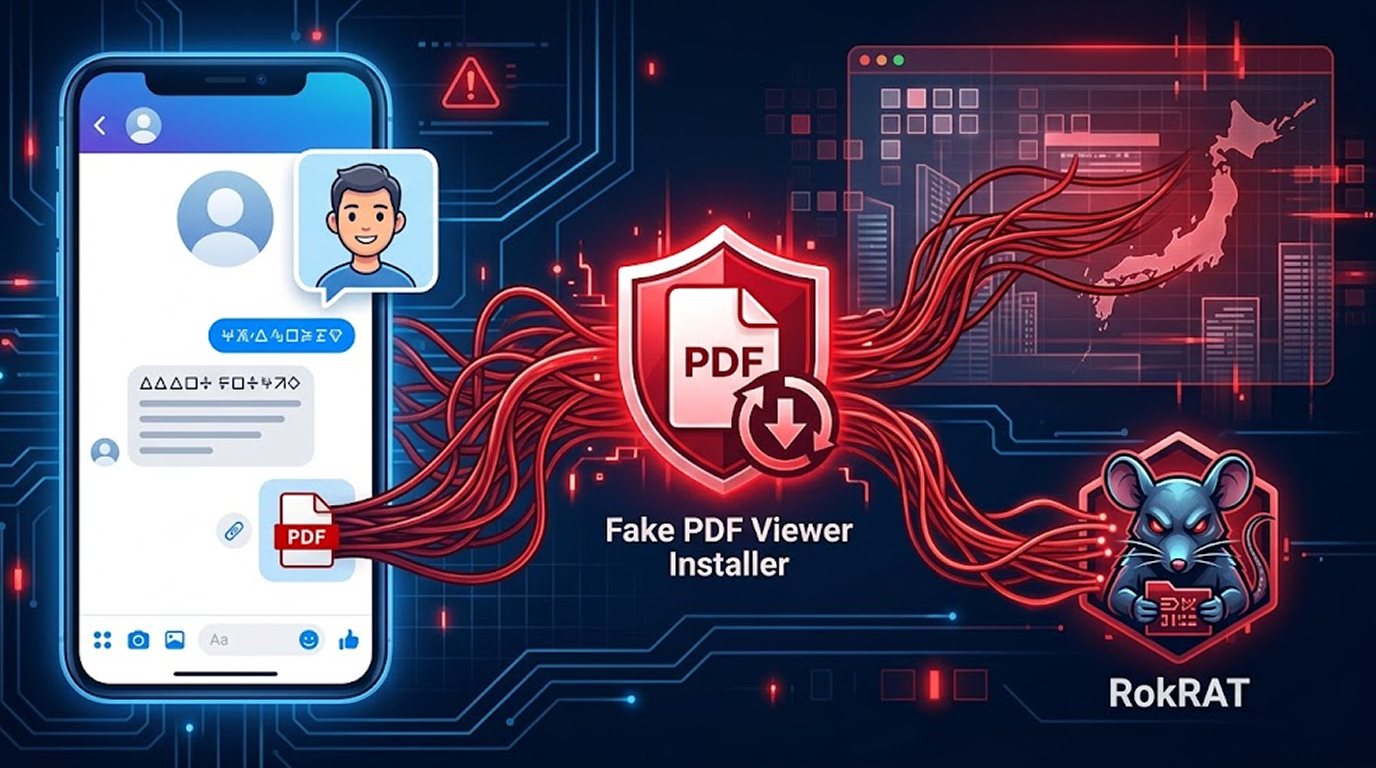
The North Korean hacking group known as APT37 (also called ScarCruft) has been linked to a targeted social engineering campaign that uses Facebook to deliv...
New malware called STX RAT was discovered as the first RAT to be able to use invisibility techniques and perform a variety of operations. This was first se...
Cybersecurity firm Socket has uncovered a targeted supply-chain compromise hitting the official client libraries for dYdX v4, the decentralized perpetuals...
The North Korean threat actor known as Konni has been linked to a new phishing campaign that uses AI-generated PowerShell malware to compromise developers...
Threat group UAT-7290, which has been tracked by Cybersecurity Researcher Cisco Talos, is comprised of suspected Chinese state-sponsored actors and targets...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067