Dangling-Byte Attack: New OWASP Threat Changes Web Security
This is one way an attacker can use to exploit websites. The dangling-byte technique is a new and innovative approach to HTTP desync that enables an attack...
Found 40 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
This is one way an attacker can use to exploit websites. The dangling-byte technique is a new and innovative approach to HTTP desync that enables an attack...
You have probably heard about prompt injection. It is the vulnerability that keeps security teams up at night. It is the number one risk on the OWASP Top 1...
Security breaches are making headlines daily. From major corporations to small businesses, no organization is immune. Yet many business owners remain confu...
You have a web app that you want to test. Maybe it is a customer portal, an API, or a full-blown SaaS platform. You know you need a security tool, but the...
You've now heard of SQLmap, and now you want to try it out for yourself. This tool is definitely powerful, and you would like to see how it works. However,...
You finally did the right thing, you hired a penetration testing firm to find security holes before the criminals do.You expected a few minor issues, maybe...
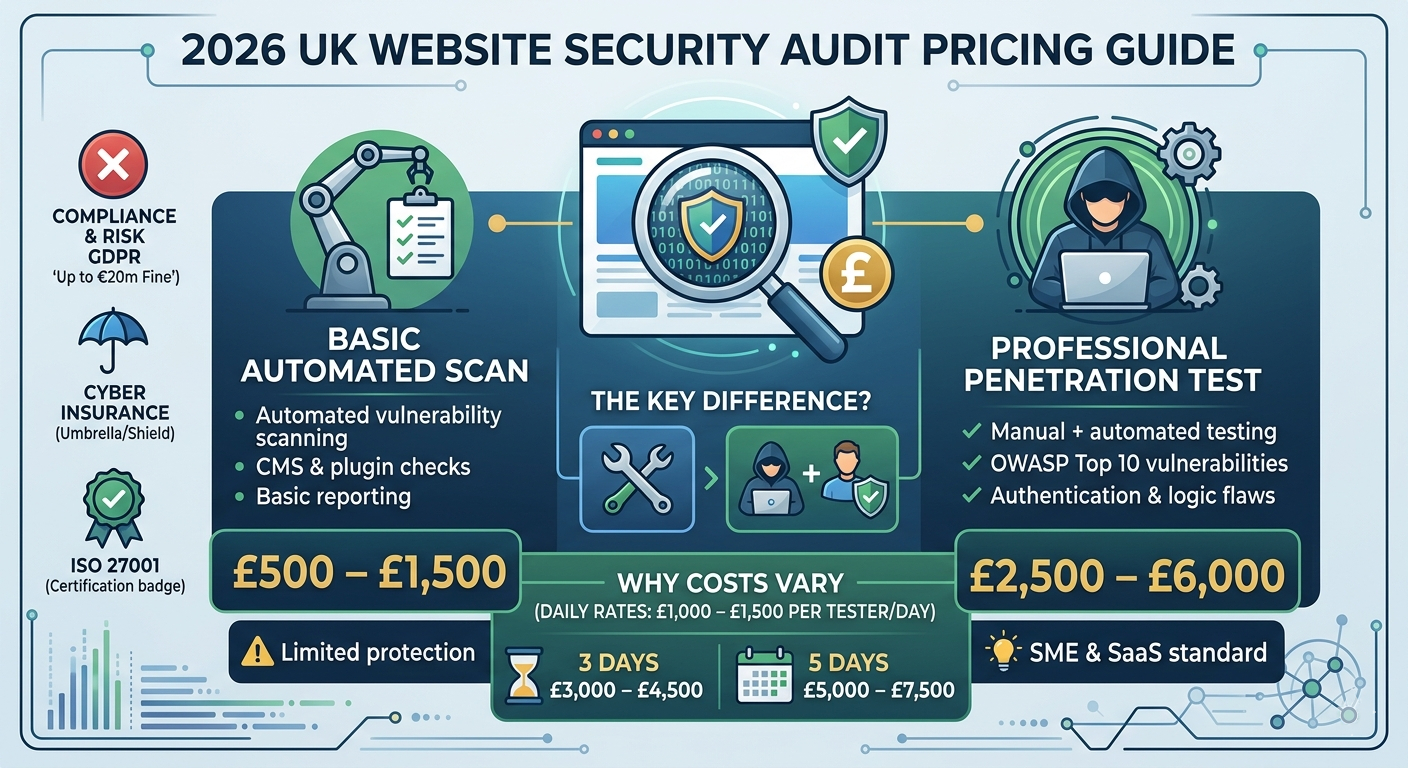
If you're researching website security audit cost in the UK, you’ve probably noticed something confusing: Some providers charge £500… o...
As the cybersecurity industry continues to advance at an accelerated pace, new vulnerabilities pose increased potential for both rewards and risk by being...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067