LockBit Affiliates Attacks Explained
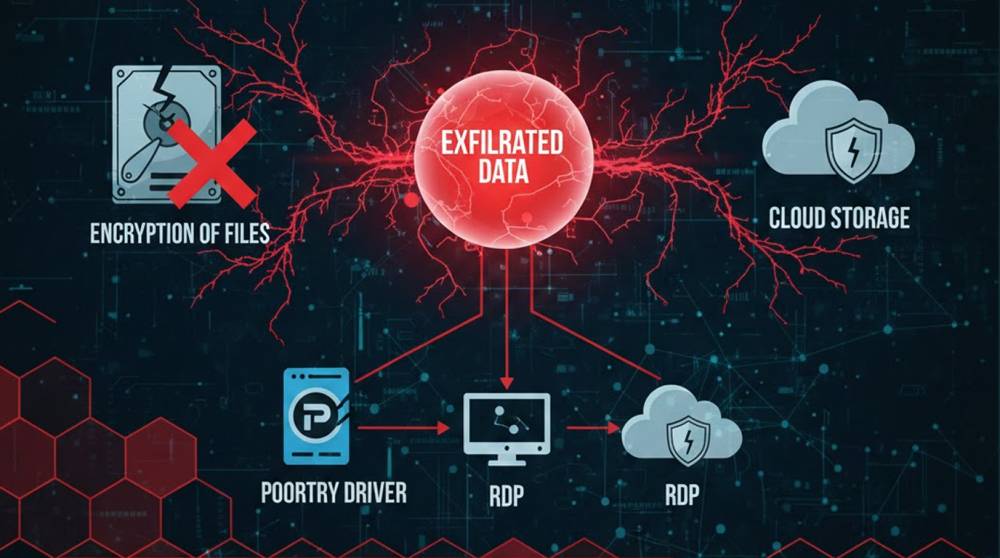
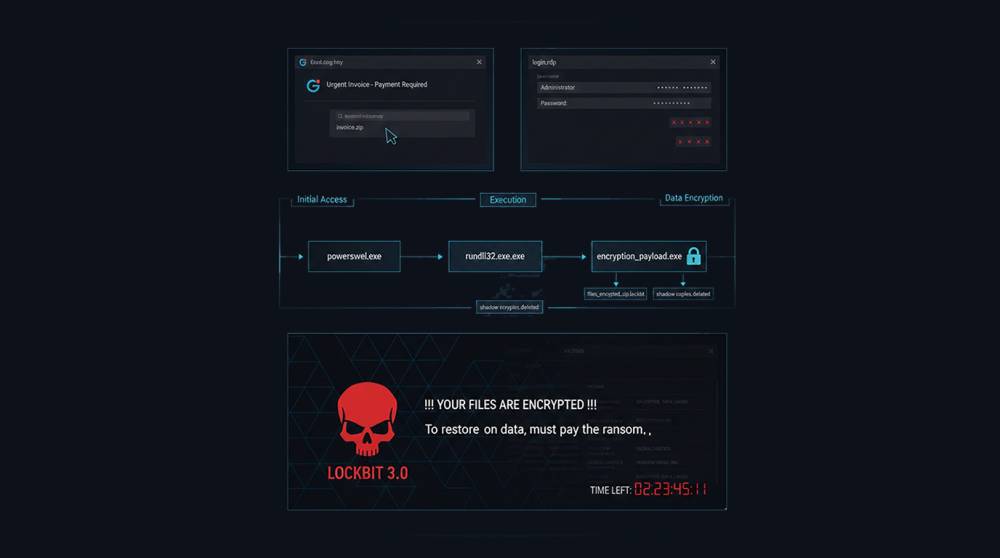
LockBit is (or was) the most active and profitable ransomware-as-a-service (RaaS) operation in recent years. The group provides the LockBit ransomware buil...
Found 23 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
LockBit is (or was) the most active and profitable ransomware-as-a-service (RaaS) operation in recent years. The group provides the LockBit ransomware buil...
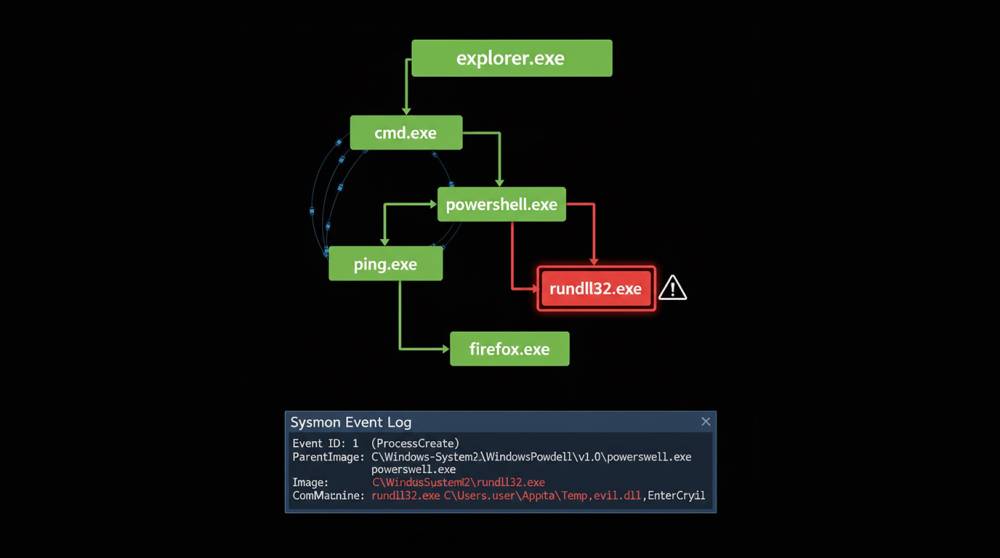
Process ancestry monitoring tracks the parent-child relationships between processes (who spawned what). This is one of the most reliable ways to detect liv...
Atomic Red Team is an open-source library of small, focused tests mapped to the MITRE ATT&CK framework. These tests simulate real adversary behaviors t...
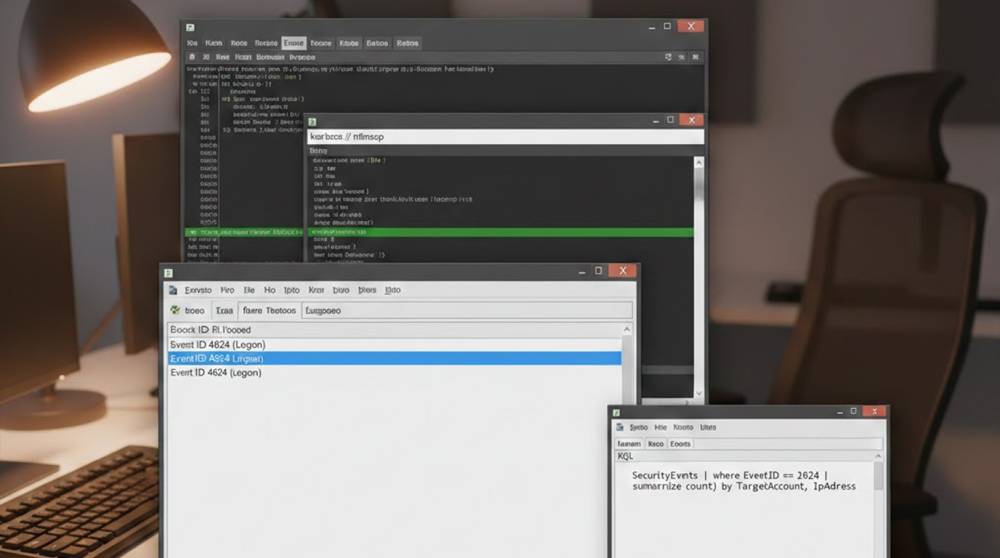
An example of unauthorized network authentication is when an attacker logs into your Wi-Fi, VPN, Active Directory, RDP, SSH, cloud console or any other ser...
The latest version of ransomware known as Osiris has been reported by Security research firm Crowdstrike after a Southeast Asia-based operator of multiple...
A Red Team not only tests the defenses of the organization during the engagement; however, a well-executed Red Team will also expose:1. The gaps in the mon...
Most serious incidents do not begin with malware or exploits.They begin with a valid login.Once attackers authenticate, their objective changes.The questio...
Imagine someone breaks into one of your computers. Instead of trying to hack other accounts one by one, they do something smarter: they take the credential...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067