PHP2Shell Flaw: Critical PHP RCE Patch Now
Your server might be running a language runtime that can be exploited by anyone who sends the right request, because PHP just released emergency updates fo...
Found 76 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Your server might be running a language runtime that can be exploited by anyone who sends the right request, because PHP just released emergency updates fo...
Your SuiteCRM install might be acting as a proxy for someone else's reconnaissance, because a public proof of concept now shows how an authenticated user c...
You search for a piece of software you need, you scan the page, you click the first result because it looks official, and you land on a page that asks you...
You come back to your desk, and every screen shows the same message, a black window with red text telling you that your files are encrypted and that you ha...
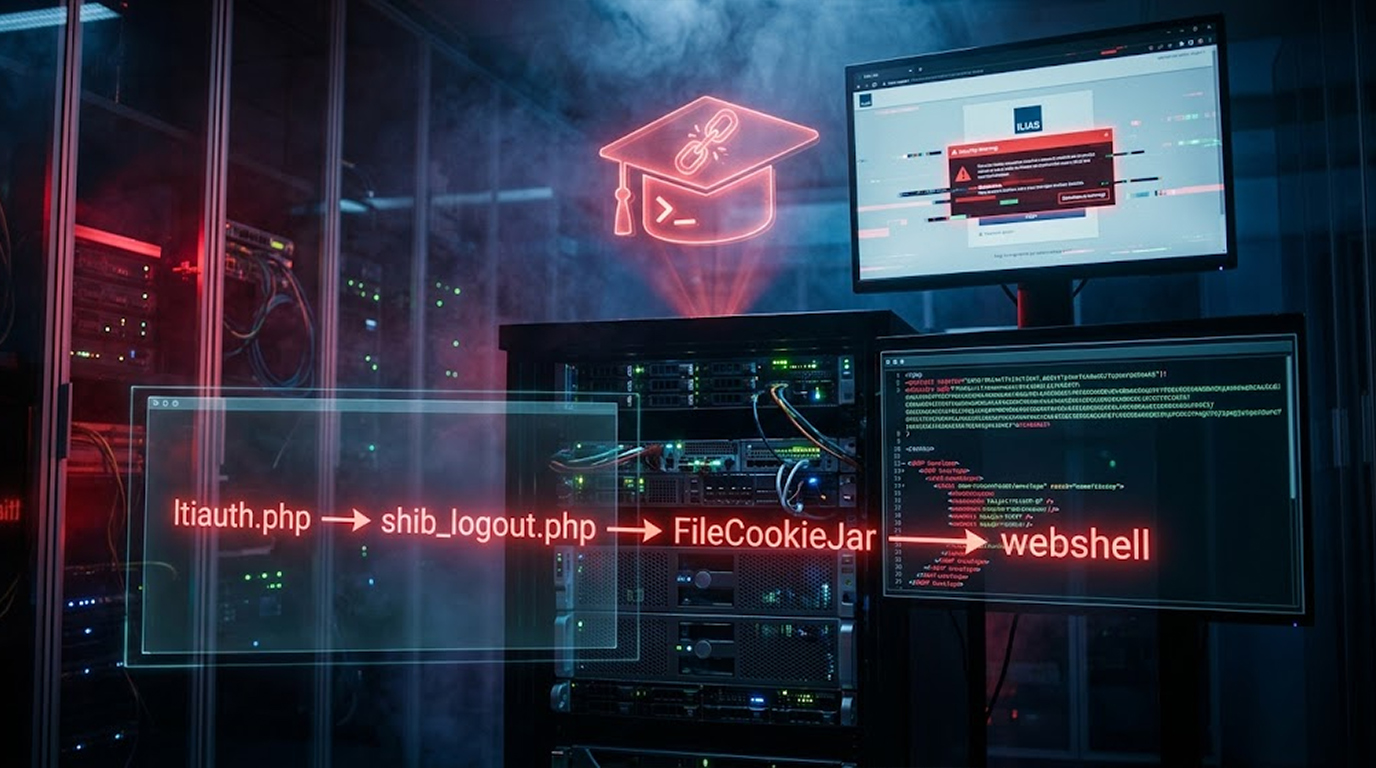
Here's a fun one. ILIAS has two endpoints that don't require authentication. One of them writes to your session. The other one reads your session back and...
There's a bug in FreePBX that lets someone walk in without a login, drop a cron job, and get a shell on your server. No username. No password. Just a web r...
You spend millions on identity protection. Multi-factor authentication. Zero-trust architecture. Password policies. You feel secure. Then an attacker comp...
A server-side request forgery vulnerability has been discovered in Apache Gravitino. The flaw affects versions 1.0.0 through 1.2.1 and allows authenticated...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067