Malicious npm Packages Spread Worm-Like Stealer & RATs
Cybersecurity firm Socket has uncovered an active supply-chain worm campaign codenamed SANDWORM_MODE that abuses at least 19 malicious npm packages to harv...
Found 287 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Cybersecurity firm Socket has uncovered an active supply-chain worm campaign codenamed SANDWORM_MODE that abuses at least 19 malicious npm packages to harv...
Banner grabbing is one of the oldest tricks in reconnaissance, and in 2026 it remains ridiculously effective, especially on internet-facing servers. You li...
According to a joint report by the Google Mandiant and Google Threat Intelligence Group, a suspected China-related threat cluster identified as "UNC6201" h...
According to Microsoft, an innovative tactic is being used by legitimate companies to take advantage of AI chatbots, called AI Recommendation Poisoning. Th...
We’ve entered the phase where the most interesting (and dangerous) cyber conflicts are no longer human hacker vs. human defender. They’re incre...
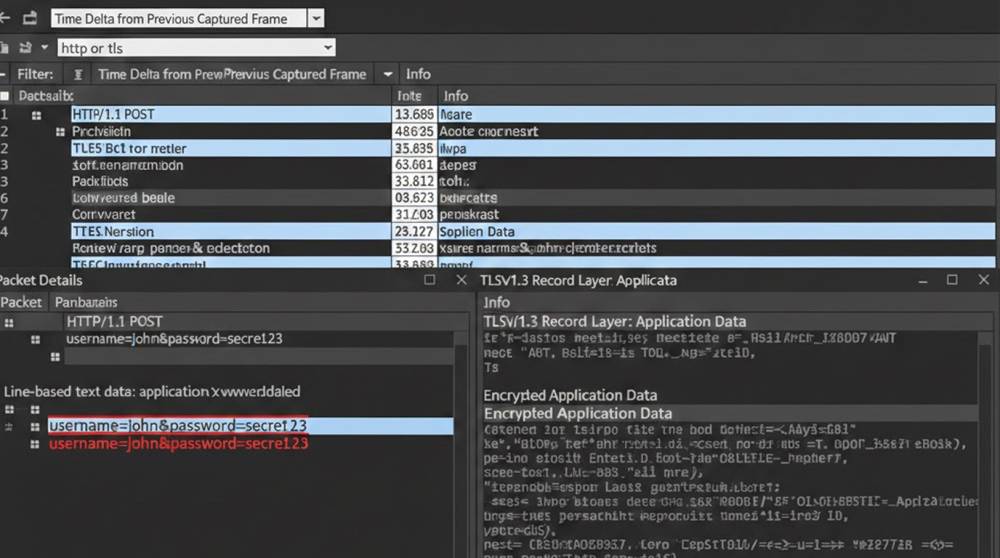
When you capture network traffic with Wireshark, the difference between plaintext (HTTP) and encrypted (HTTPS/TLS) becomes very obvious and very usef...
Two-factor authentication (2FA) is one of the strongest everyday protections we have , it makes stolen passwords alone useless. But attackers have develope...
These three vulnerabilities are among the most common ways attackers break into web applications. They all happen through normal-looking HTTP GET or POST r...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067