ILIAS Unauthenticated PHP Object Injection Leads to RCE
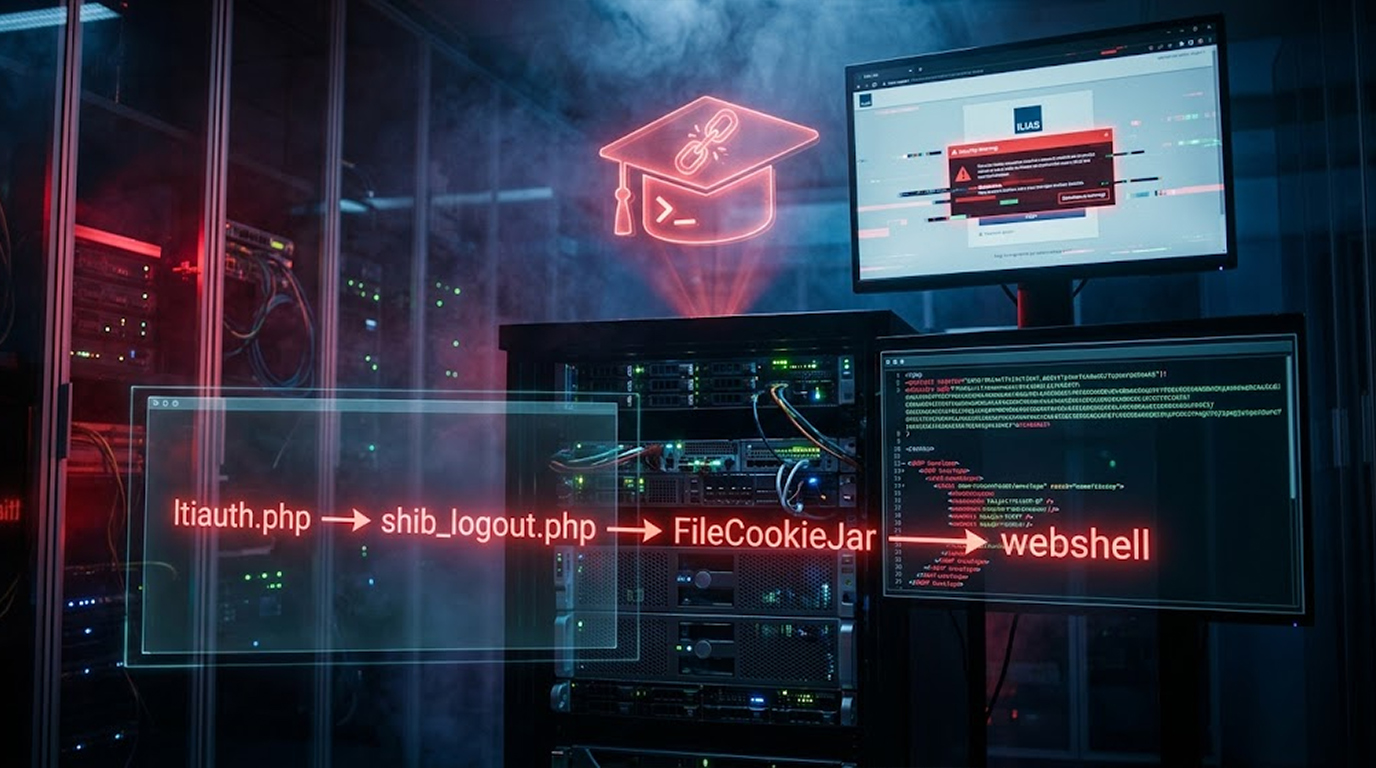
Here's a fun one. ILIAS has two endpoints that don't require authentication. One of them writes to your session. The other one reads your session back and...
Found 1023 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Here's a fun one. ILIAS has two endpoints that don't require authentication. One of them writes to your session. The other one reads your session back and...
There's a bug in FreePBX that lets someone walk in without a login, drop a cron job, and get a shell on your server. No username. No password. Just a web r...
Metabase has a problem. A user with an account and permission to run native queries can execute operating system commands on the server. That's not a typo....
If you run PodcastGenerator on your website, you need to pay attention. Here's the deal. Someone with admin access can type JavaScript into a Live Item. T...
Remember that "major malicious attack" on RubyGems back in May? The one where hundreds of junk packages flooded the registry and forced maintainers to susp...
Anthropic just dropped a 154-page report that should make anyone in security sit up straight. Between December 2025 and August 2026, cybercriminals and sta...
You receive a phone call. The voice on the other end sounds exactly like your grandson. He is scared. He says he is in trouble and needs money fast. You pa...
Your endpoint detection and response tool is running. It is watching for malicious behavior. It is blocking known attacks. You feel protected. Then an att...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067