Hotel Phishing Campaign Drops TonRAT Node.js Malware
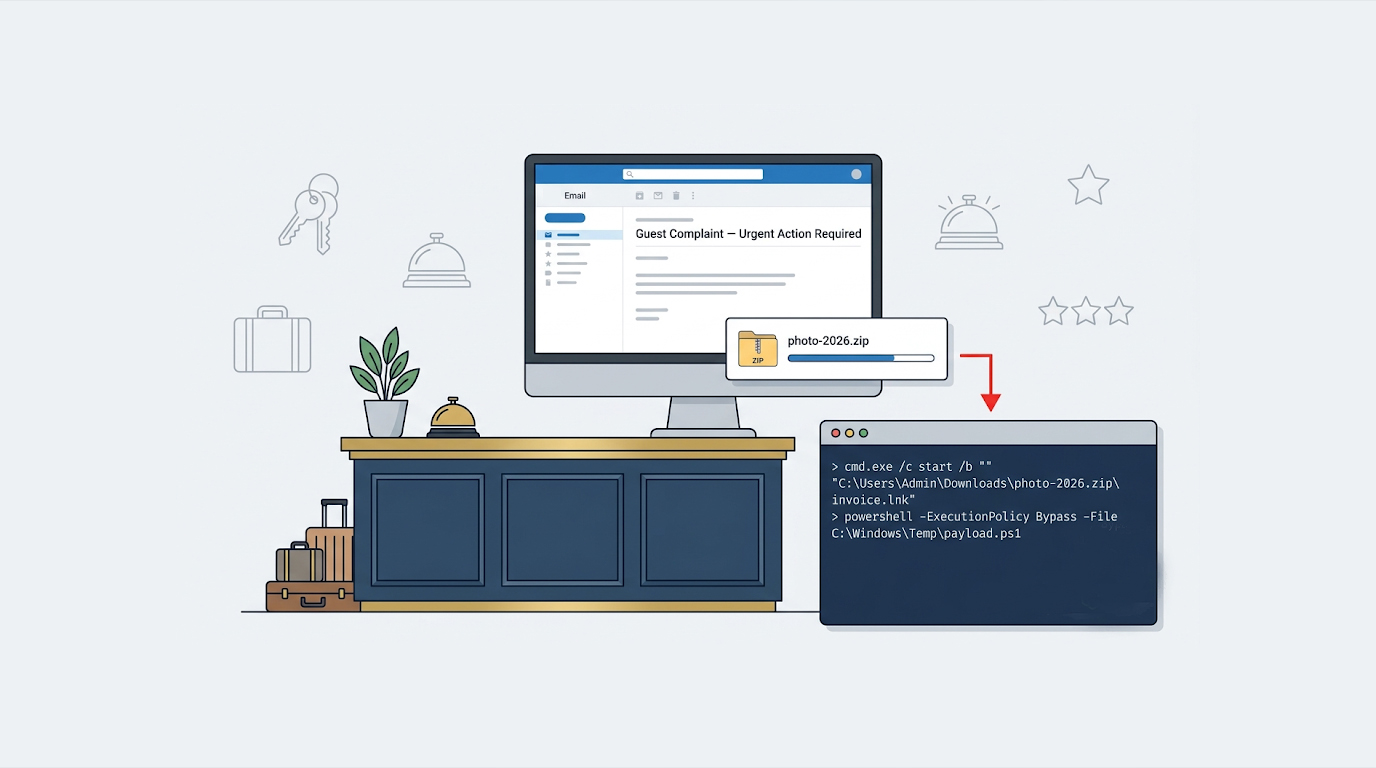
Your front desk receives an email. It looks like it came from Calendly. The display name says "Booking Manager." The subject mentions a guest complaint. Th...
Found 427 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Your front desk receives an email. It looks like it came from Calendly. The display name says "Booking Manager." The subject mentions a guest complaint. Th...
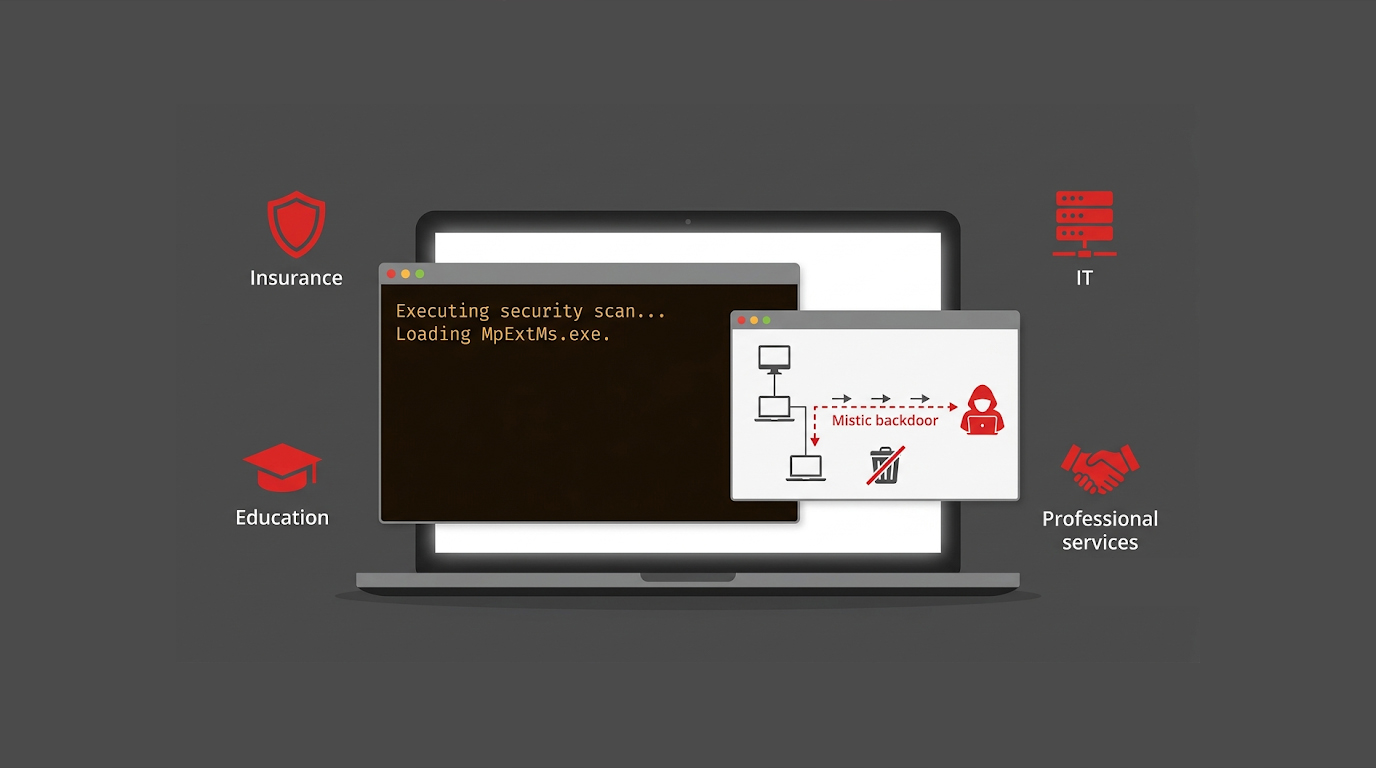
The latest stealth backdoor which has been used to conduct an attack with financial gains as the main objective since April 2026 in various industries has...
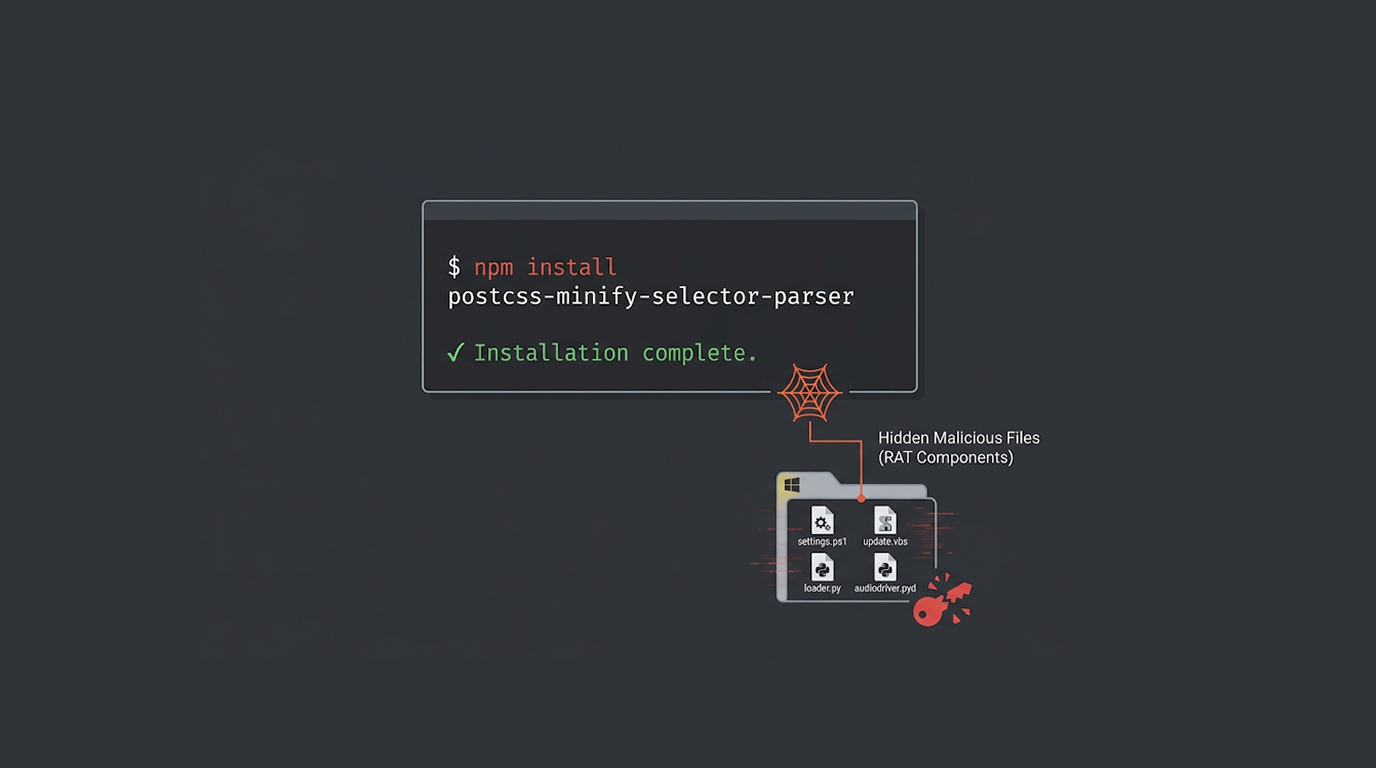
You install a package that looks like a legitimate build tool. It has a name similar to a popular library. It has hundreds of downloads. It seems safe. It...
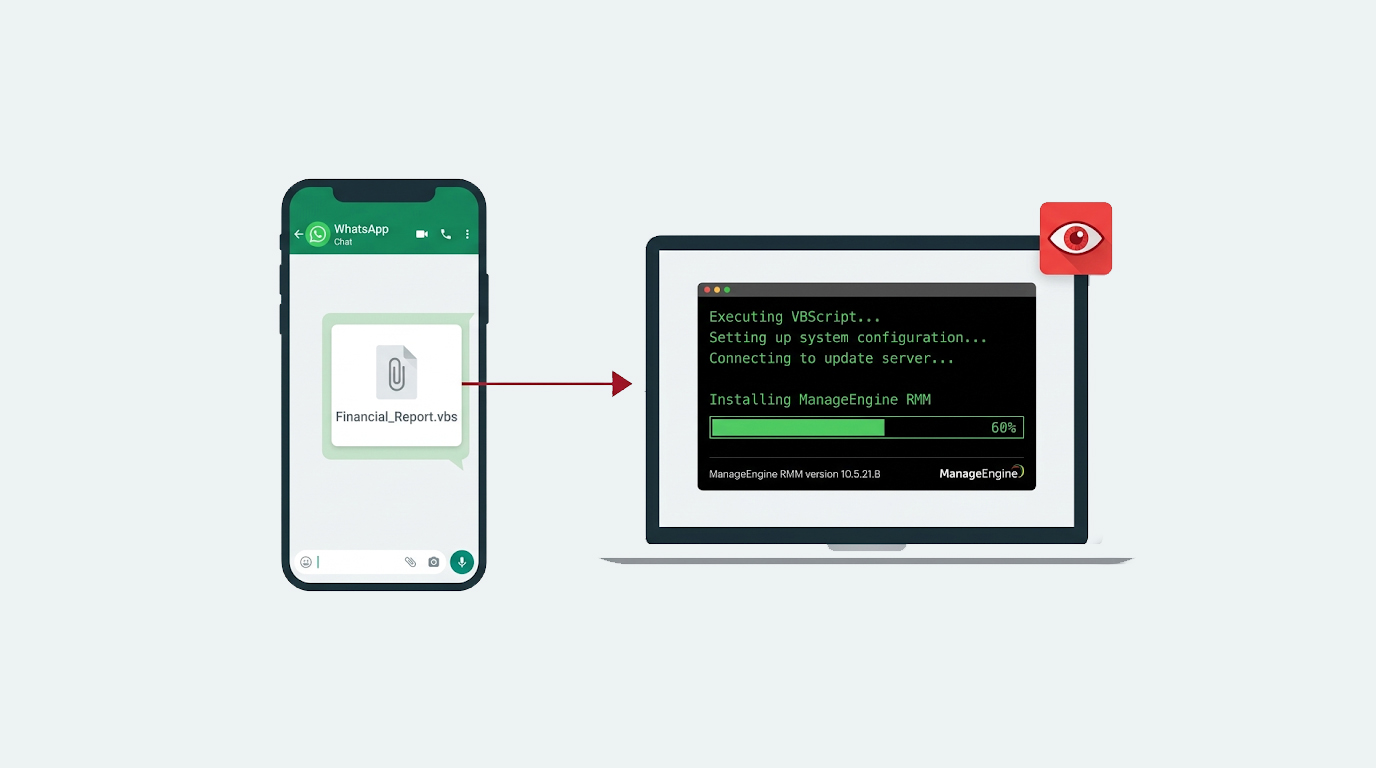
You receive a WhatsApp message from a contact you know. It includes an attachment named "Financial Reports.vbs." They don't explain what it is. They don't...
You are on a penetration test. You find a vulnerability in a web application. You execute a command on the target server. Now you need a way to control tha...
You have a web app that you want to test. Maybe it is a customer portal, an API, or a full-blown SaaS platform. You know you need a security tool, but the...
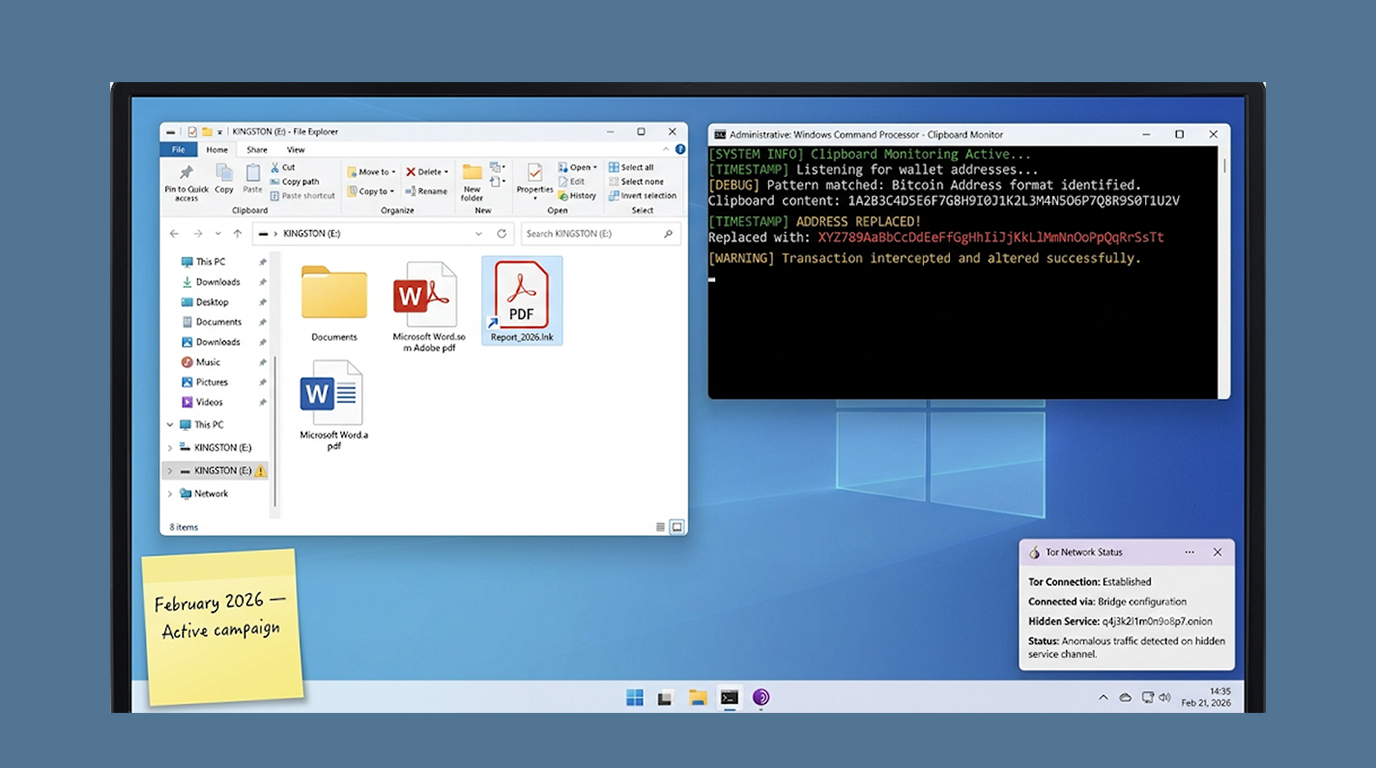
In a new report from Microsoft, window-based cryptocurrency clipper campaign, running since February 2026, has been disclosed. The malware intercepts clipb...
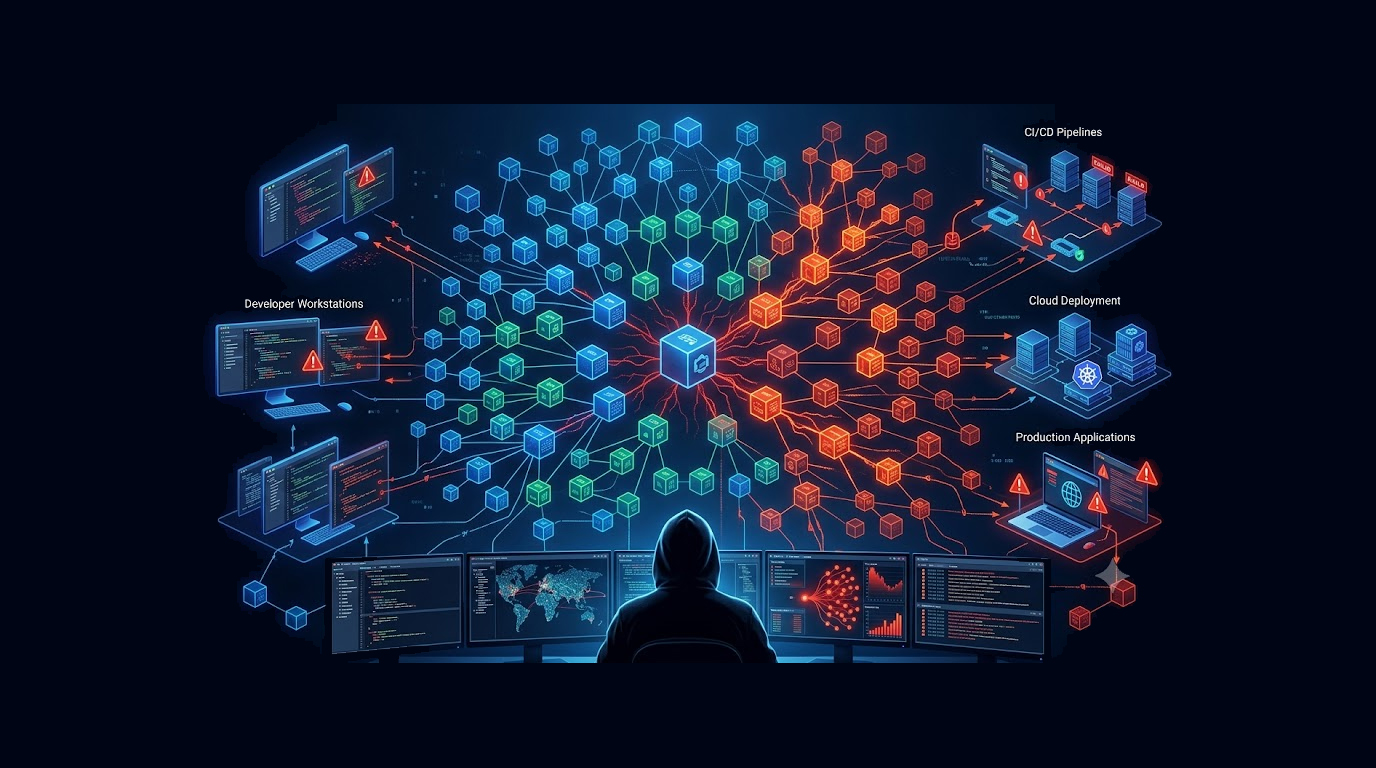
In just 88 minutes, a single npm account published more than 140 malicious versions of packages in the Mastra namespace. Mastra is a popular open-source Ja...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067