Direct vs Indirect Prompt Injection: Real Difference (With Examples)
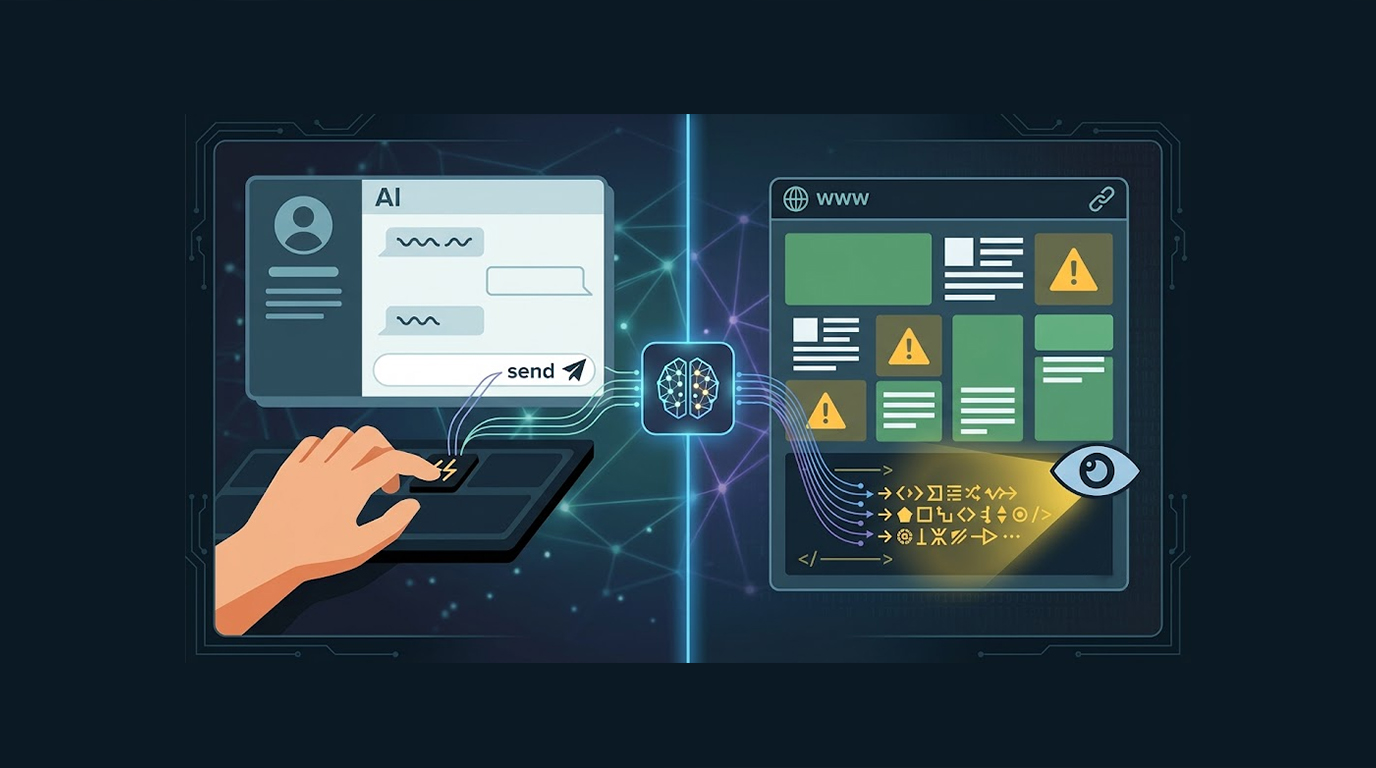
You have probably heard about prompt injection. It is the vulnerability that keeps security teams up at night. It is the number one risk on the OWASP Top 1...
Found 389 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You have probably heard about prompt injection. It is the vulnerability that keeps security teams up at night. It is the number one risk on the OWASP Top 1...
You have 40,000 new vulnerabilities reported in a single year. Your security team can realistically patch maybe 5% of them. The rest will sit there, unpatc...
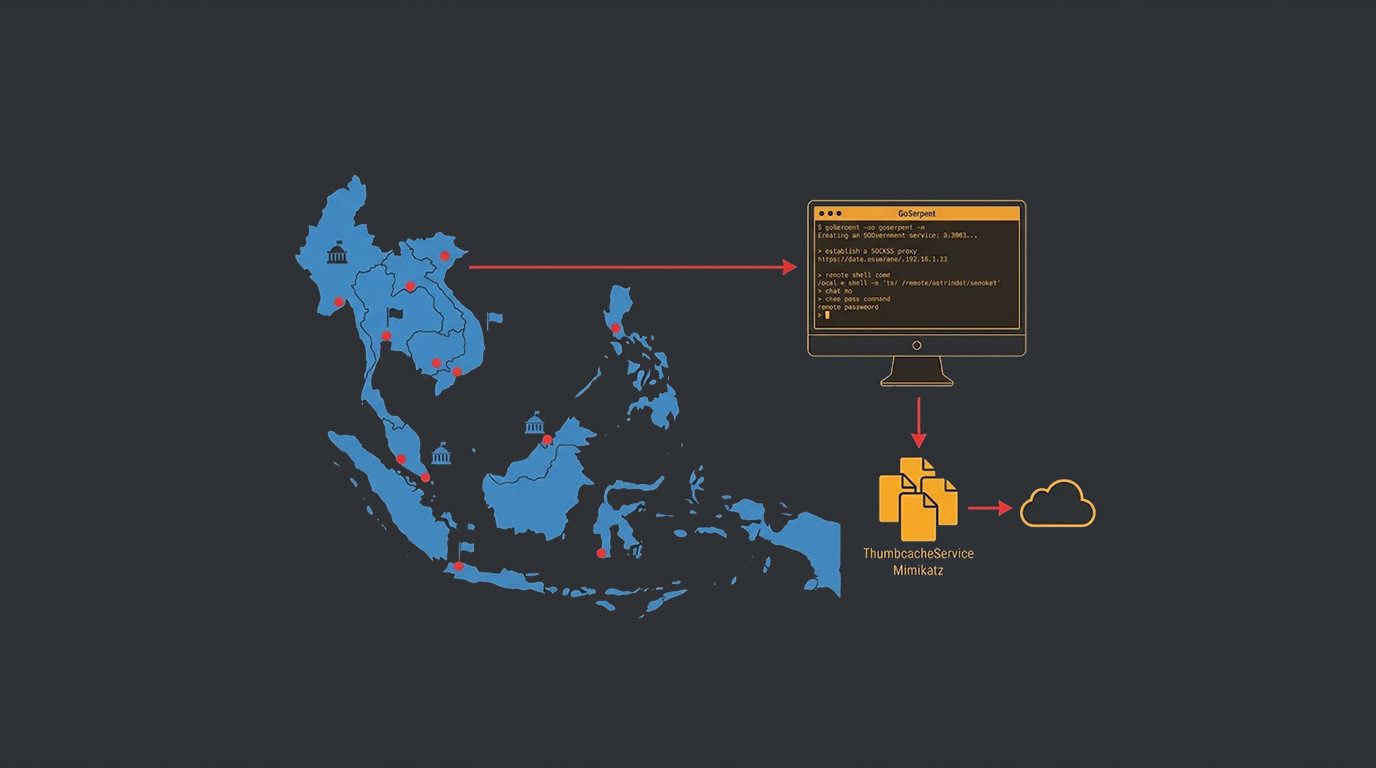
A new malware strain known as GoSerpent has been utilized in cyber attacks against targets from Southeast Asia starting in late 2025. As per Kaspersky, the...
You have done everything right. You patched your systems. You updated your software. You hardened your configurations. You are secure. But what if an atta...
You have a network. You have firewalls, intrusion detection, and endpoint protection. You have done everything right. But the attackers are still probing....
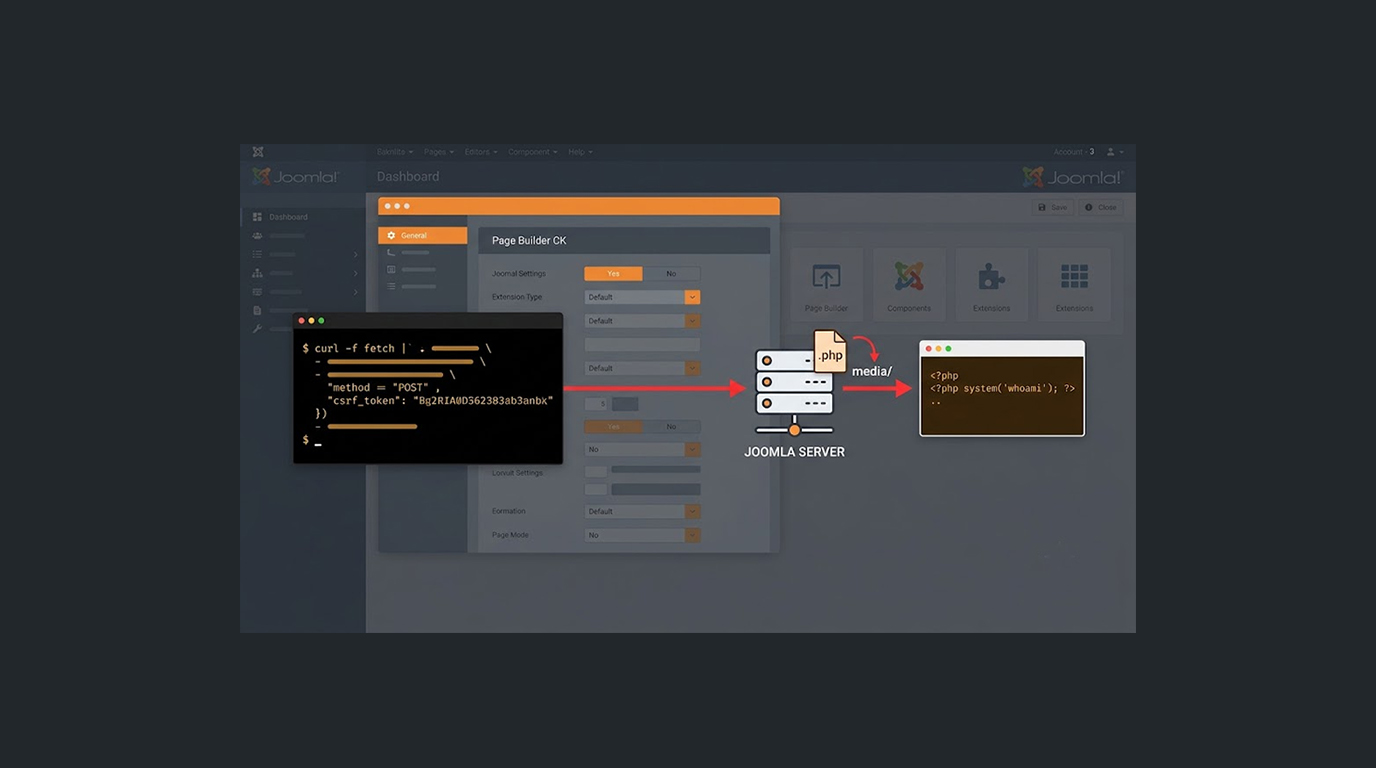
There is a serious vulnerability in Joomla Page Builder CK which enables an attacker without authentication to upload PHP files and run arbitrary code on t...
Bot problem? The malicious bots are scraping your site, stealing your content, and overwhelming your servers. You have tried blocking IP addresses, but the...
You are a security analyst. It is 3 AM. Your SIEM lights up with an alert. A user is downloading large amounts of data from a file server. You investigate....
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067