GitHub Breach Traced to Poisoned Nx Console Extension
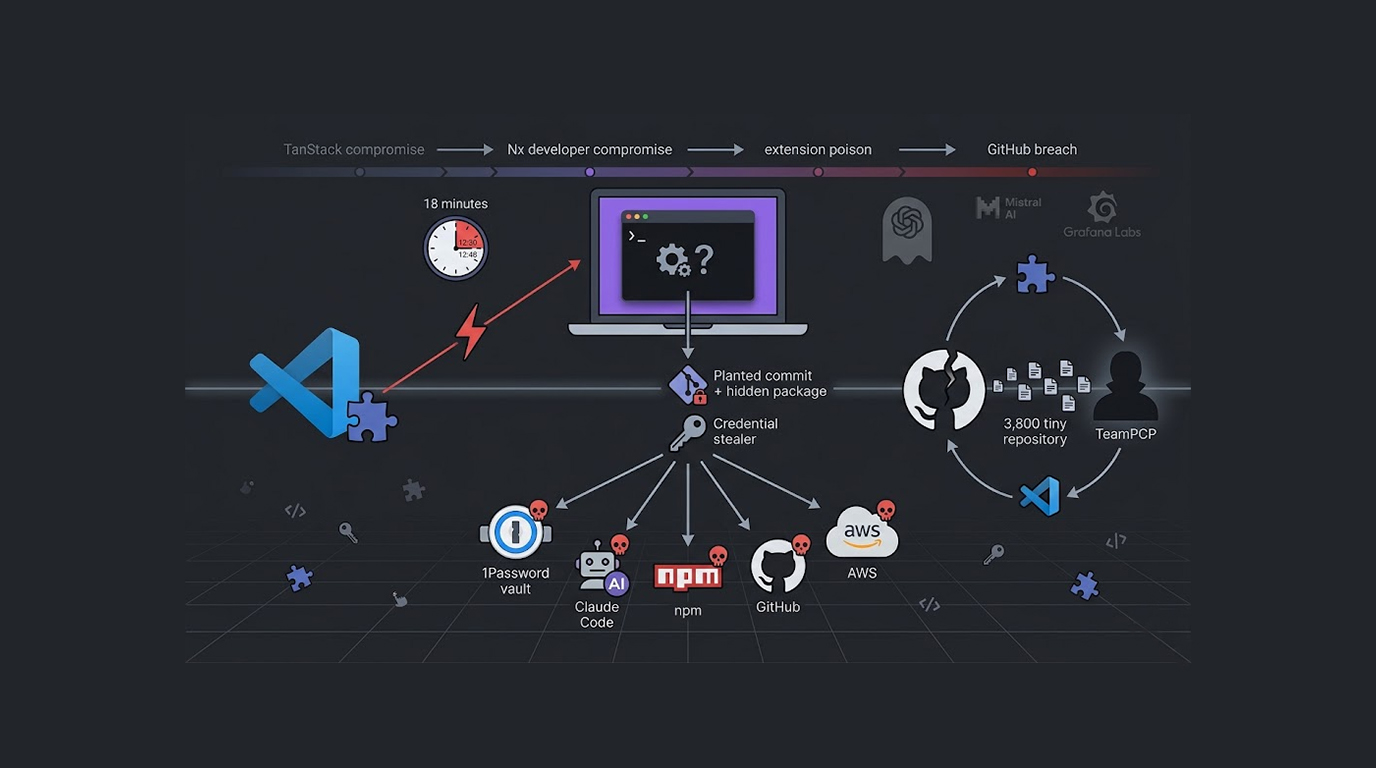
GitHub has officially confirmed that the breach of its internal repositories was the result of a compromised employee device, and the attack vector was a p...
Found 302 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
GitHub has officially confirmed that the breach of its internal repositories was the result of a compromised employee device, and the attack vector was a p...
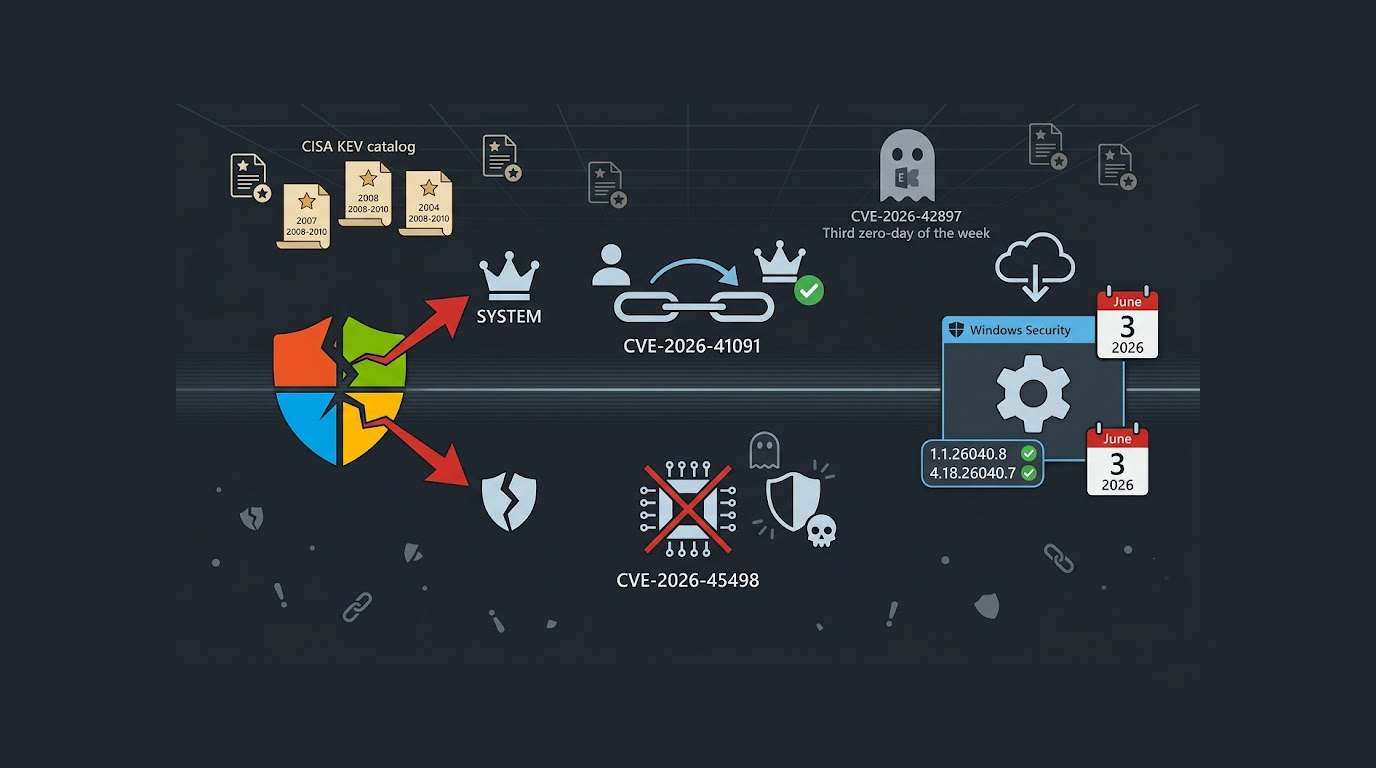
Microsoft has disclosed that two vulnerabilities in Microsoft Defender are under active exploitation, and one of these flaws allows an attacker to gain SYS...
You are sitting in a coffee shop, airport lounge, or shared apartment, and you are connected to the same Wi-Fi as strangers. Someone else on that network...
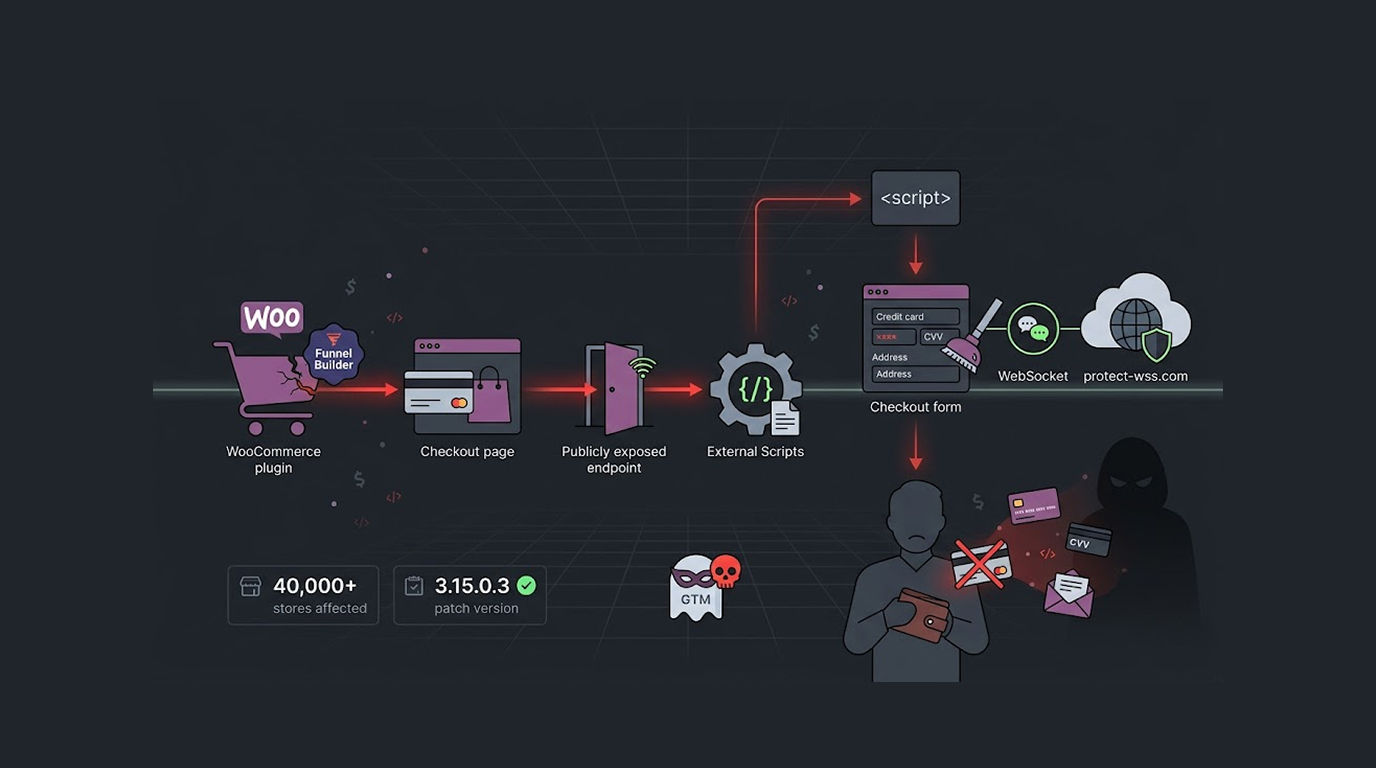
A critical security vulnerability in the Funnel Builder plugin for WordPress is under active exploitation, and attackers are using it to inject malicious J...
Your inbox is overflowing with junk, newsletters you never signed up for, offers you never wanted, scams you never asked for. You see a small link at the...
Your phone rings, you do not recognize the number, you hesitate, but curiosity wins and you answer.Hello, silence, then a click, the line goes dead.You thi...
Your network is set up like this, employees plug into the switch, servers plug into the same switch, everything can talk to everything, it is simple, it is...
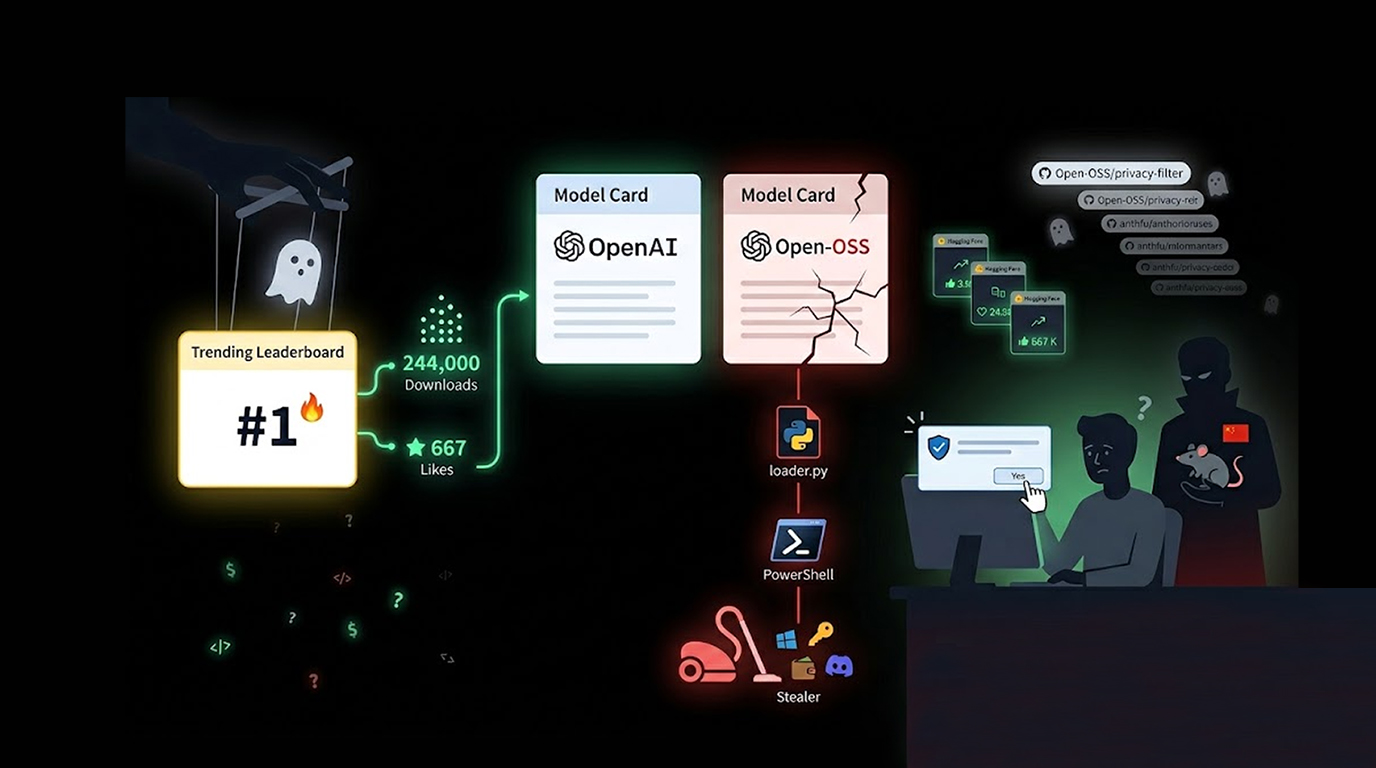
A malicious repository on Hugging Face ranked #1 on the platform by impersonating OpenAI's just-released Privacy Filter model while delivering a Rust-based...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067