RAG Poisoning: AI's Biggest Security Blind Spot
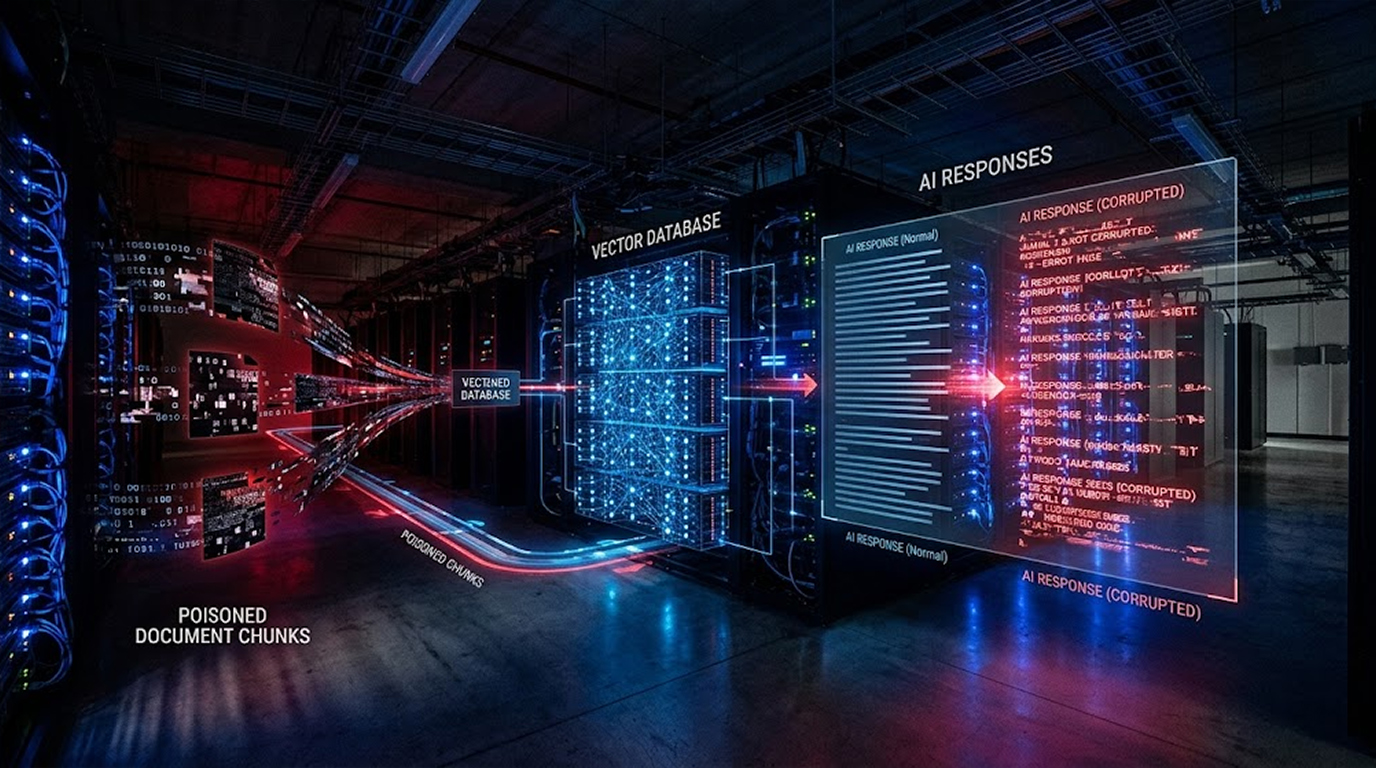
Your AI assistant just told a developer to install a malicious package. It cited a "trusted" internal document as the source. The document looked legitimat...
Found 571 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Your AI assistant just told a developer to install a malicious package. It cited a "trusted" internal document as the source. The document looked legitimat...
There has been an exploitation campaign carried out against a maximum severity vulnerability present in the SAP Commerce Cloud. The attackers have acted pr...
A recently patched security flaw in Apple macOS is now being actively exploited in the wild. Attackers are using it to install cryptocurrency miners on vul...
A previously unseen Android near field communication relay malware family has been discovered in the wild. The malware, dubbed WindRelay, is being deployed...
Threat actors have begun to exploit a newly disclosed Microsoft SharePoint vulnerability. The exploit came after the publication of proof-of-concept code b...
A server-side request forgery vulnerability has been discovered in Apache Gravitino. The flaw affects versions 1.0.0 through 1.2.1 and allows authenticated...
Threat actors have started to target a critical security vulnerability that has been recently patched by Broadcom VMware vCenter. The vulnerability gives a...
A maximum severity level vulnerability was detected in SAP Commerce Cloud, for which patches have been released by SAP. The vulnerability would allow arbit...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067