Cryptojacking Campaign Exploits Docker API for Malicious Swarm Control
Cybersecurity researchers have uncovered a new cryptojacking campaign targeting the Docker Engine API, aiming to enlist compromised instances into a malici...
Found 113 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Cybersecurity researchers have uncovered a new cryptojacking campaign targeting the Docker Engine API, aiming to enlist compromised instances into a malici...
The infamous cryptojacking group TeamTNT has likely resurfaced, launching a new campaign aimed at Virtual Private Server (VPS) infrastructures running the...
Cybersecurity researchers have identified a new malware campaign targeting Linux environments, specifically exploiting Oracle Weblogic servers to conduct i...
The Iraqi government has recently become the target of a highly sophisticated cyberattack campaign orchestrated by the Iranian state-sponsored threat actor...
A Chinese-speaking threat actor, known as Earth Lusca, has been linked to a recent cyber attack involving a new backdoor called KTLVdoor, targeting an unna...
Threat actors are actively exploiting a critical security vulnerability in Atlassian Confluence Data Center and Confluence Server to conduct unauthorized c...
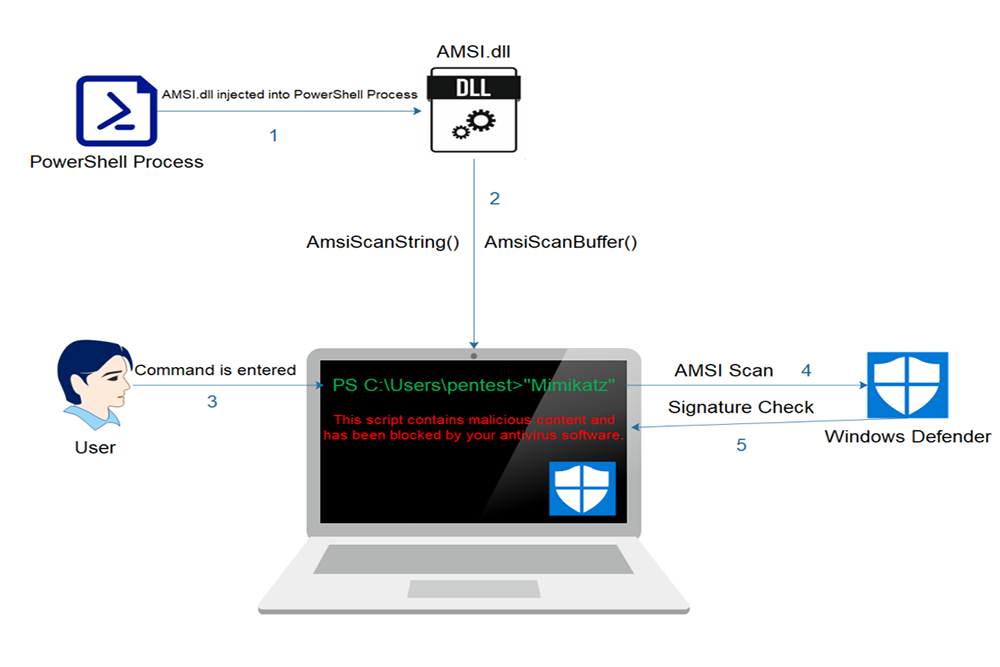
Introduction Windows developed the Antimalware Scan Interface (AMSI) standard that allows a developer to integrate malware defense in his application. AMS...
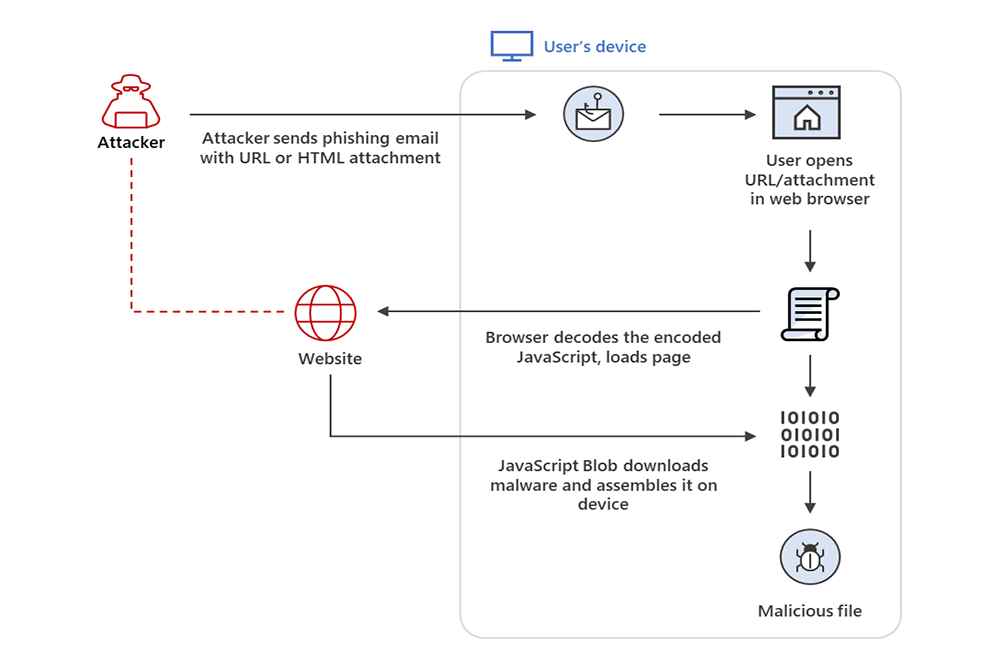
Introduction HTML Smuggling is an evasive payload delivery method that helps an attacker smuggle payload past content filters and firewalls by hiding mali...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067