PamDOORa SSH Backdoor: The 'Magic Password' Attack Explained
You type your SSH password, you press enter, you are logged in, everything seems normal, but someone else just logged in without any password at all, they...
Found 200 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You type your SSH password, you press enter, you are logged in, everything seems normal, but someone else just logged in without any password at all, they...
cPanel has issued security patch for three vulnerabilities within its cPanel/WHM software that may allow attackers to read arbitrary files, execute Perl sc...
A developer sits down at their Linux workstation, pushes code, publishes packages, and manages cloud infrastructure, but they have no idea that every keyst...
You have run Cobalt Strike for years, it works, but it is also the most signatured tool on the market, every defender knows how to spot it Havoc is differ...
A kernel bug that has lurked in Linux for over a decade can turn any local user into root. The flaw sits in how the proc filesystem handles directory entri...
You built a Docker image, it runs perfectly, no errors, no warnings, you push it to your registryBut inside that image, there are vulnerabilities, old vers...
60 seconds to summarize for you about DIRTPIPE (Dirty Pipe) security vulnerability. The TL;DR (10 Seconds) Question Answer What...
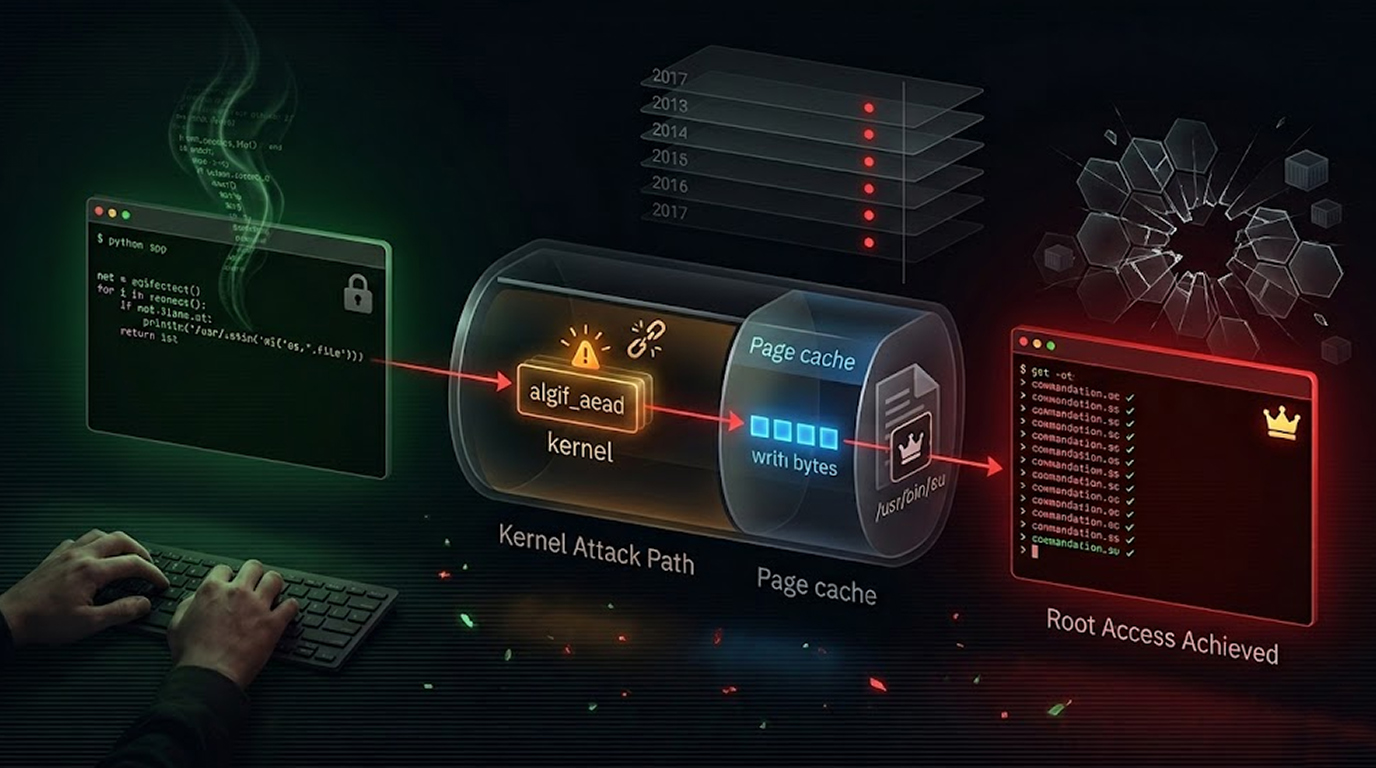
A single 732-byte Python script. Four controlled bytes. And root access on virtually every Linux machine shipped since 2017. That is the reality of Copy F...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067