Comment Box to Remote Code Execution (RCE)
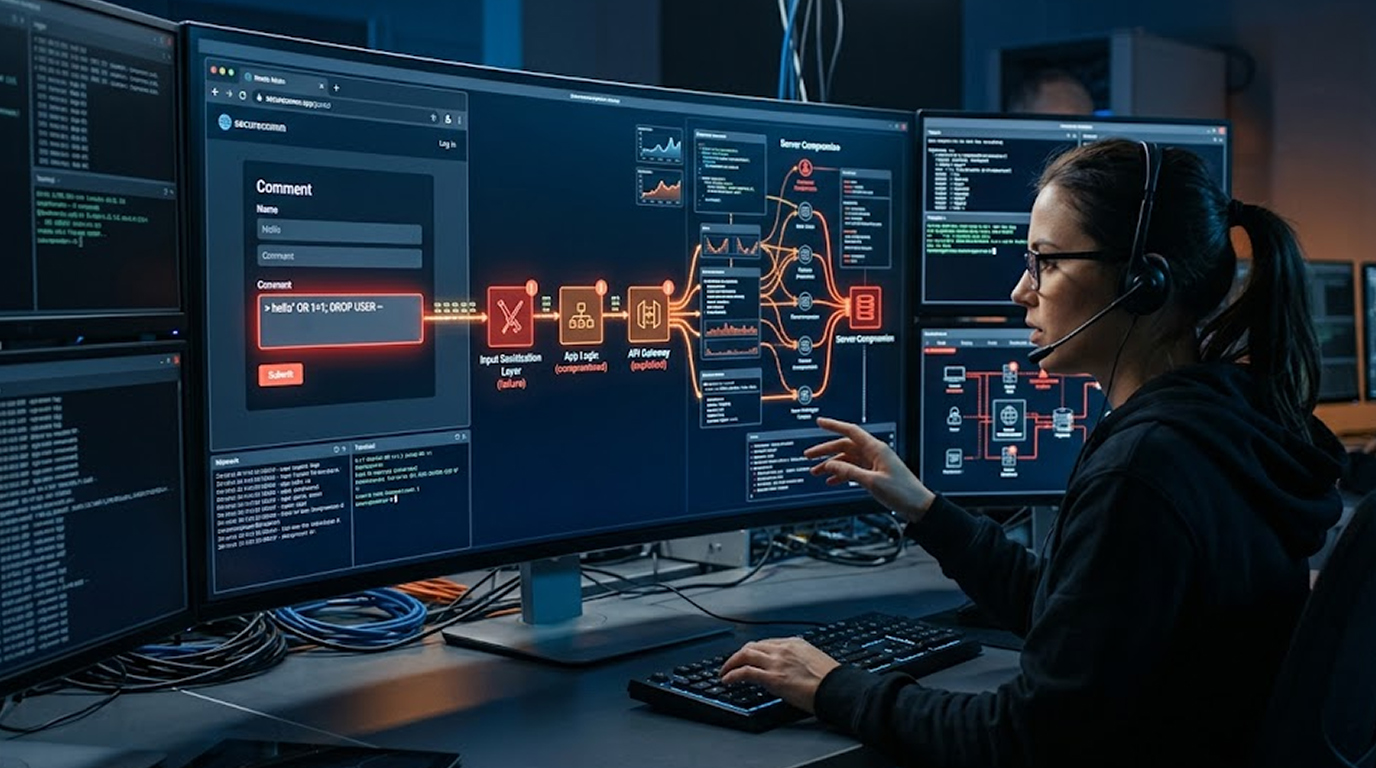
While the comment box may appear to be a benign feature of a website (i.e., a place for users to submit their feedback), at its core, it can become an entr...
Found 183 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
While the comment box may appear to be a benign feature of a website (i.e., a place for users to submit their feedback), at its core, it can become an entr...
SSTI (Server Side Template Injection) is an incredibly hazardous as well as often overlooked method of code injection that has been used against modern web...
Cybersecurity researchers have warned that cybercriminals are currently leveraging a serious remote code execution vulnerability in Flowise – a widel...
Researchers in cybersecurity have discovered 36 malicious npm packages attempting to masquerade as plugins for the widely used open source Content Manageme...
CPA (Cost Per Action) fraud keeps evolving fast in 2026. Currently, fraudsters are using bot farms and actual device farms (that can imitate humans very we...
Most organizations have a WAF and firewall, but a surprising amount of malicious traffic still slips through because the rules are either too generic or fo...
Nothing kills an online store faster than hidden redirects and pharma spam. One day your customers are happily browsing, the next they’re being redir...
The postinstall script is one of the most abused features in the npm ecosystem right now (2025–2026). When you run npm install, anything listed in th...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067