SolarEdge CSRF OOB Injection Compromises Monitoring
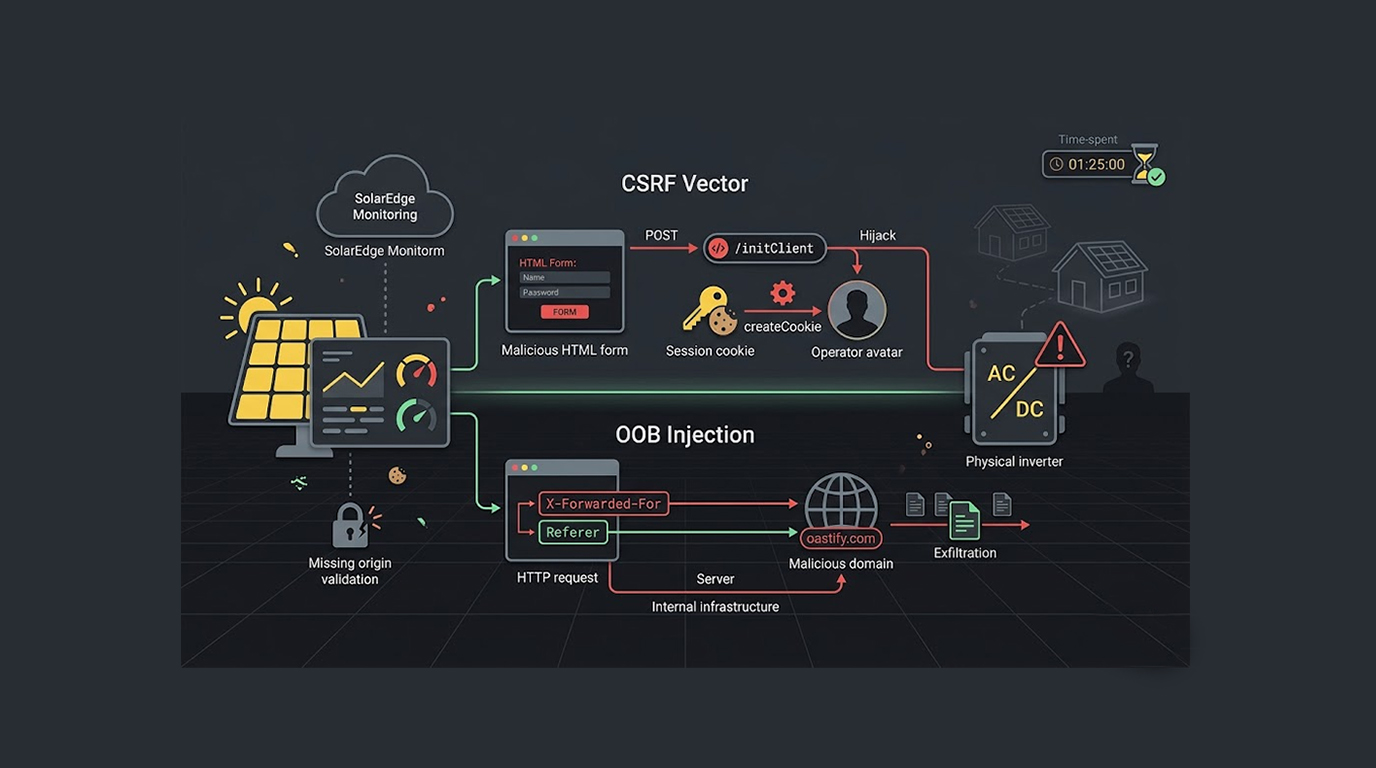
An essential flaw within the SolarEdge monitoring platform's business logic permits the takeover of an operator's session by an attacker, which will allow...
Found 148 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
An essential flaw within the SolarEdge monitoring platform's business logic permits the takeover of an operator's session by an attacker, which will allow...
An active exploitation of an extremely severe vulnerability was found on the LiteSpeed cPanel Plugin for User-End usage. This vulnerability allows attacker...
Chinese-linked threat actors carried out a lengthy operation from December 2025 to February 2026, using a compromised Microsoft Exchange server to establis...
You finally did the right thing, you hired a penetration testing firm to find security holes before the criminals do.You expected a few minor issues, maybe...
cPanel has issued security patch for three vulnerabilities within its cPanel/WHM software that may allow attackers to read arbitrary files, execute Perl sc...
A popular blogging platform has a serious problem, attackers can steal admin passwords and API keys without ever logging in, and the vulnerability has exis...
You have run Cobalt Strike for years, it works, but it is also the most signatured tool on the market, every defender knows how to spot it Havoc is differ...
A critical vulnerability in a popular enterprise office automation platform is being actively exploited. Attackers need no password. No username. No specia...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067