FatFs File System Flaws Expose Embedded Devices
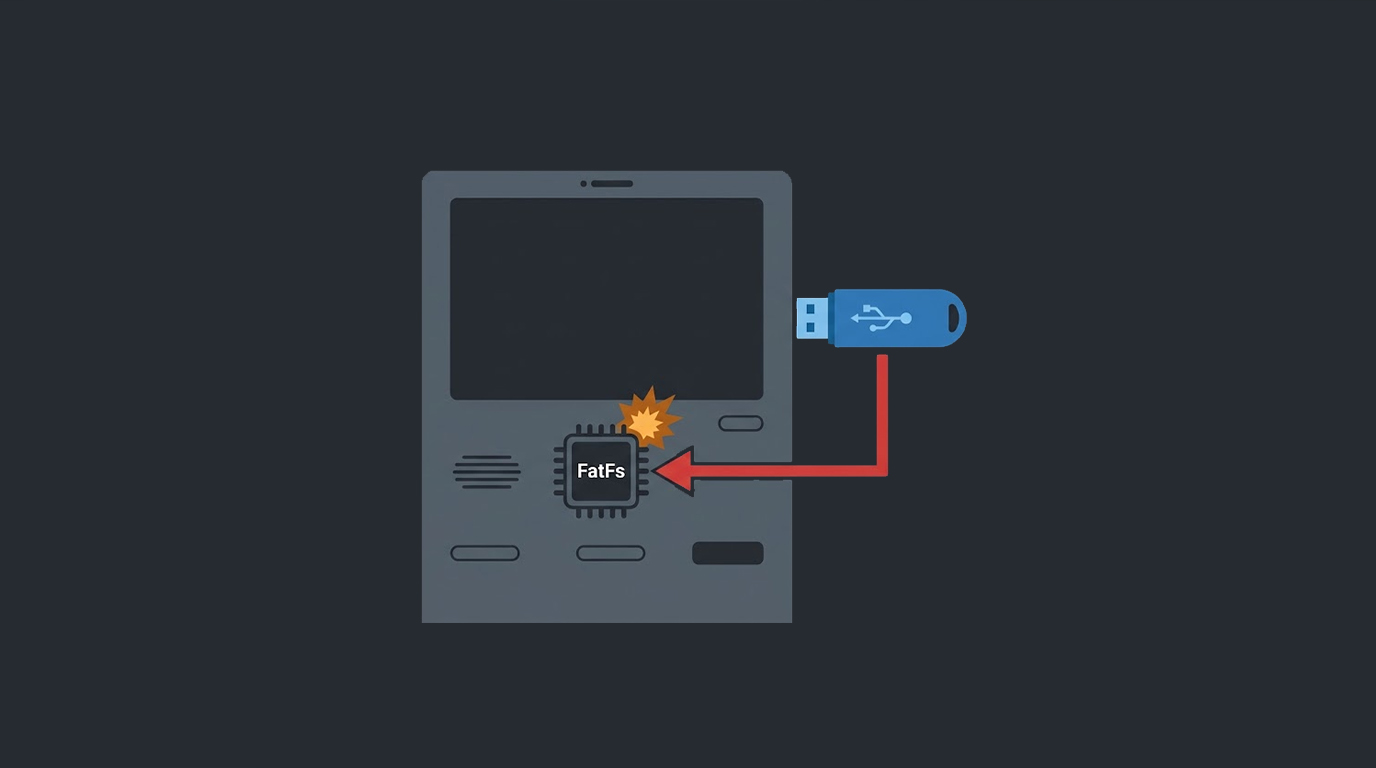
Security firm runZero has uncovered seven vulnerabilities in FatFs, a lightweight filesystem library that handles FAT and exFAT formats for USB drives and...
Found 234 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Security firm runZero has uncovered seven vulnerabilities in FatFs, a lightweight filesystem library that handles FAT and exFAT formats for USB drives and...
A newly discovered vulnerability in the Linux kernel allows any unprivileged user to obtain full root access. The flaw, known as Bad Epoll and tracked as C...
You are the CISO of a major utility company. It is 2 AM. Your phone rings. The operator on the other end tells you that the power grid is offline. Three ci...
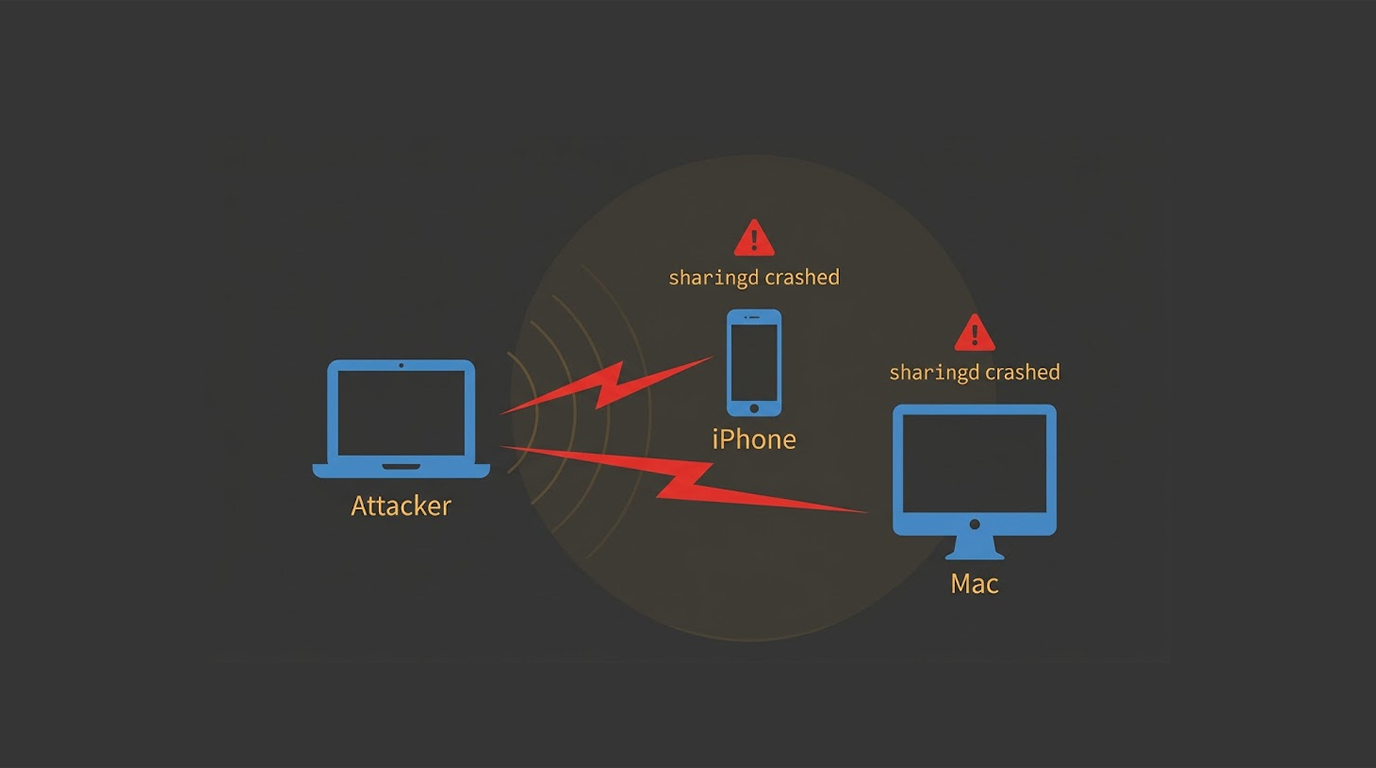
An attacker within wireless range, with just a laptop and no prior connection, can crash the sharing service on a Mac or iPhone set to receive from anyone....
You receive an email. It looks normal. Your AI assistant scans it, summarizes it, and files it away. You never even open it. But something just happened....
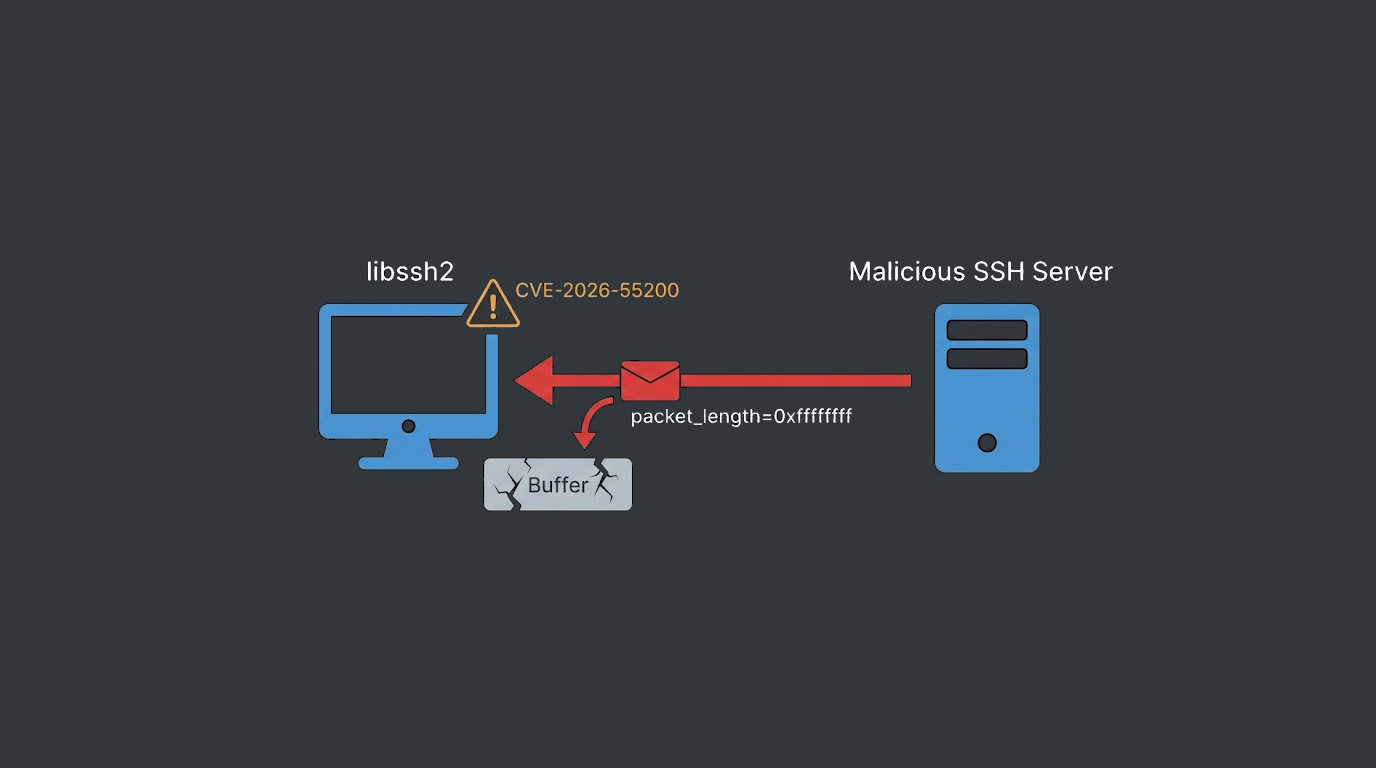
Proof of concept released to the public for CVE-2026-55200 – an extremely critical vulnerability in libssh2 where a malicious SSH server can cause me...
You have heard the terms. Red team attacks. Blue team defends. But when you look at the actual commands, what is the difference? The answer is not the too...
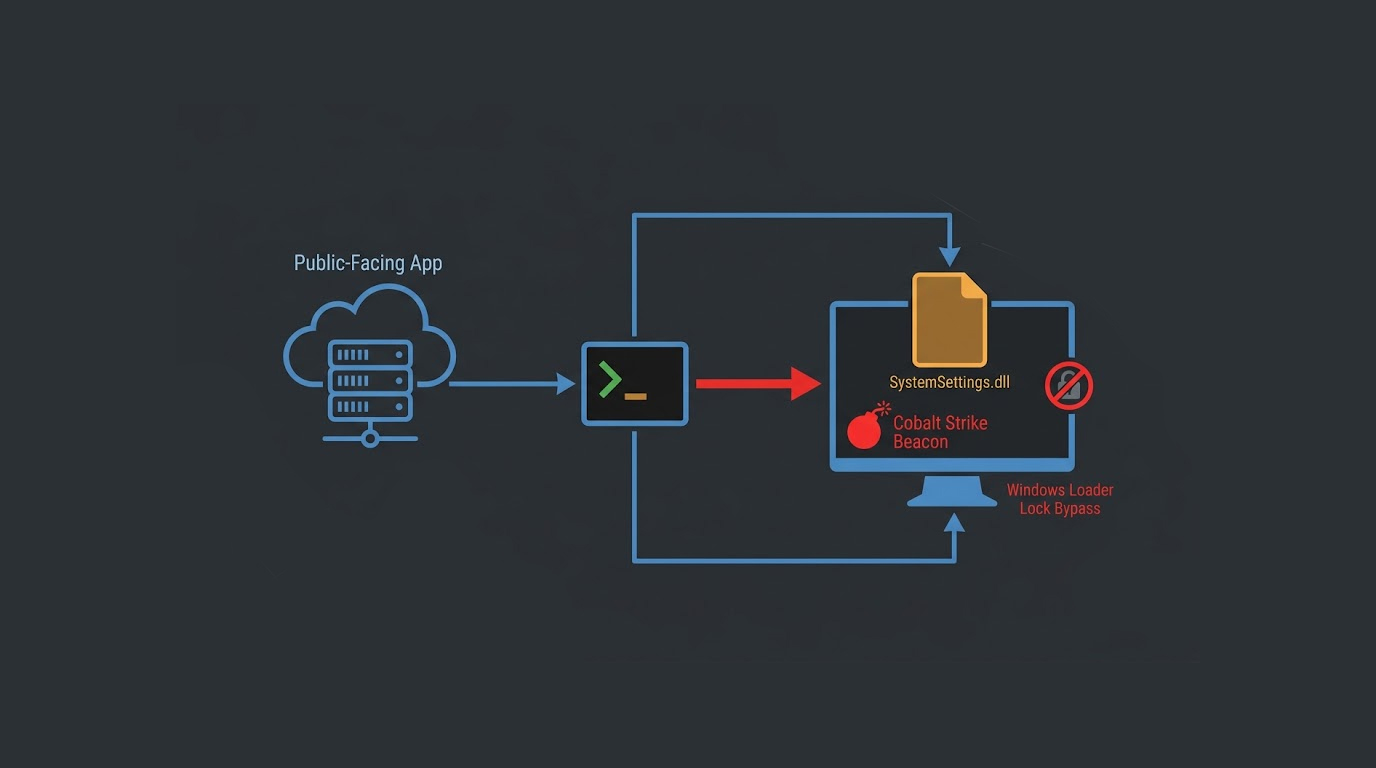
This new wave of attacks includes an unknown variant of malware known as SharkLoader. SharkLoader functions as a loader for distributing Cobalt Strike Beac...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067