Malicious Overlays in Banking Apps
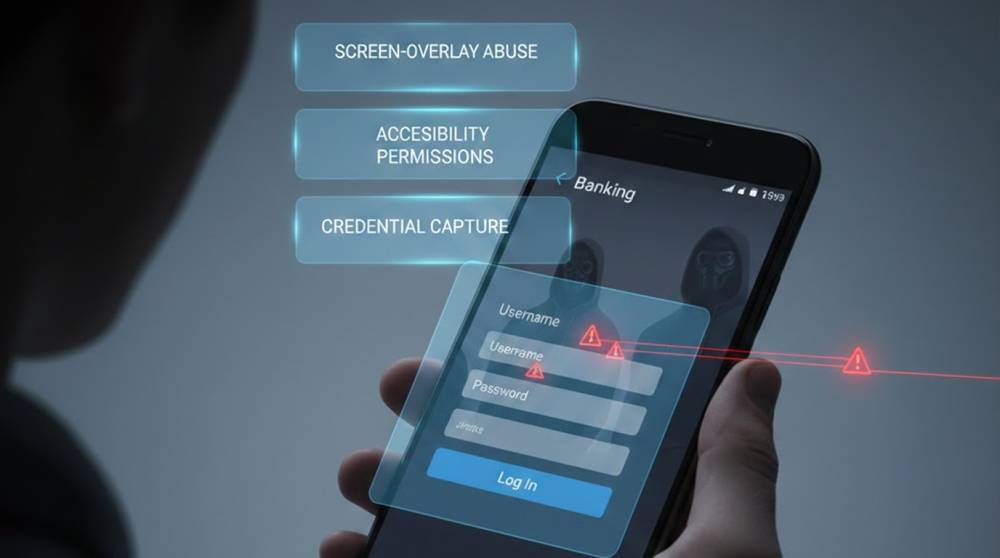
A malicious overlay can be described as a secondary interface used to simulate legitimate online banking applications. From a User's Perspective:1. The ov...
Found 173 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A malicious overlay can be described as a secondary interface used to simulate legitimate online banking applications. From a User's Perspective:1. The ov...
Attackers are no longer trying to break systems first.They are trying to become users.Once identity is compromised, most defenses step aside.No exploit cha...
The Federal Bureau of Investigation (FBI) has published a notice that warns about potential attacks using malicious QR codes targeting think tanks and high...
Why BGP Is an Attractive TargetBorder Gateway Protocol decides how traffic moves across the internet.It was designed for cooperation, not hostility.BGP ass...
What “Malware Free” Actually MeansNot all compromises involve payloads, binaries, or dropped files.Some of the most persistent incidents never...
Automation has quietly changed the balanceCyber-attacks are no longer driven only by people sitting behind screens.Much of the activity now comes from syst...
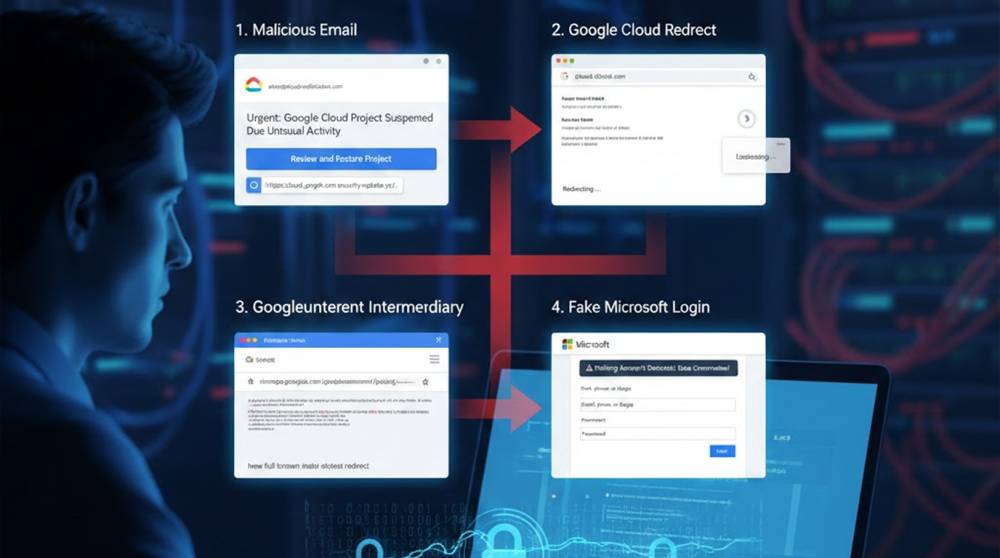
Cybersecurity experts discovered a new type of phishing attack using the Google Cloud's Application Integration service to send email from a legitimate-loo...
When an online account stops being yoursA social media takeover is usually noticed through small signs.An unfamiliar post. Messages you did not send. A sud...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067