TeamPCP Supply Chain Worm Hits npm PyPI
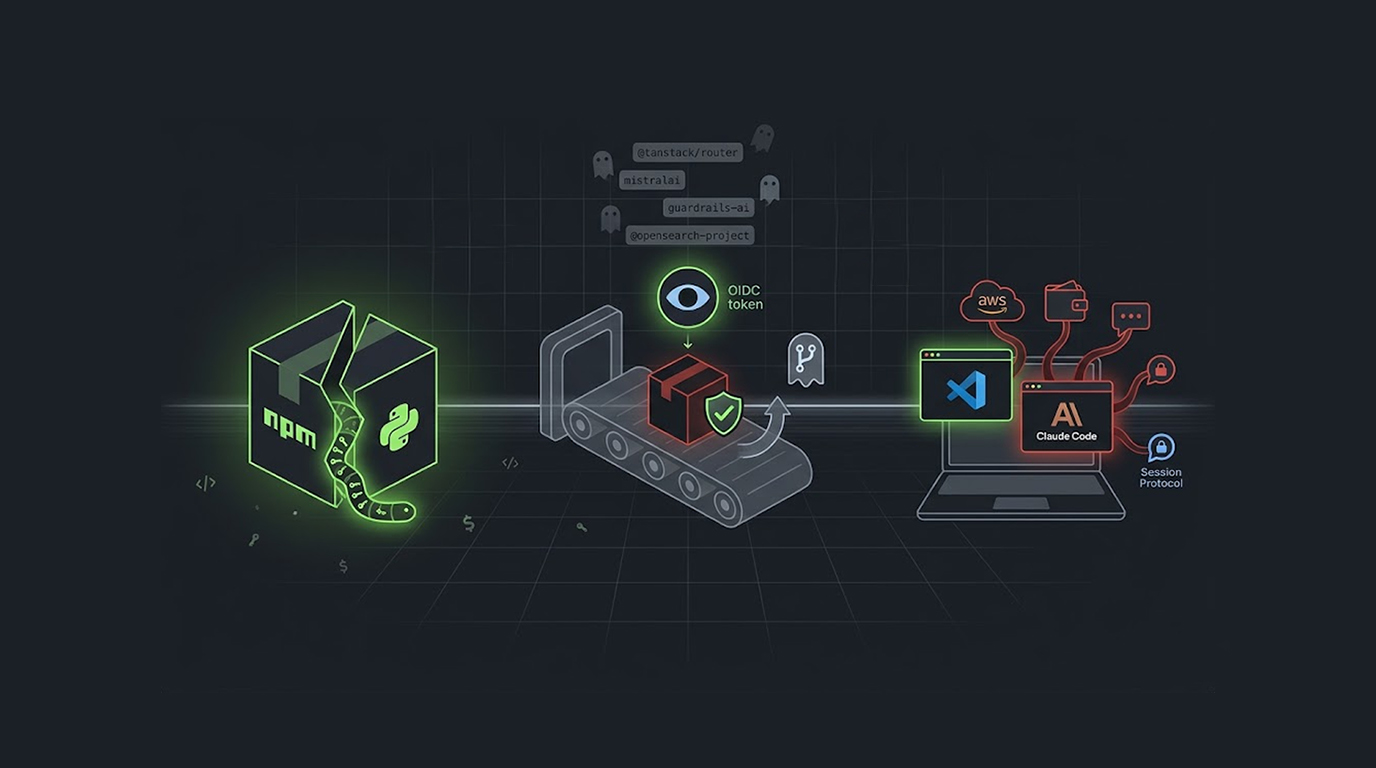
A single worm has spread across both npm and PyPI, it compromised packages from major companies like TanStack, UiPath, Mistral AI, and OpenSearch, and it u...
Found 174 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A single worm has spread across both npm and PyPI, it compromised packages from major companies like TanStack, UiPath, Mistral AI, and OpenSearch, and it u...
You spend thousands on marketing, you optimize your product pages, you run Facebook ads, you finally see sales rolling in.Then one morning you wake up to a...
cPanel has issued security patch for three vulnerabilities within its cPanel/WHM software that may allow attackers to read arbitrary files, execute Perl sc...
A kernel bug that has lurked in Linux for over a decade can turn any local user into root. The flaw sits in how the proc filesystem handles directory entri...
You built a Docker image, it runs perfectly, no errors, no warnings, you push it to your registryBut inside that image, there are vulnerabilities, old vers...
A critical vulnerability in a popular enterprise office automation platform is being actively exploited. Attackers need no password. No username. No specia...
Imagine waking up to find your email server locked. Your admin password does not work. Your users cannot send or receive messages.You did not click a phish...
60 seconds to summarize for you about DIRTPIPE (Dirty Pipe) security vulnerability. The TL;DR (10 Seconds) Question Answer What...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067