OSGeo GeoServer Exploit Targets Global Organizations with Botnets and Backdoors
A critical remote code execution flaw in OSGeo GeoServer GeoTools (CVE-2024-36401, CVSS score: 9.8) is being exploited in multiple malware campaigns. Threa...
Found 953 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A critical remote code execution flaw in OSGeo GeoServer GeoTools (CVE-2024-36401, CVSS score: 9.8) is being exploited in multiple malware campaigns. Threa...
Google has rolled out its monthly security updates for the Android operating system, addressing a high-severity flaw that is being actively exploited in th...
A newly discovered security flaw in the Apache OFBiz open-source enterprise resource planning (ERP) system has been patched, preventing the risk of unauthe...
Veeam has rolled out a set of critical security updates aimed at addressing 18 vulnerabilities across its software products. Among these, five are categori...
In today's digital age, cybersecurity has become a critical concern as organizations face increasing cyber threats. As traditional security measures strugg...
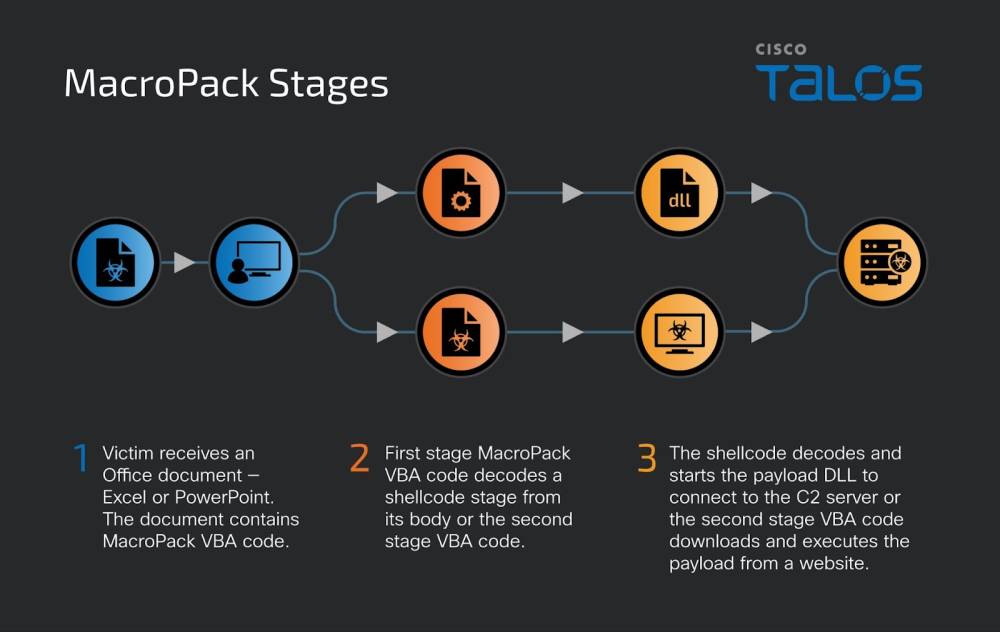
Threat actors are utilizing a red-teaming tool called MacroPack to serve malware payloads, according to recent findings from Cisco Talos. Originally design...
A new malware campaign has been detected that targets users searching for Palo Alto Networks' GlobalProtect VPN software. The campaign, active since June 2...
A hacktivist group known as Head Mare has been linked to a series of cyber attacks that exclusively target organizations in Russia and Belarus. In a recen...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067