Insecure Tool Calling Risks in Autonomous AI Agents
Tool calling (also known as function calling or tool use) is one of the most powerful features of modern large language models. It allows autonomous AI age...
Found 152 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Tool calling (also known as function calling or tool use) is one of the most powerful features of modern large language models. It allows autonomous AI age...
Researchers in cybersecurity have discovered 36 malicious npm packages attempting to masquerade as plugins for the widely used open source Content Manageme...
Hacked websites are a nightmare for anyone who owns one. You have to deal with the downtime of your site, a possible loss of data, and a lot of very upset...
The postinstall script is one of the most abused features in the npm ecosystem right now (2025–2026). When you run npm install, anything listed in th...
Cybersecurity researchers have spotted yet another clever attempt to slip malicious code into developers' toolkits, this time by impersonating one of the m...
In the first half of 2026 a new class of malware started appearing in underground forums and private Telegram channels under names like “PromptReaper”, “LL...
Google Play Protect is Android's built-in malware scanner, it runs in the background, checks apps during install and periodically after, and can block or w...
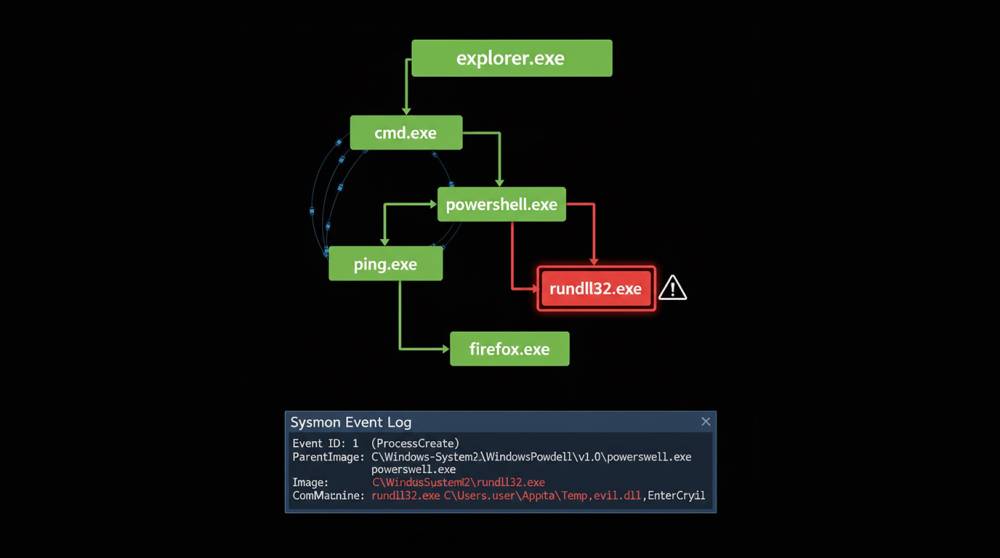
Process ancestry monitoring tracks the parent-child relationships between processes (who spawned what). This is one of the most reliable ways to detect liv...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067