Poisoning Public Repos with Fake Credentials
Poisoning public repositories with fake (but very attractive-looking) credentials is one of the fastest-growing reconnaissance and initial-access technique...
Found 185 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Poisoning public repositories with fake (but very attractive-looking) credentials is one of the fastest-growing reconnaissance and initial-access technique...
All three techniques are still responsible for a huge portion of account takeovers in 2026, but the balance has shifted noticeably over the last two years....
Google Play Protect is Android's built-in malware scanner, it runs in the background, checks apps during install and periodically after, and can block or w...
The SMB (Server Message Block) is a popular protocol used by ransomware gangs to move between computers in networked environments like Windows. Port 445 is...
The open-source webcam security software, MotionEye, is vulnerable to remote code execution, identified as CVE-2025-60787 (motionEye <= 0.43.1b4). Authe...
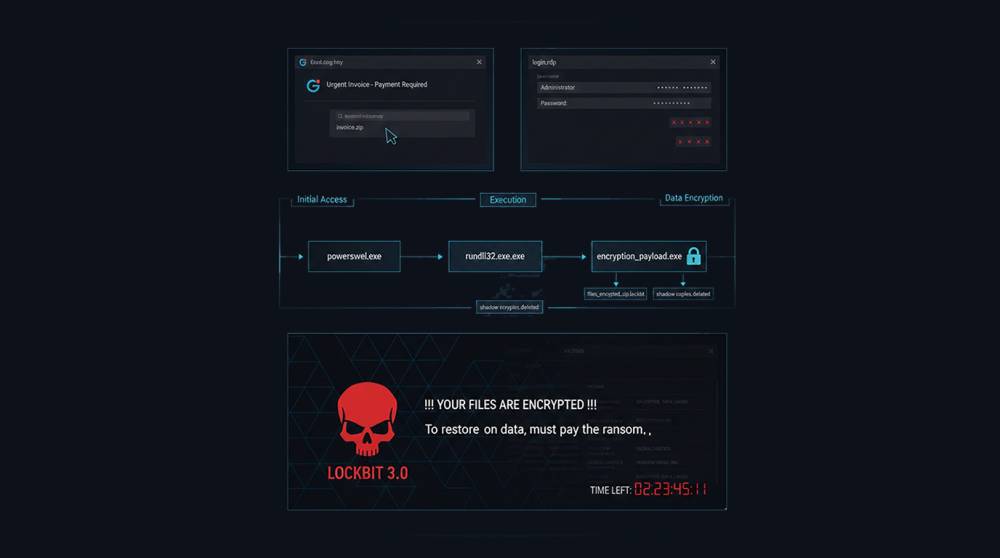
LockBit is (or was) the most active and profitable ransomware-as-a-service (RaaS) operation in recent years. The group provides the LockBit ransomware buil...
CVE-2025-58180 is a critical remote code execution vulnerability (CVSS 7.5) in OctoPrint versions ≤ 1.11.2 (patched in 1.11.3, released September 2025)....
Ivanti disclosed and patched two high-severity (CVSS 9.8) code injection vulnerabilities (CVE-2026-1281 and CVE-2026-1340) affecting Ivanti Endpoint Manage...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067