GitHub Breach Traced to Poisoned Nx Console Extension
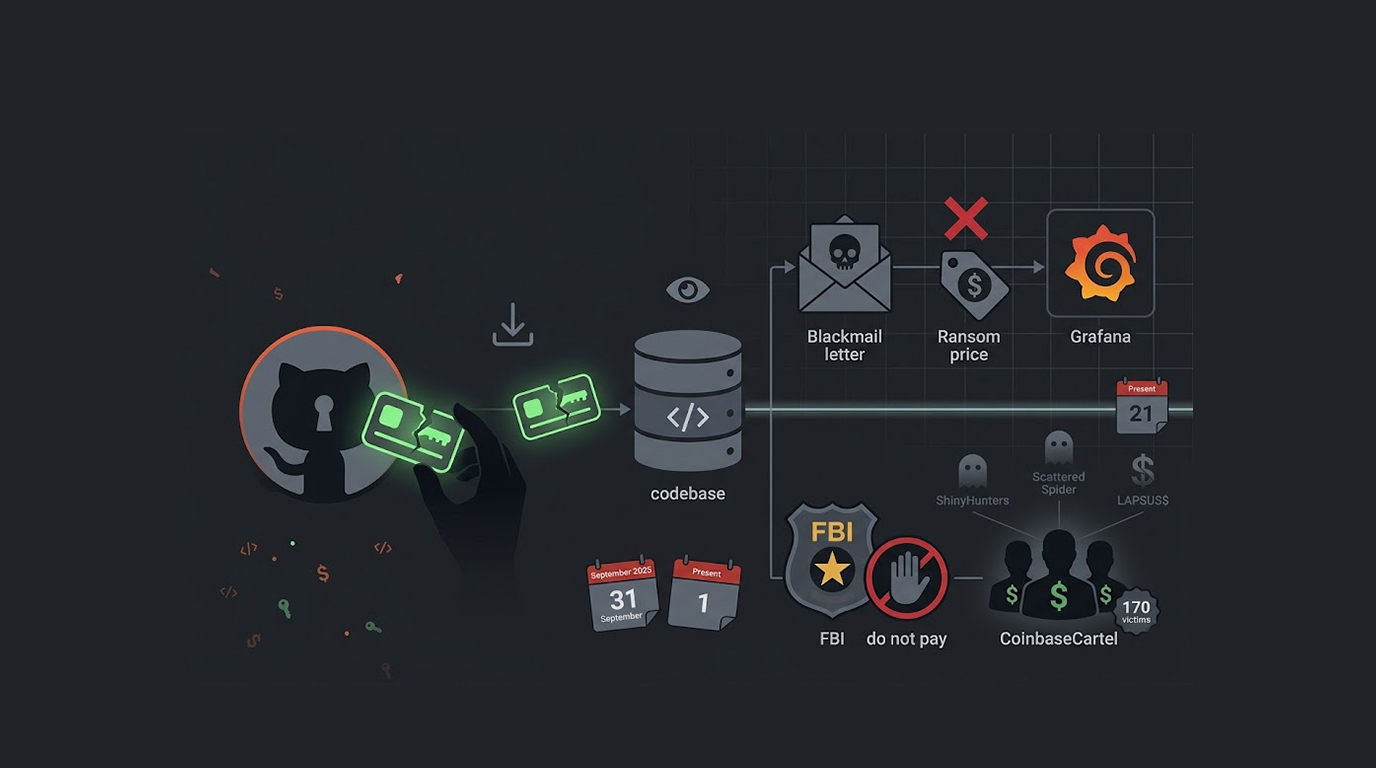
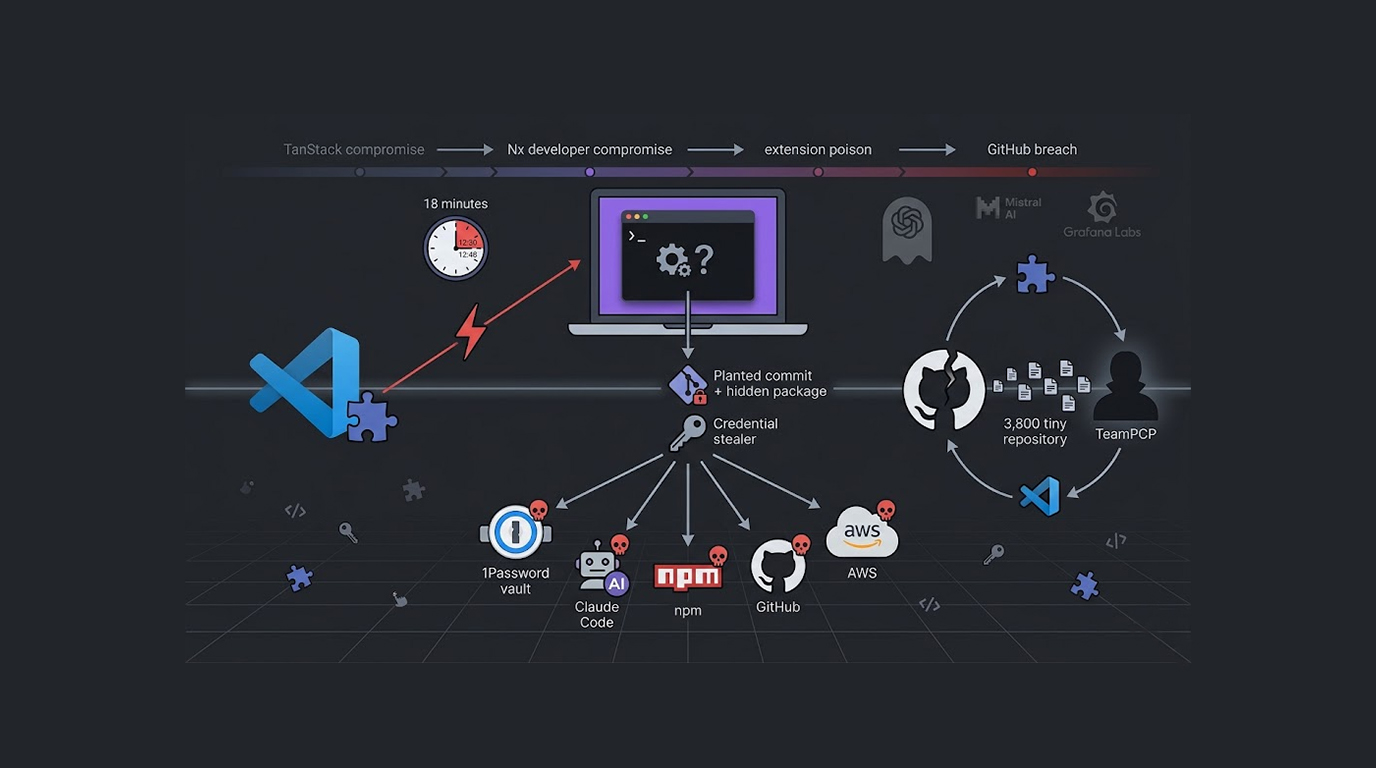
GitHub has officially confirmed that the breach of its internal repositories was the result of a compromised employee device, and the attack vector was a p...
Found 200 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
GitHub has officially confirmed that the breach of its internal repositories was the result of a compromised employee device, and the attack vector was a p...
Grafana has disclosed that an unauthorized party obtained a token granting access to the company's GitHub environment, and the attacker used this access to...
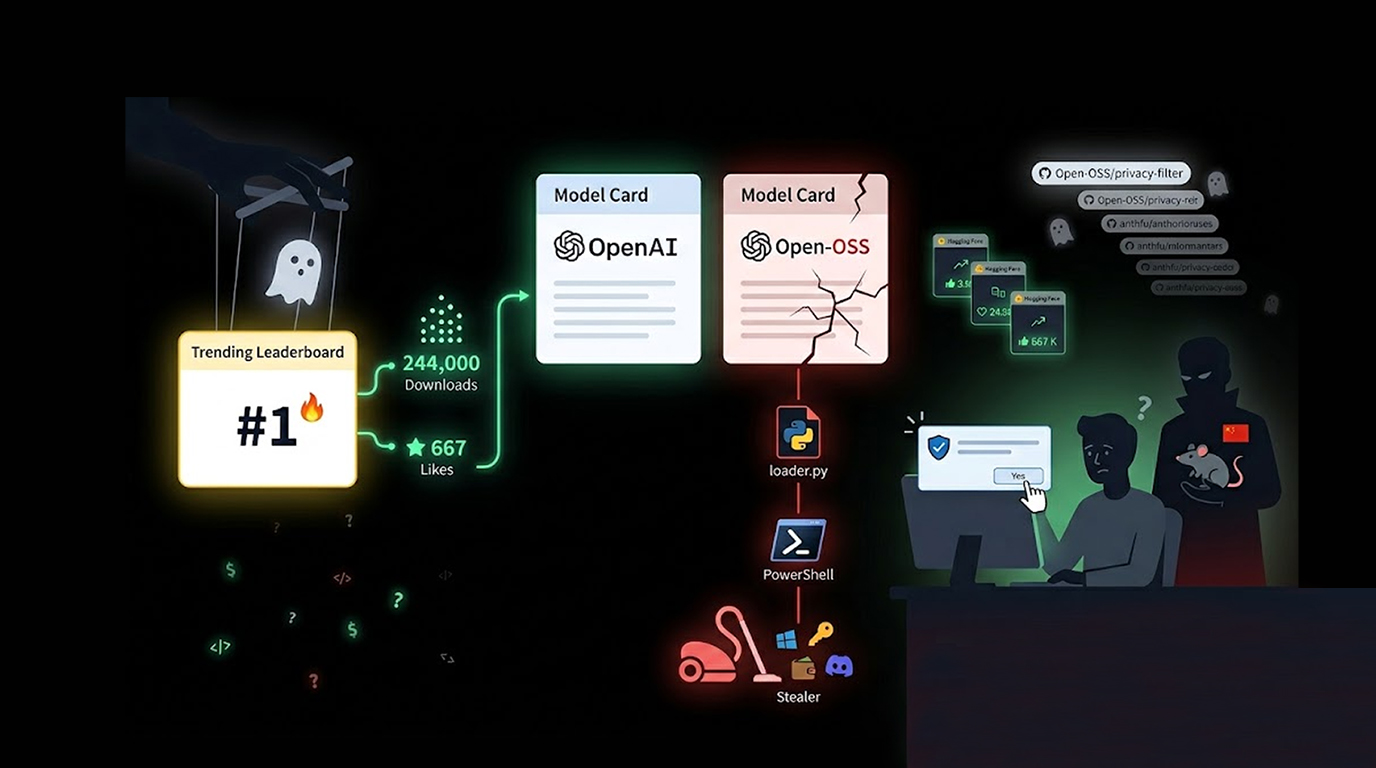
A malicious repository on Hugging Face ranked #1 on the platform by impersonating OpenAI's just-released Privacy Filter model while delivering a Rust-based...
A popular blogging platform has a serious problem, attackers can steal admin passwords and API keys without ever logging in, and the vulnerability has exis...
You have run Cobalt Strike for years, it works, but it is also the most signatured tool on the market, every defender knows how to spot it Havoc is differ...
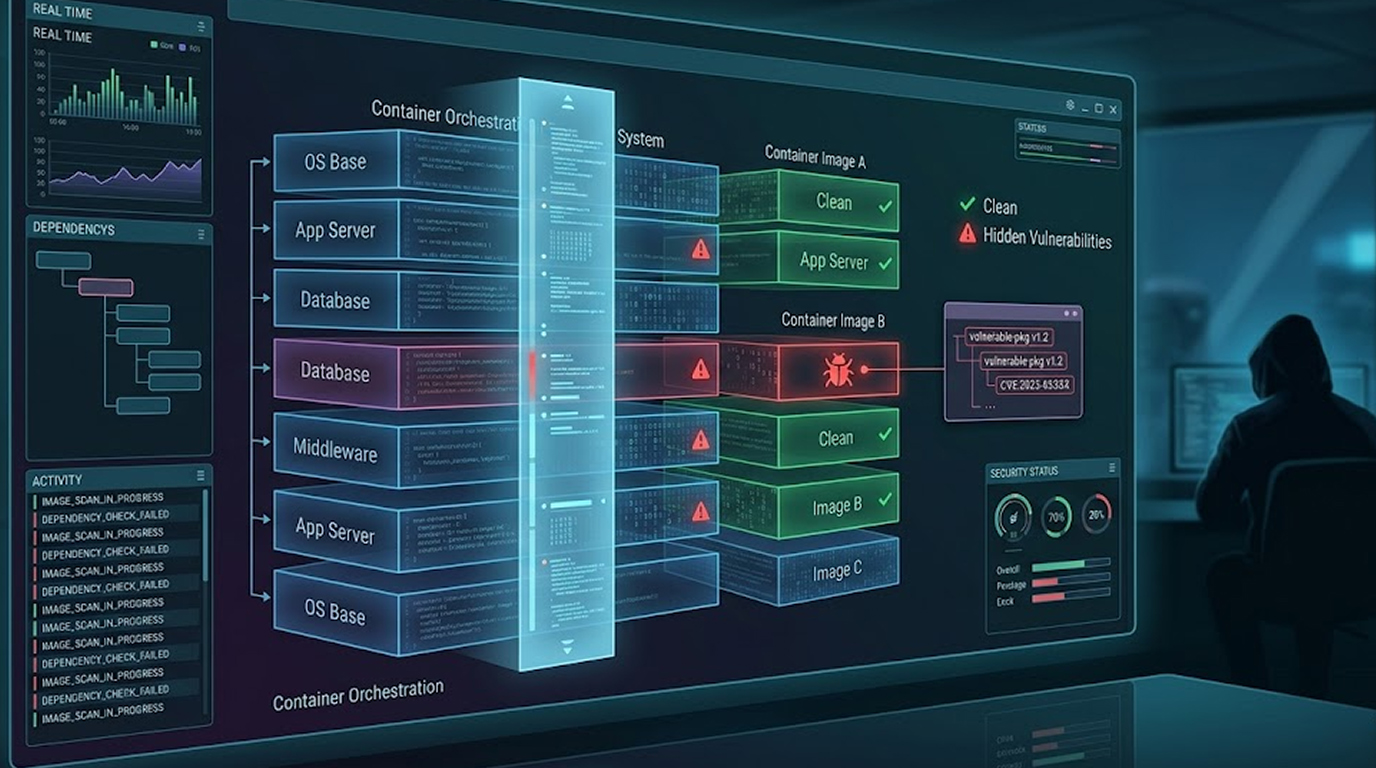
You built a Docker image, it runs perfectly, no errors, no warnings, you push it to your registryBut inside that image, there are vulnerabilities, old vers...
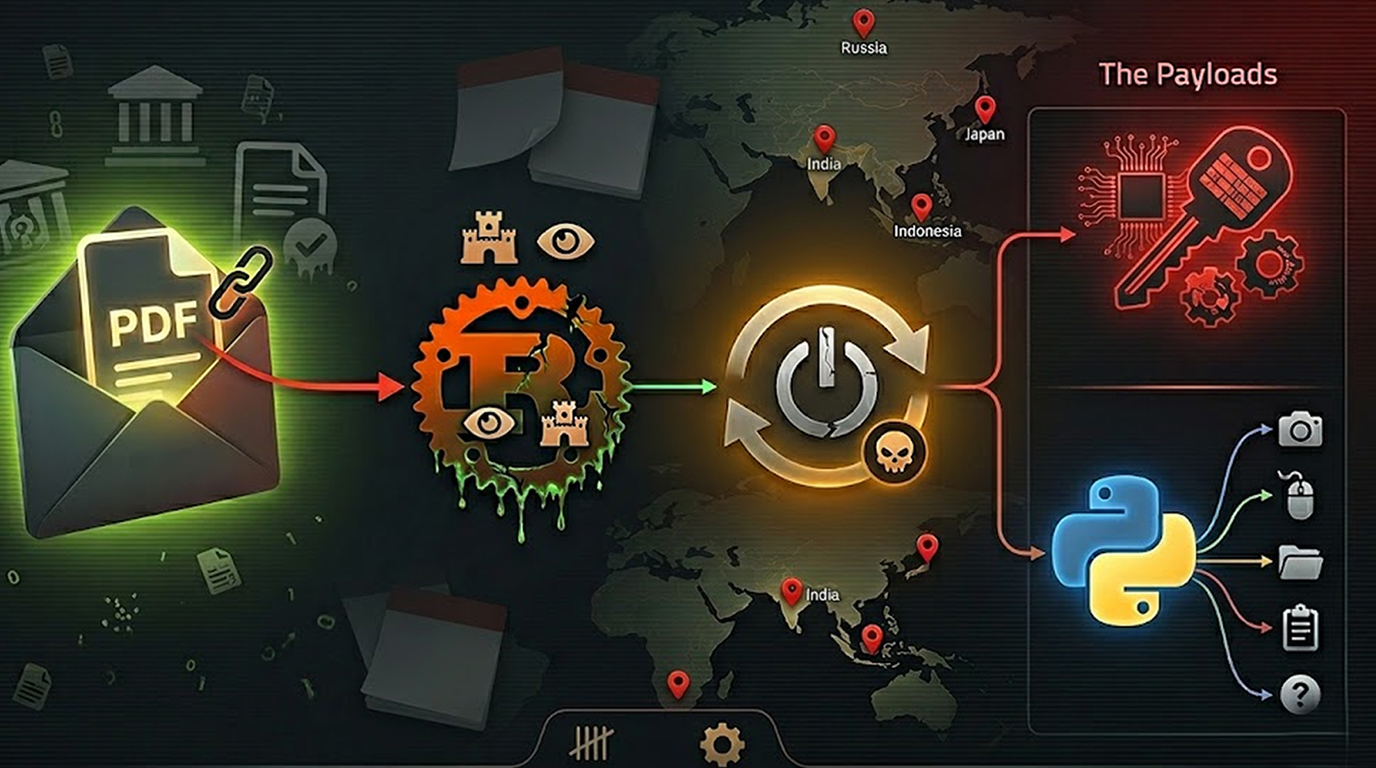
A Chinese cybercrime group is pretending to be tax authorities in two different countries. Their goal? Deliver malware that steals data, controls systems,...
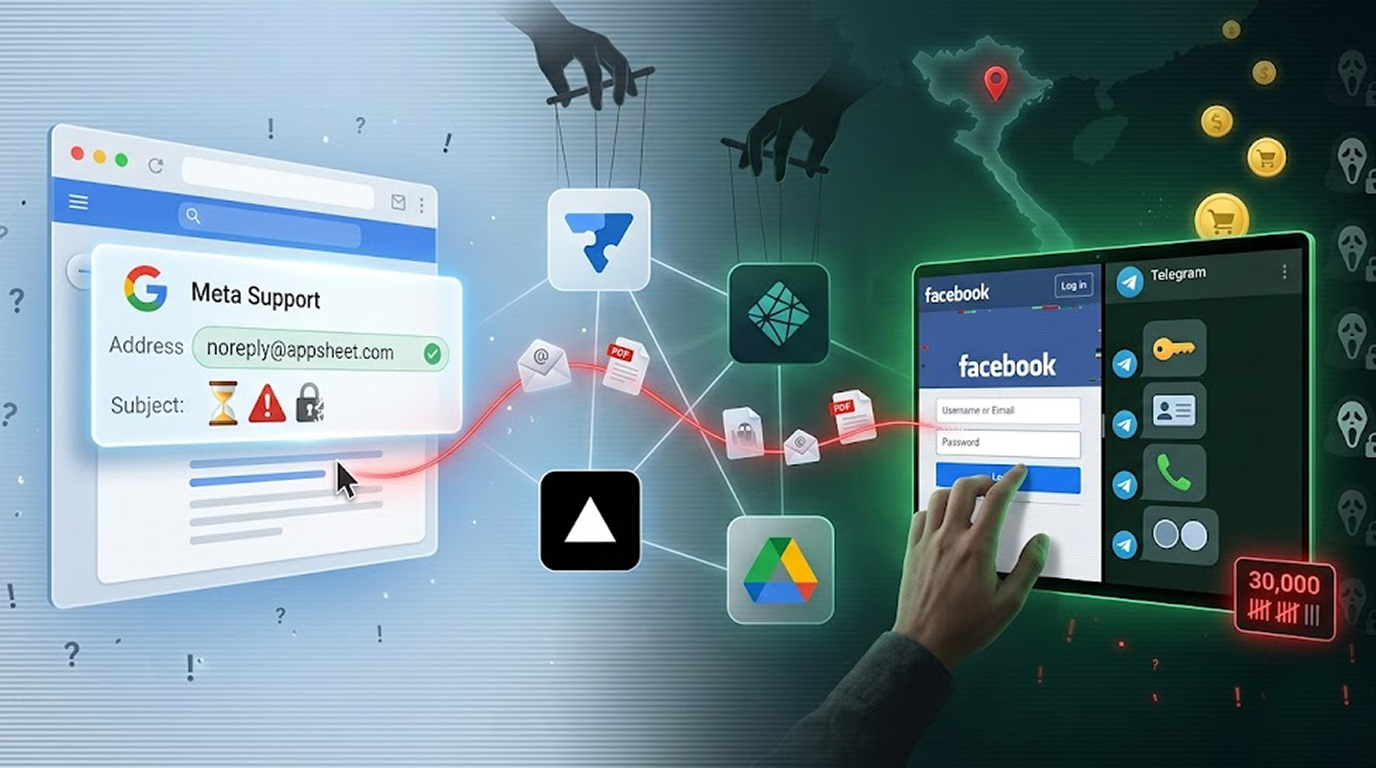
You receive a fake email from Meta Support that looks legitimate, as it was sent from a Gmail address using the @appsheet.com domain (which is operated by...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067