ASCII Collapse Vulnerability: How Unicode Enables XSS
You are a security engineer reviewing a web application. You have put in place a strong Content Security Policy. You sanitize all user input. You escape sp...
Found 230 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You are a security engineer reviewing a web application. You have put in place a strong Content Security Policy. You sanitize all user input. You escape sp...
You are a security engineer. You have spent months building defenses. Firewalls, intrusion detection, zero-trust architecture. You feel confident. Now ima...
You are a security engineer working for a company which has just released an AI-based assistant which takes care of all the customer needs. This AI assista...
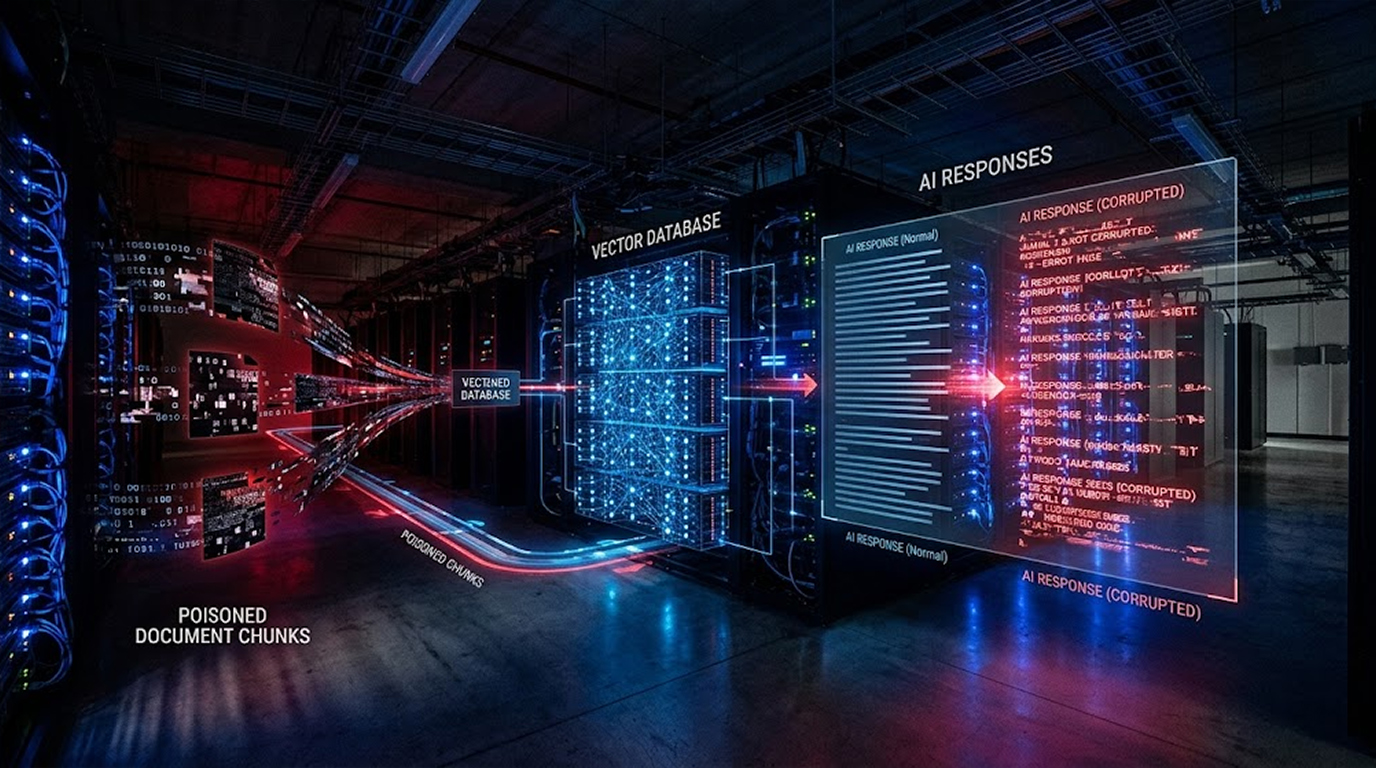
Your AI assistant just told a developer to install a malicious package. It cited a "trusted" internal document as the source. The document looked legitimat...
Threat actors have begun purchasing expired domains for the purposes of inheriting their reputations and traffic. They use these domains to redirect unsusp...
You tell your AI code assistant to help you solve your problem. It does its analysis and tells you about the problem, giving you some solution. You believe...
When you think about web security, CSS is probably the last thing on your mind. It is just styling, right? Colors, fonts, layouts. What could possibly be d...
This is one way an attacker can use to exploit websites. The dangling-byte technique is a new and innovative approach to HTTP desync that enables an attack...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067