SignDrop: CLFS Exploit Claims SYSTEM Access
A researcher published exploit code on Tuesday that claims a standard local Windows user can reach SYSTEM privileges through the Common Log File System dri...
Found 63 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A researcher published exploit code on Tuesday that claims a standard local Windows user can reach SYSTEM privileges through the Common Log File System dri...
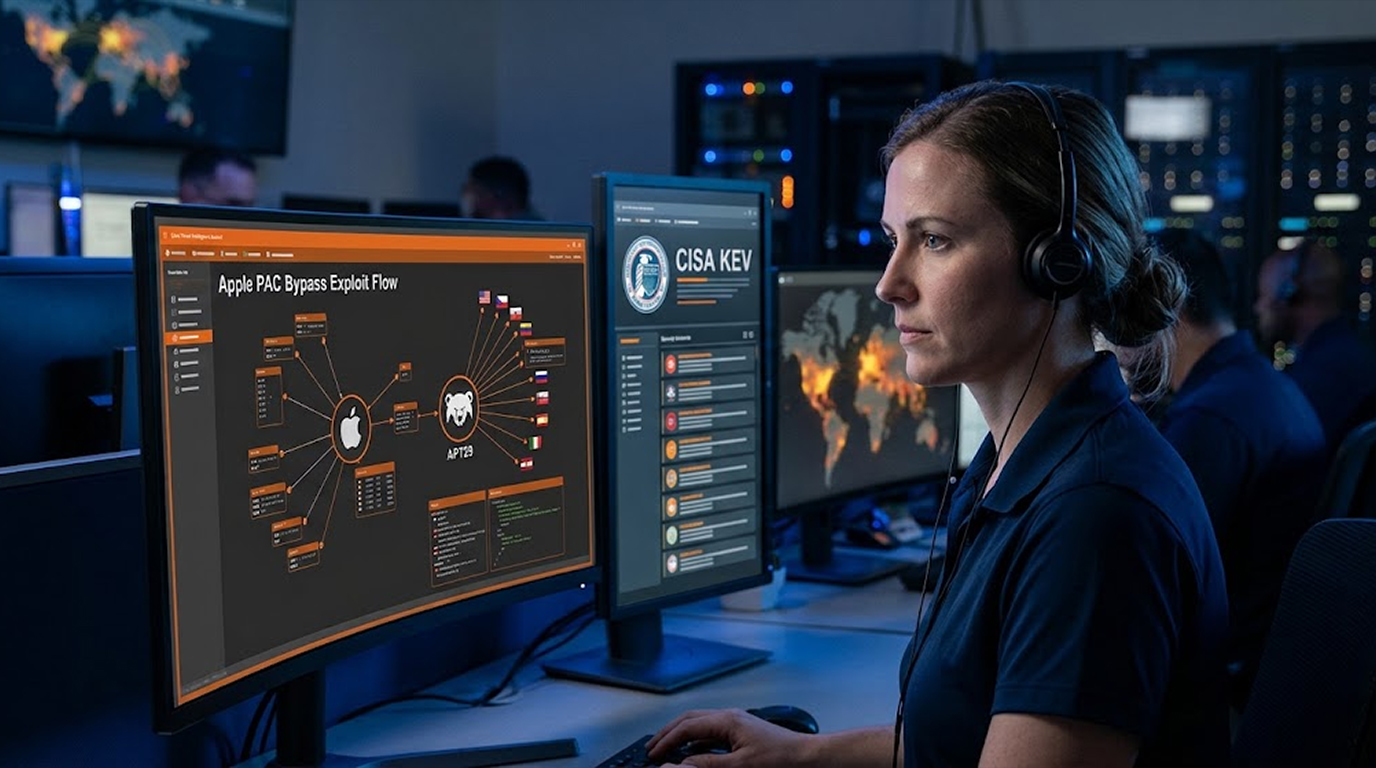
A 5.5 medium-severity vulnerability just landed in CISA's Known Exploited Vulnerabilities catalog, and the reason is a lesson every security team should in...
IBM just published details on two critical flaws in Langflow, an open-source tool for building AI agents and workflows, and the combination is about as bad...
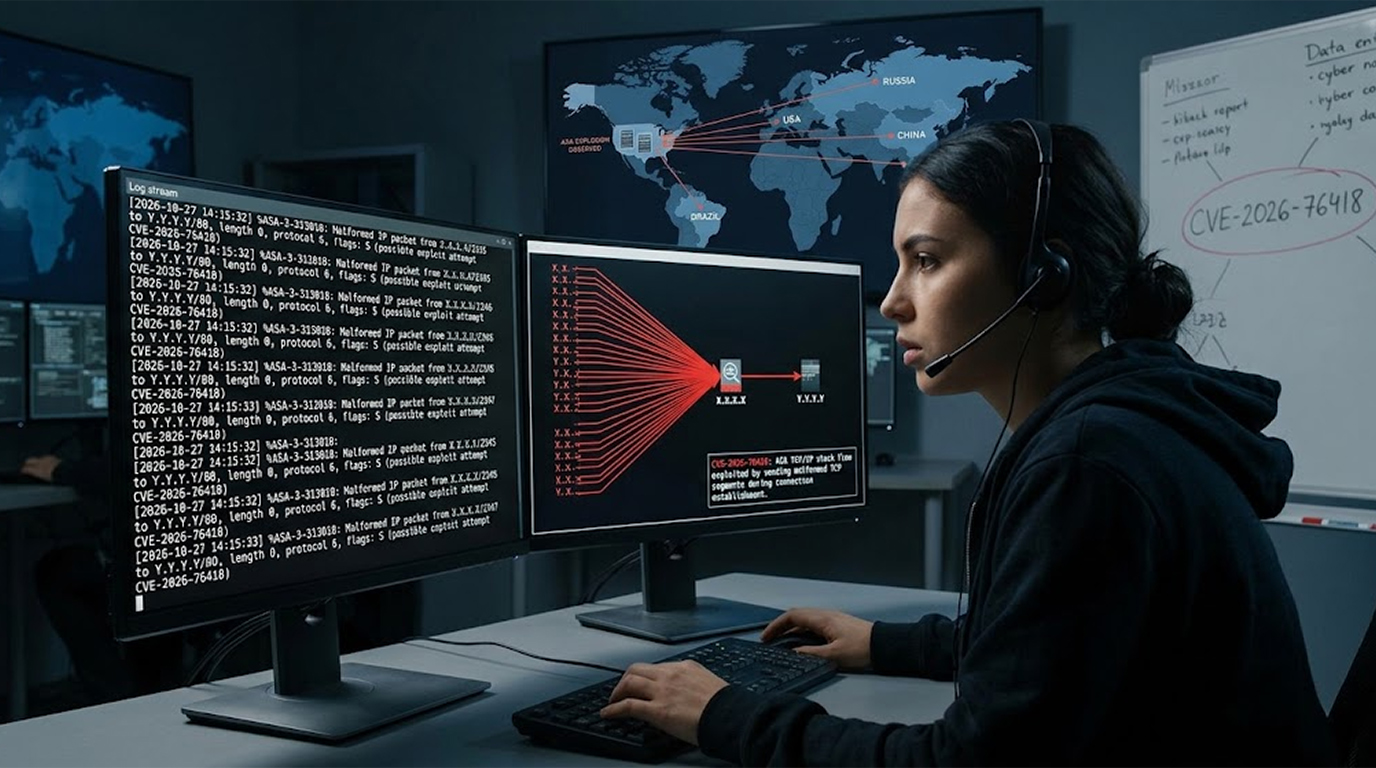
Cisco just confirmed that a high-severity flaw in its Secure Firewall ASA and FTD software is being exploited in the wild, and if you are running SSL remot...
Yes, you can audit your own website security, and for most small sites you should. A DIY website security audit covers the basics that stop the majority of...
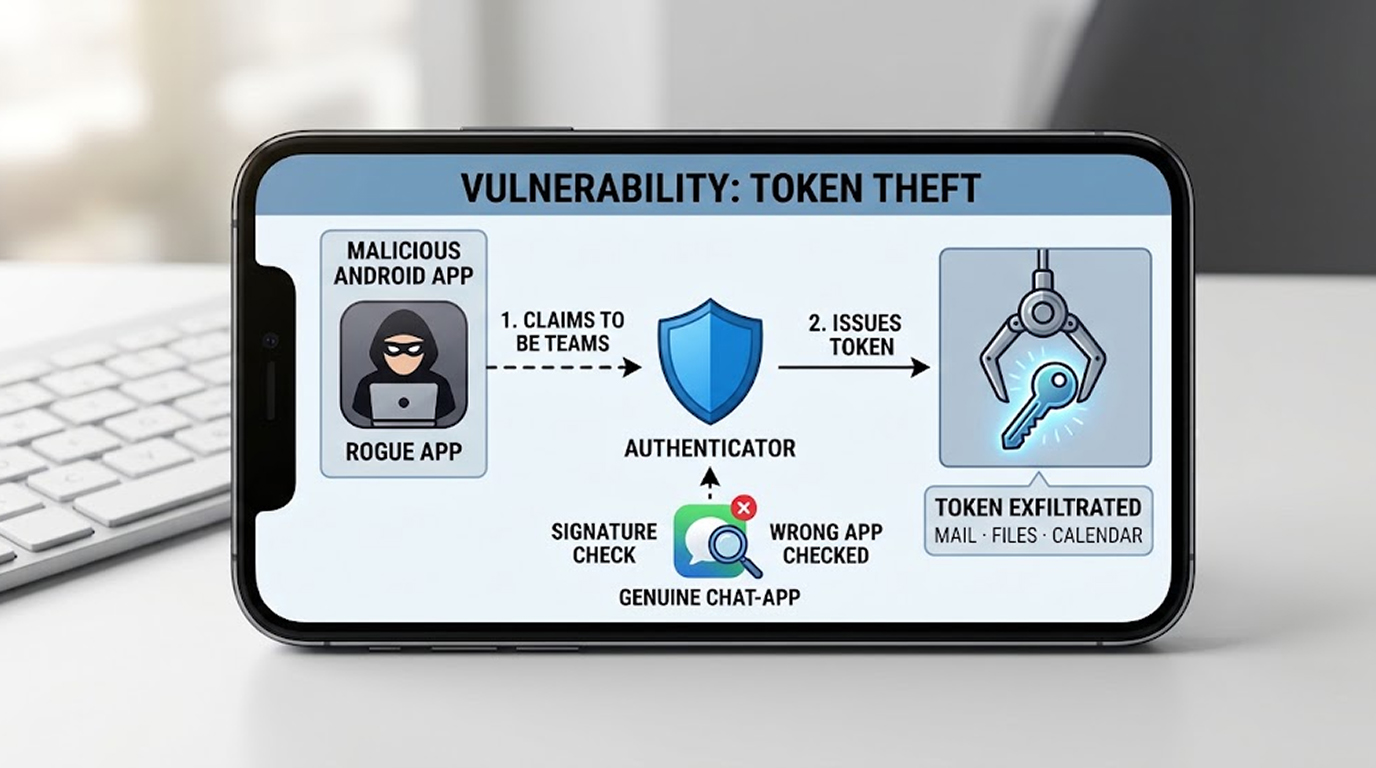
Microsoft just patched a nasty flaw in its Authenticator app for Android, because a malicious app with zero permissions could pose as a trusted Microsoft a...
Most ransomware crews rely on human operators to manually pivot through a network and hunt for sensitive files, but a Russian-speaking group tied to the IN...
You're sitting in a coffee shop, or on a train, or in a lecture hall, and your phone buzzes with a popup saying someone nearby wants to share a file with y...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067