Cisco ASA Flaw: CVE-2026-76418 Exploited in Wild
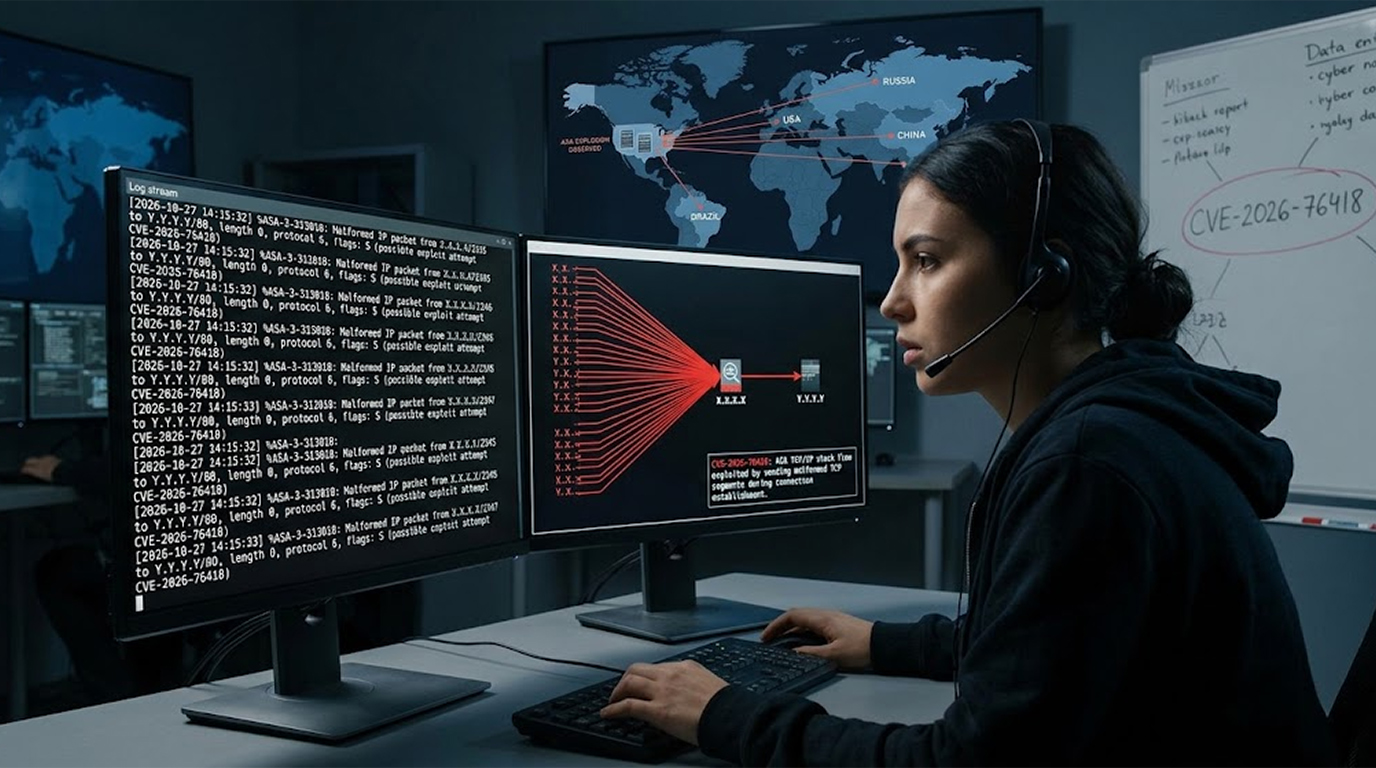
Cisco just confirmed that a high-severity flaw in its Secure Firewall ASA and FTD software is being exploited in the wild, and if you are running SSL remot...
Found 91 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Cisco just confirmed that a high-severity flaw in its Secure Firewall ASA and FTD software is being exploited in the wild, and if you are running SSL remot...
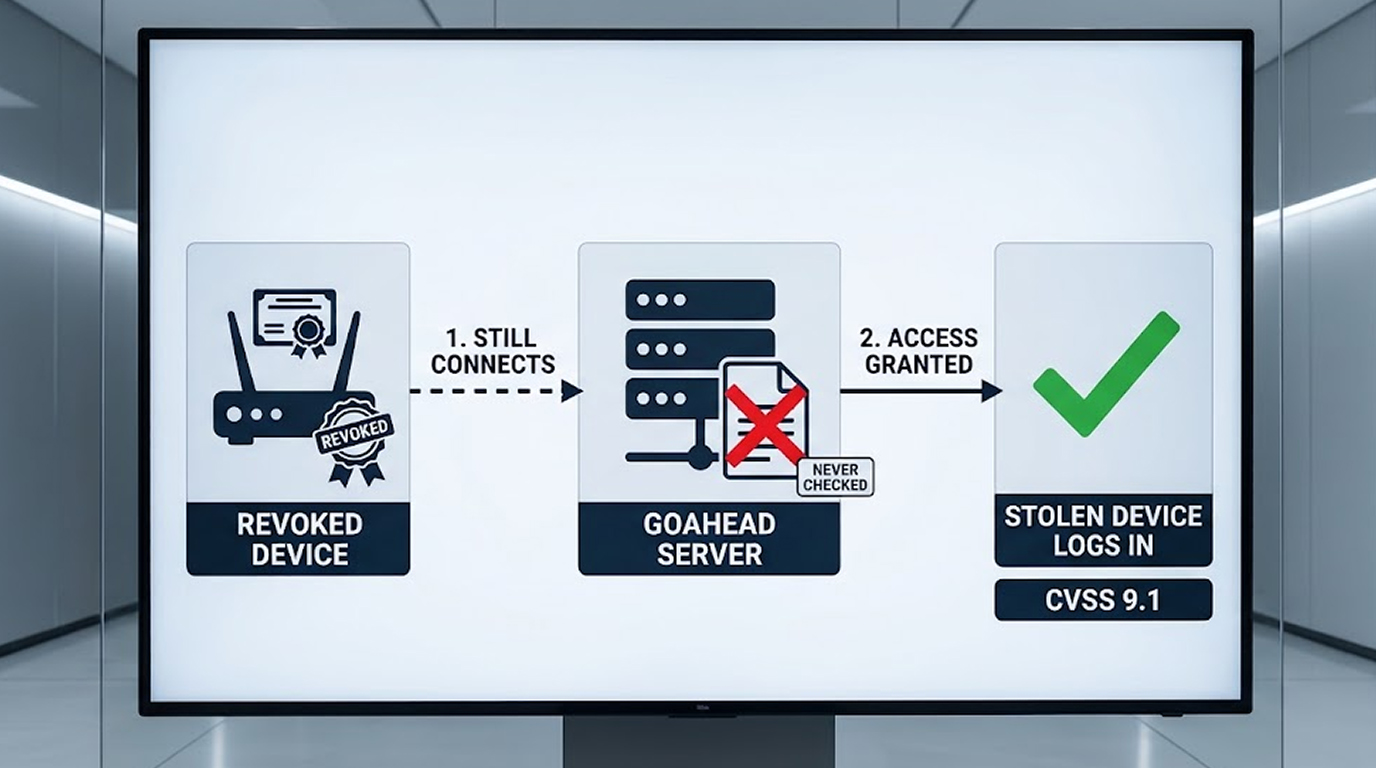
Your router, printer, or industrial controller might be accepting logins from stolen or retired devices, because a critical flaw in the GoAhead embedded we...
Yes, you can audit your own website security, and for most small sites you should. A DIY website security audit covers the basics that stop the majority of...
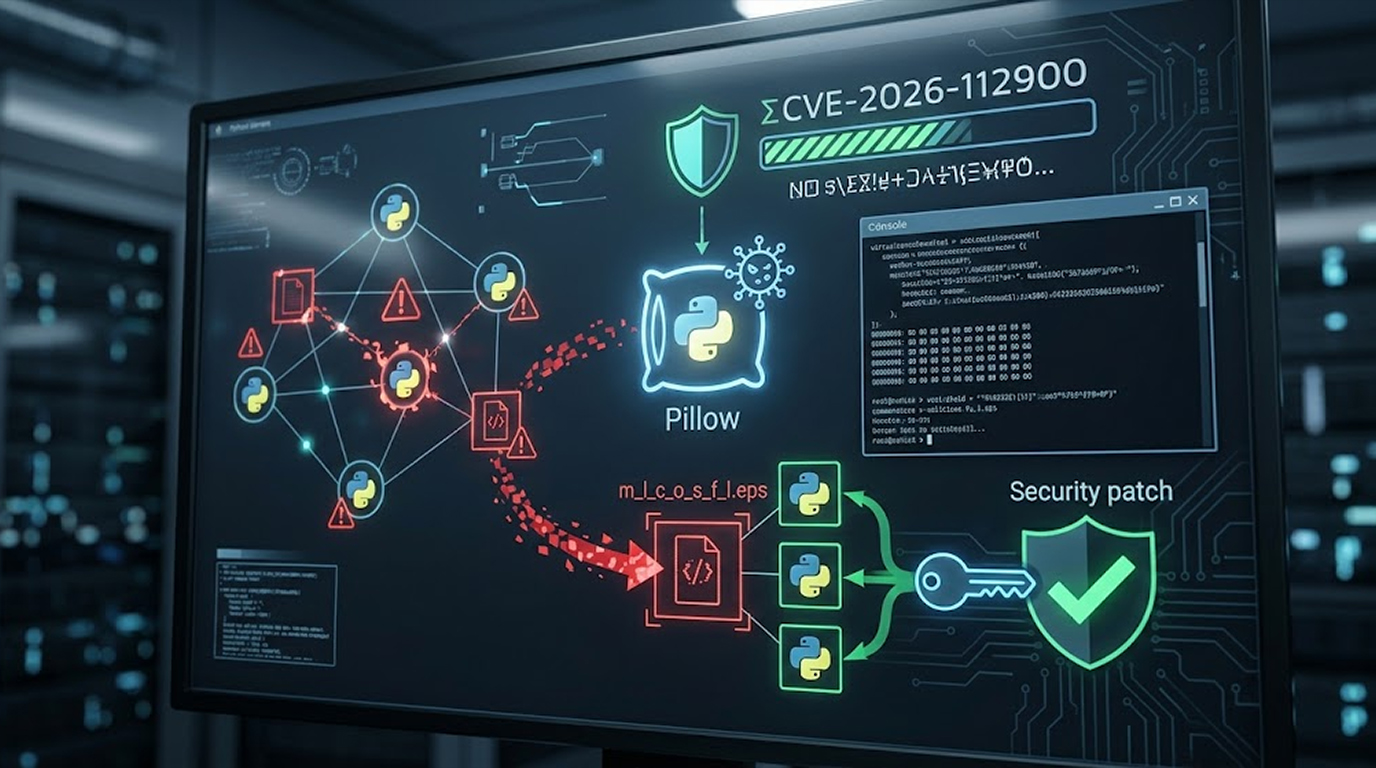
Your Python application might be executing operating system commands just because it processed an image upload, because a critical Pillow EPS vulnerability...
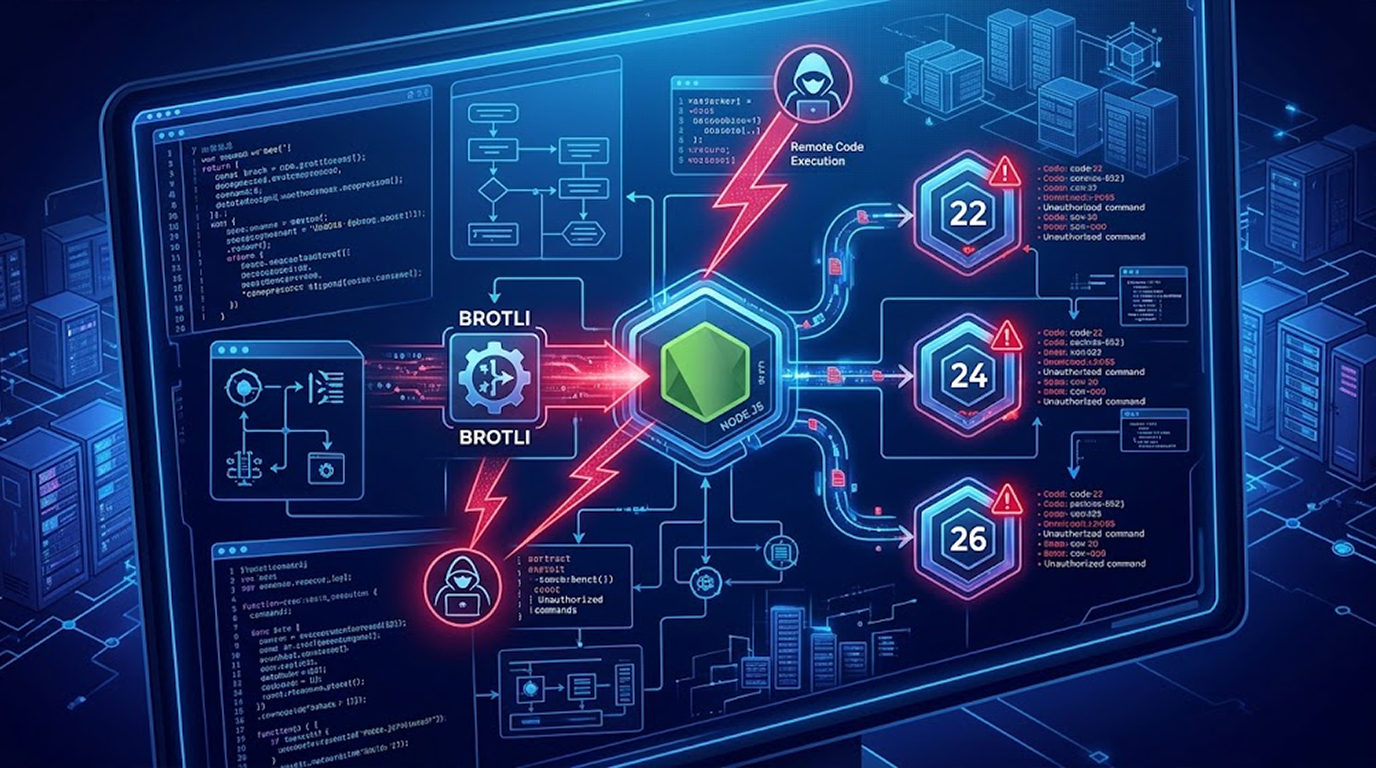
Your Node.js server might be running code that can be crashed or compromised by a malformed request, because the project just released security updates fix...
Your WordPress site might be handing anonymous visitors a route straight into your server's filesystem, because a security researcher just published a proo...
Somewhere on your network there is a service you forgot about, a staging server that was never meant to face the internet, a database with no password, an...
Two days. That's all it took. SonicWall disclosed CVE-2026-15409 on July 14, 2026. By July 16, someone was already scanning for vulnerable appliances at sc...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067