Node.js Brotli Flaw: Remote Code Execution Patch
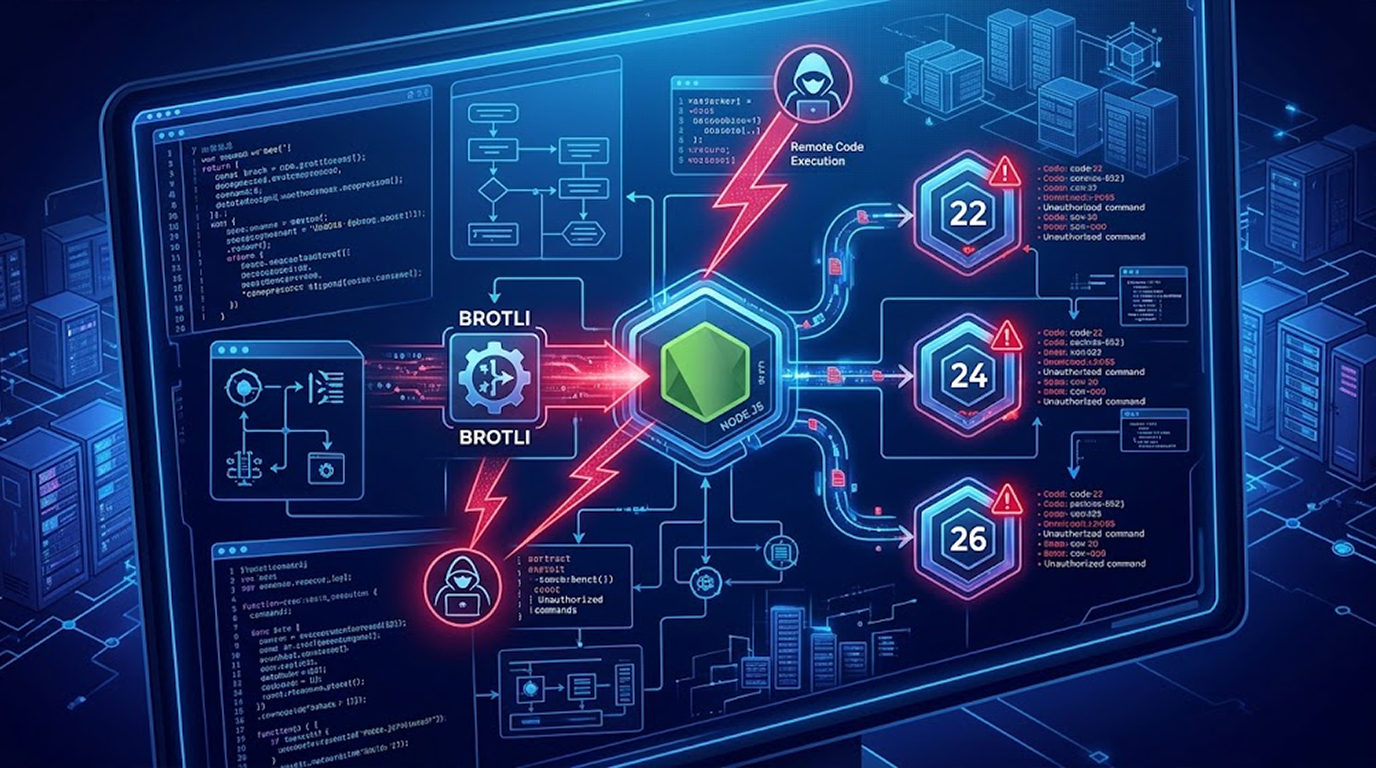
Your Node.js server might be running code that can be crashed or compromised by a malformed request, because the project just released security updates fix...
Found 31 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Your Node.js server might be running code that can be crashed or compromised by a malformed request, because the project just released security updates fix...
Cisco has a new problem. And it's a big one. A maximum-severity flaw in Identity Services Engine is being actively exploited. The bug lets an unauthentica...
There's a bug in FreePBX that lets someone walk in without a login, drop a cron job, and get a shell on your server. No username. No password. Just a web r...
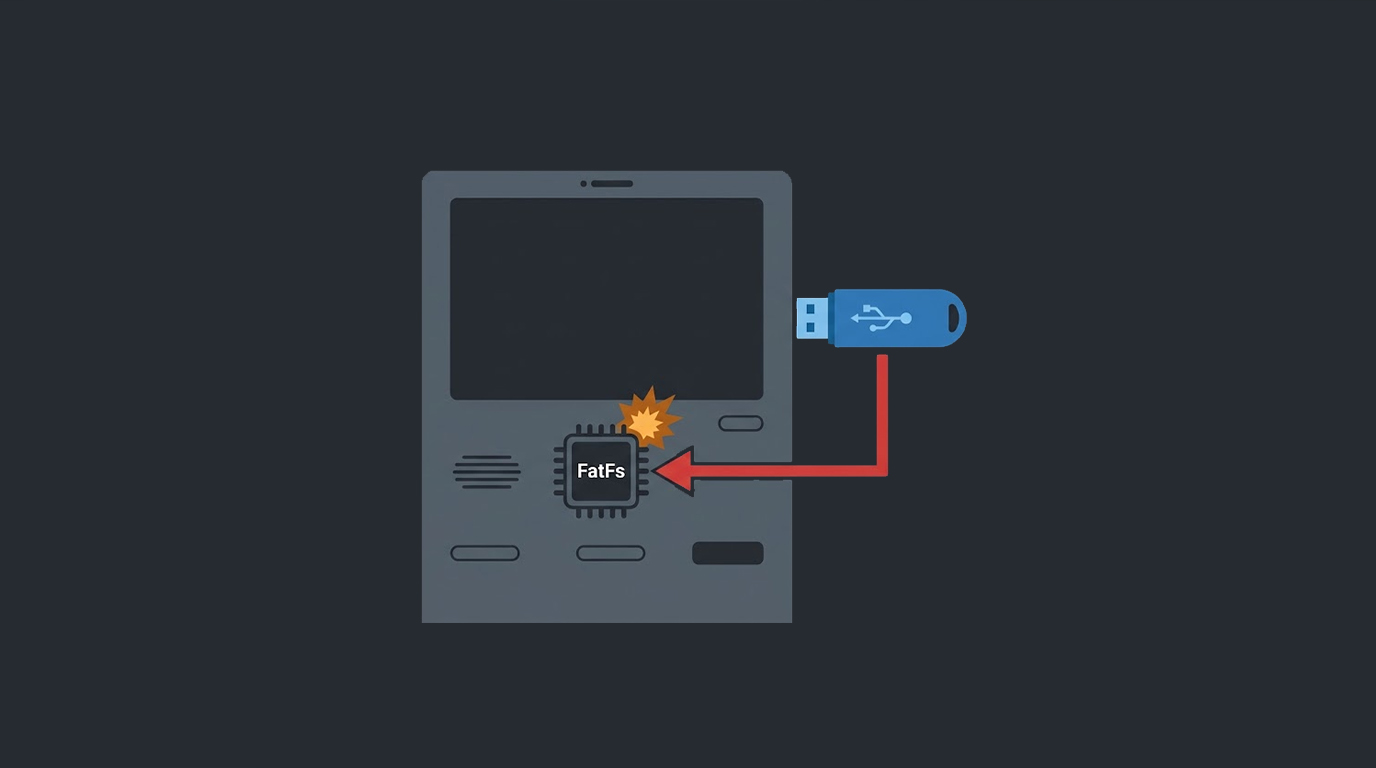
Security firm runZero has uncovered seven vulnerabilities in FatFs, a lightweight filesystem library that handles FAT and exFAT formats for USB drives and...
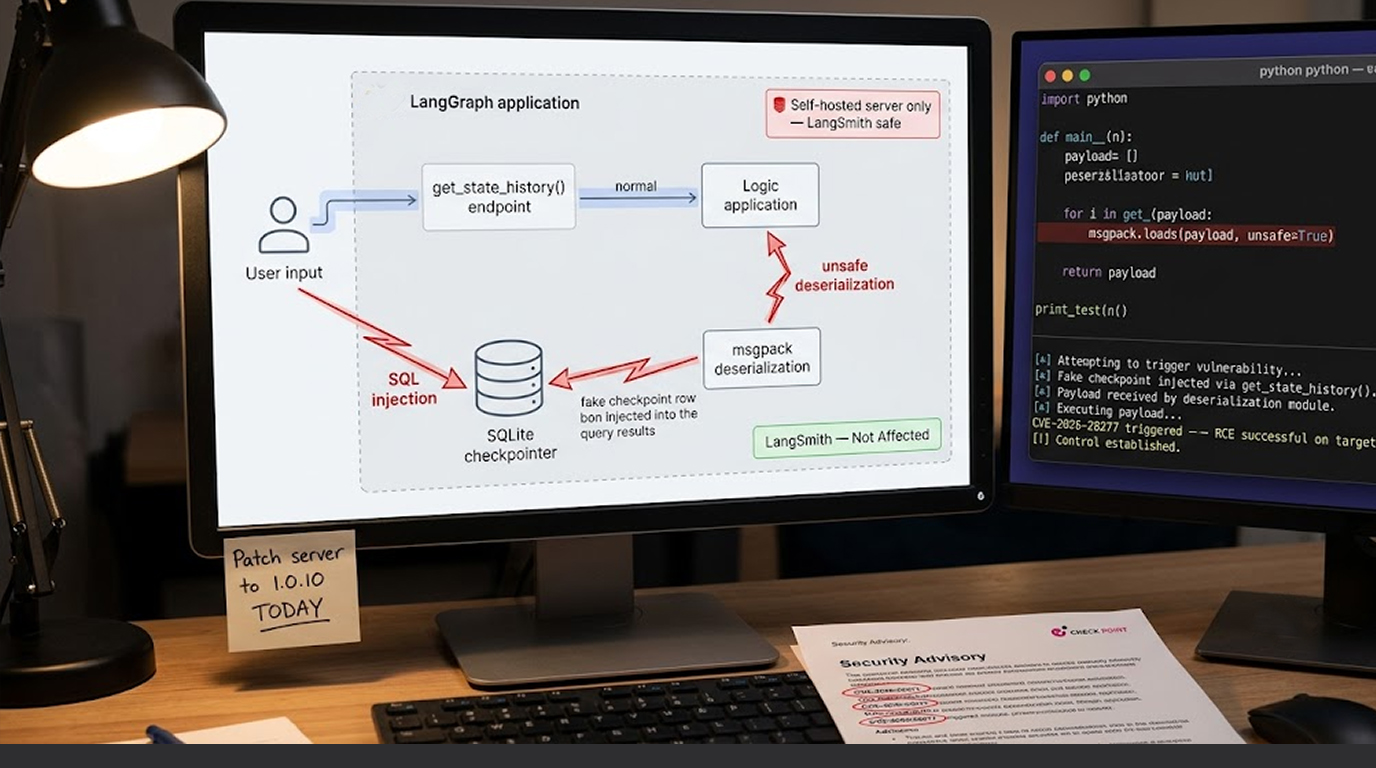
LangGraph is helping you build complex, stateful, multi-agent AI applications. It's open-source, built by LangChain, and widely used by developers who want...
A popular blogging platform has a serious problem, attackers can steal admin passwords and API keys without ever logging in, and the vulnerability has exis...
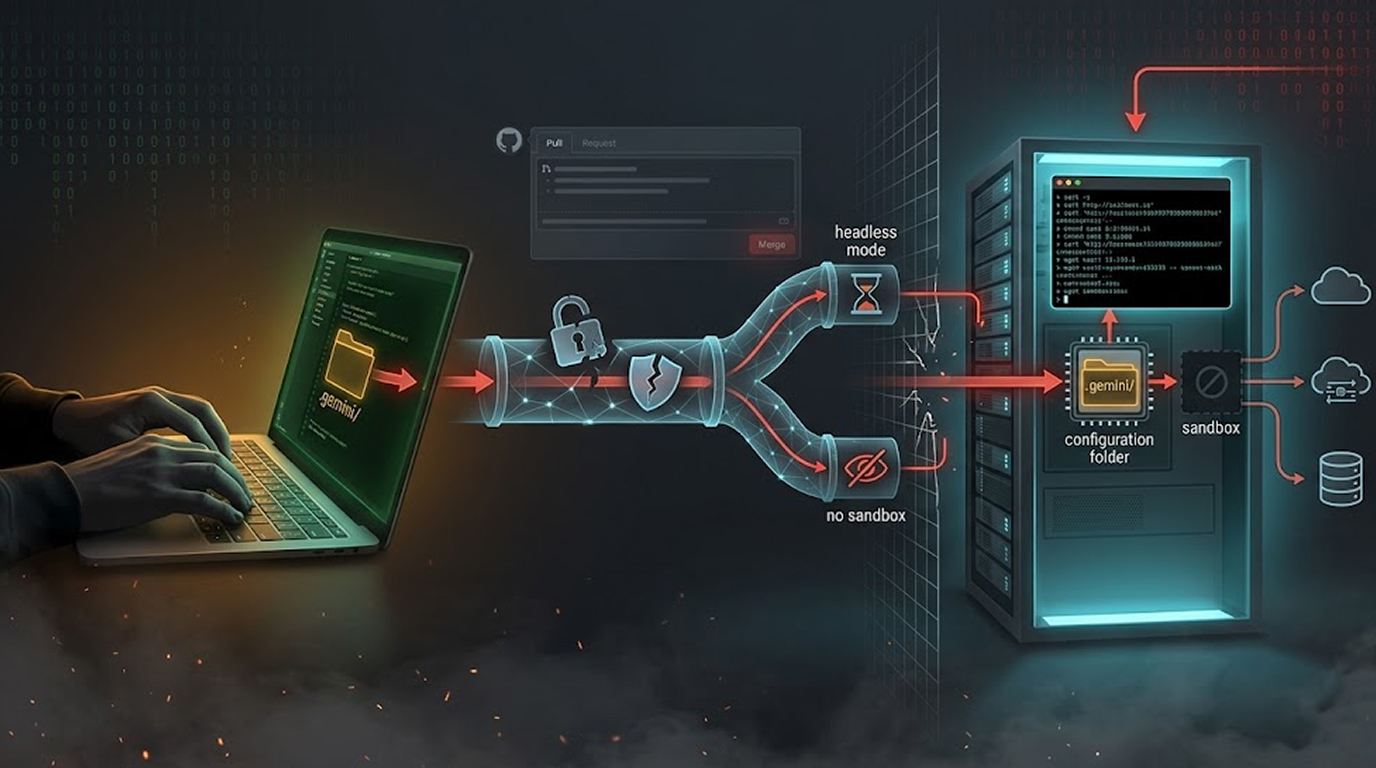
A perfect 10. That is the CVSS score Google assigned to a security flaw in its Gemini CLI tool. And for good reason. The Gemini CLI remote code execution...
According to recent discoveries made by cybersecurity researchers, they have identified three significant vulnerabilities present in two highly utilized op...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067