CL-UNK-1211: AI-Powered Linux Espionage Campaign
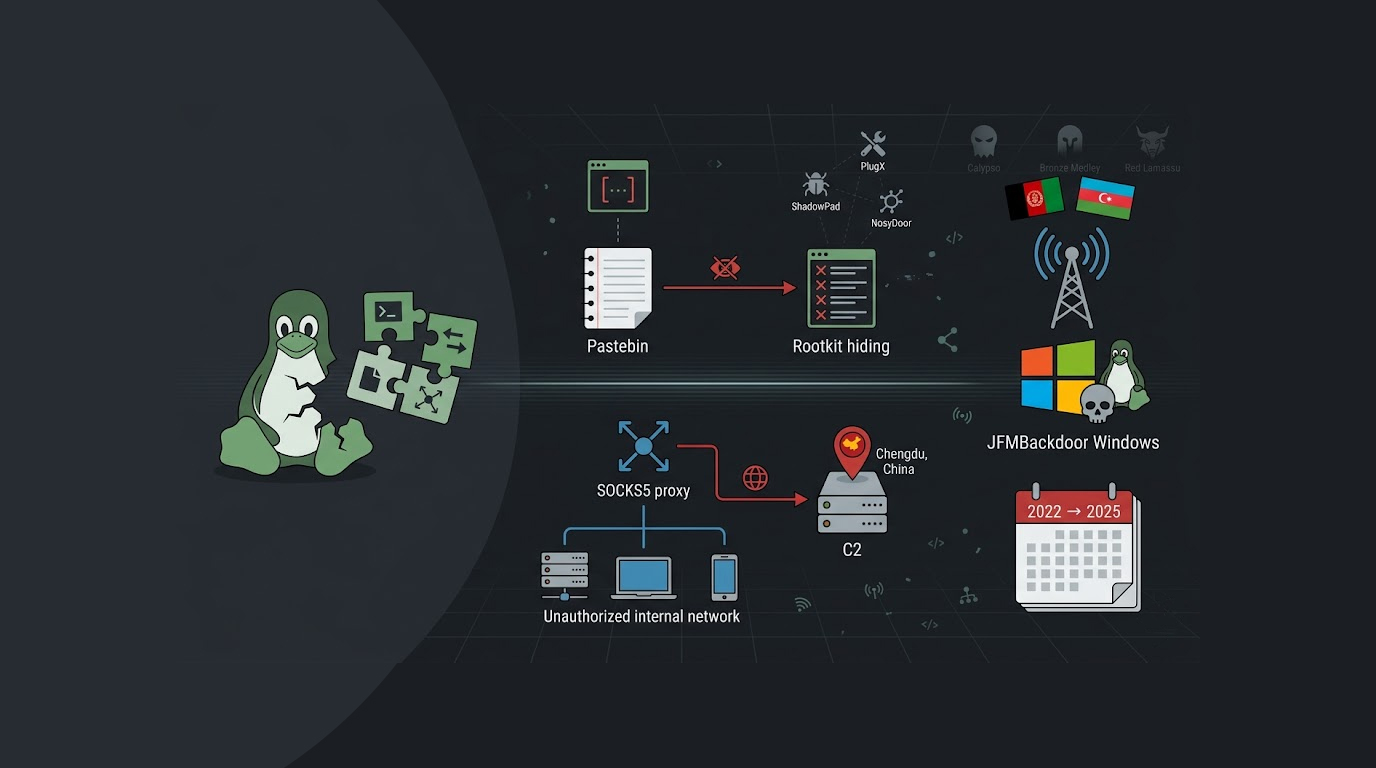
Unit 42 spent six months watching a cluster they now call CL-UNK-1211 work its way through government Linux servers across multiple regions. The campaign r...
Found 9 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Unit 42 spent six months watching a cluster they now call CL-UNK-1211 work its way through government Linux servers across multiple regions. The campaign r...
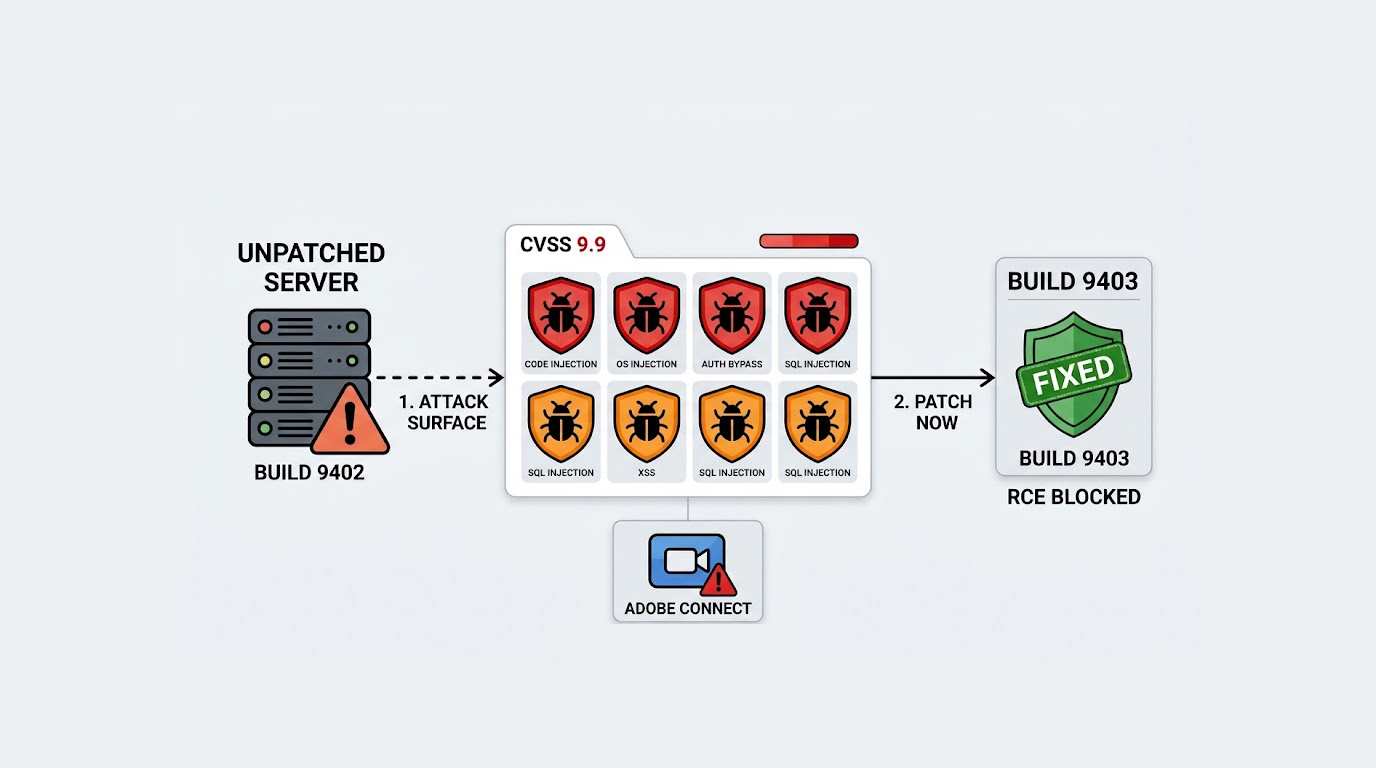
Adobe just dropped a massive security update, and if you are running Adobe Campaign Classic on Windows or Linux, you need to patch your servers right now,...
Linux servers running KSMBD, the kernel's built-in SMB server, are currently exposed to two publicly reported remote code execution vulnerabilities, both c...
CISA added three Linux kernel vulnerabilities to its Known Exploited Vulnerabilities catalog on Friday. All three are being exploited in the wild. Red Hat...
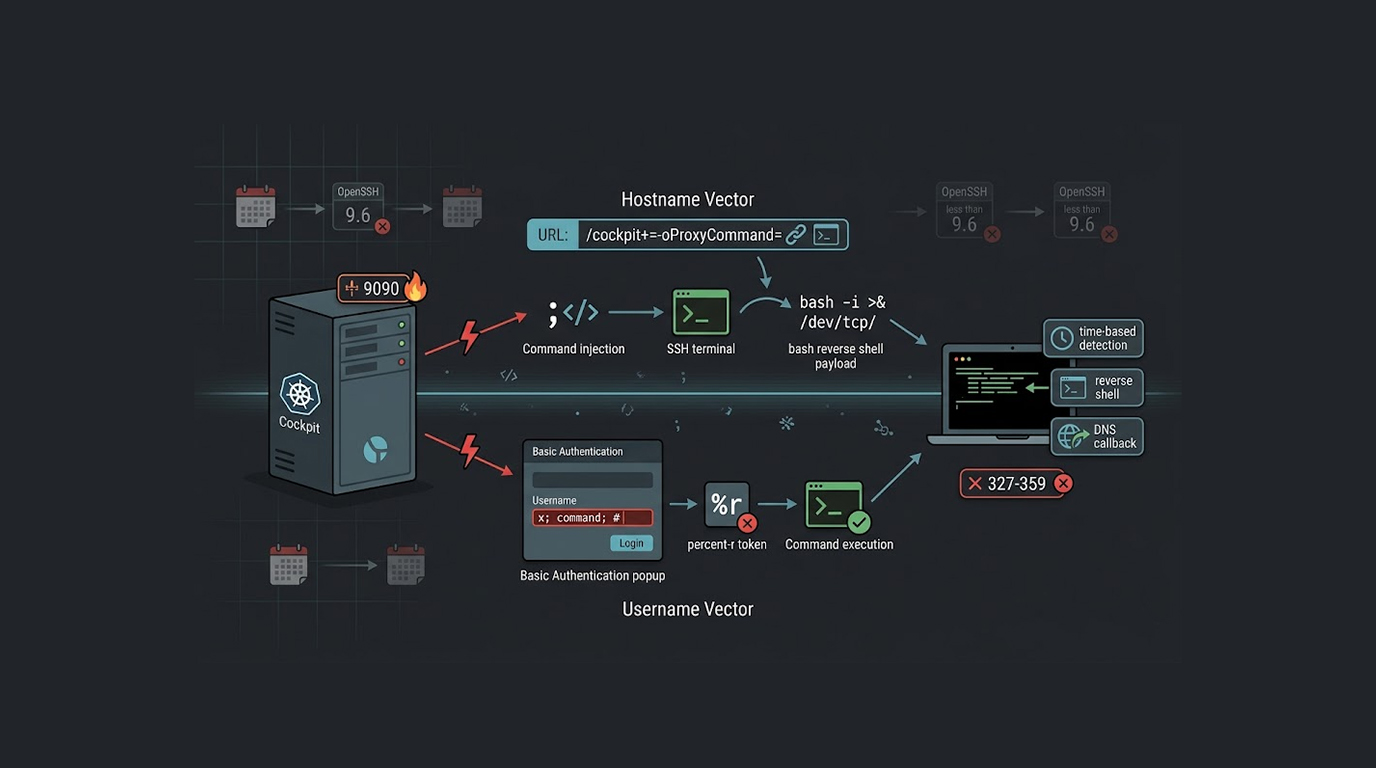
A security flaw in Cockpit allows an attacker to run arbitrary code on the server without authenticating first. The problem manifests itself through Cockpi...
Showboat malware targets MT companies in the Middle East. It looks like was created by someone linked to Chinese-sponsored organizations and has been utili...
Misconfigured and vulnerable Linux servers have become the latest target of a stealthy malware campaign delivering a threat dubbed perfctl, primarily aimed...
For years, Linux has been celebrated for its robust security, especially compared to more commonly targeted operating systems like Windows. However, this p...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067