SignDrop: CLFS Exploit Claims SYSTEM Access
A researcher published exploit code on Tuesday that claims a standard local Windows user can reach SYSTEM privileges through the Common Log File System dri...
Found 17 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A researcher published exploit code on Tuesday that claims a standard local Windows user can reach SYSTEM privileges through the Common Log File System dri...
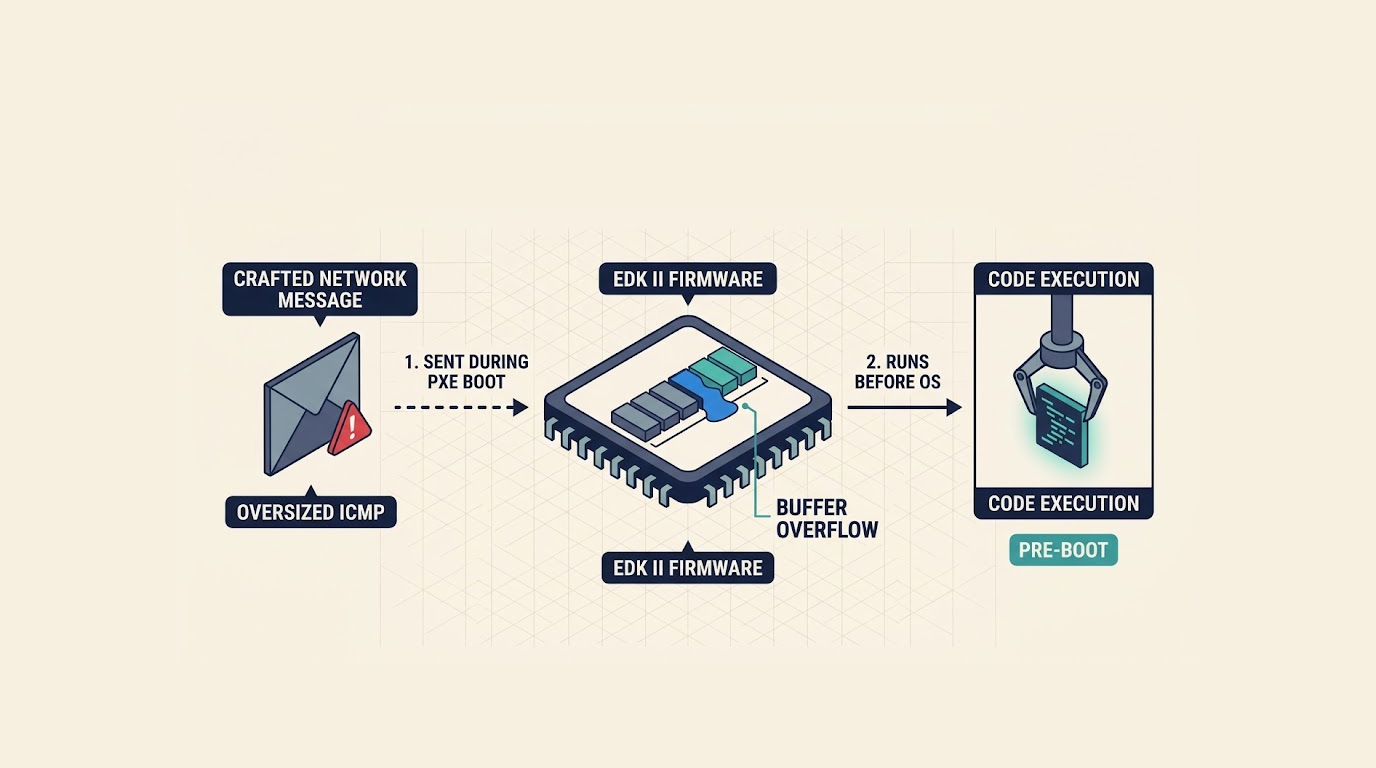
Your servers might be carrying a 16-year-old vulnerability in the firmware that boots them, because a critical buffer overflow in EDK II, the open-source c...
You have backups, you have a recovery plan, and you have a document that says what to do when ransomware hits, but none of that proves you can actually rec...
You open an attachment, it looks like a normal invoice, a standard contract, a routine report, nothing about it triggers suspicion, and yet the moment your...
You are a security engineer reviewing a web application. You have put in place a strong Content Security Policy. You sanitize all user input. You escape sp...
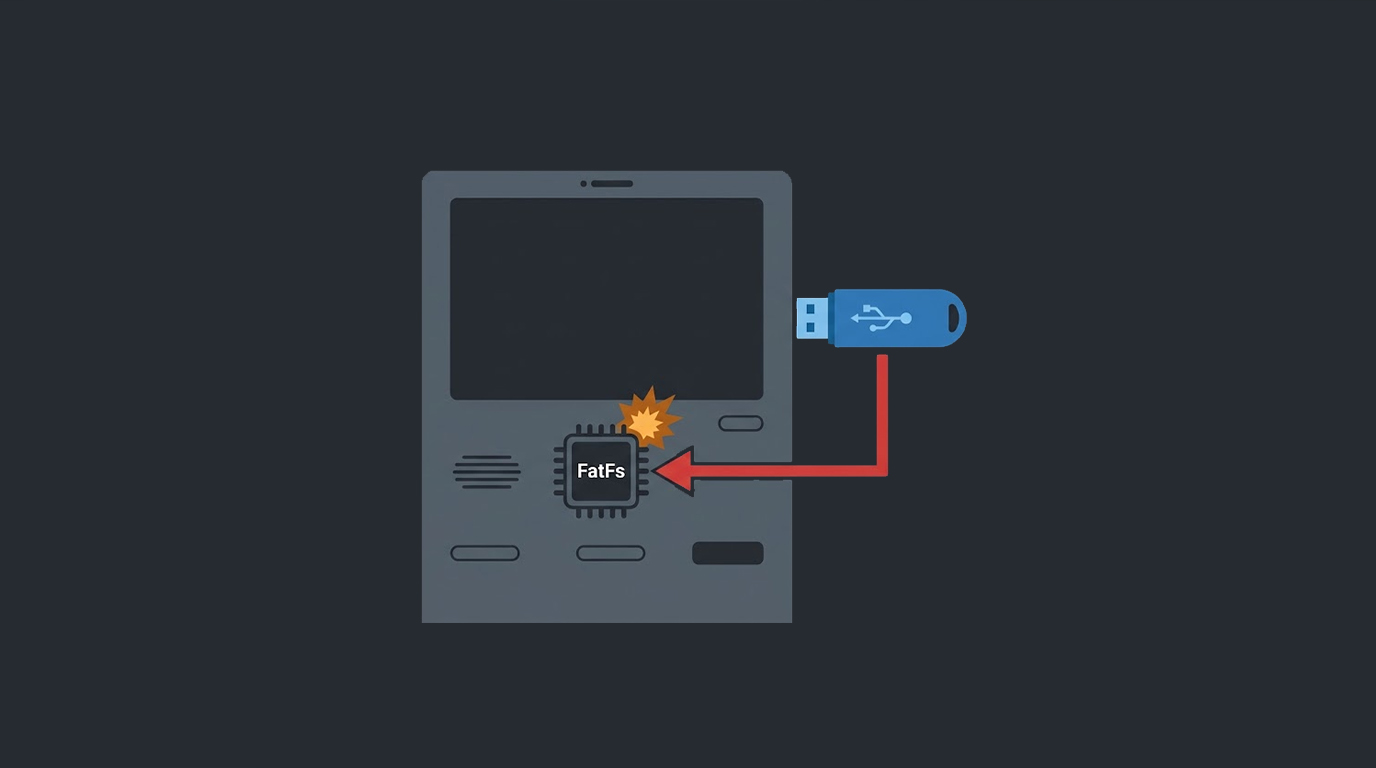
Security firm runZero has uncovered seven vulnerabilities in FatFs, a lightweight filesystem library that handles FAT and exFAT formats for USB drives and...
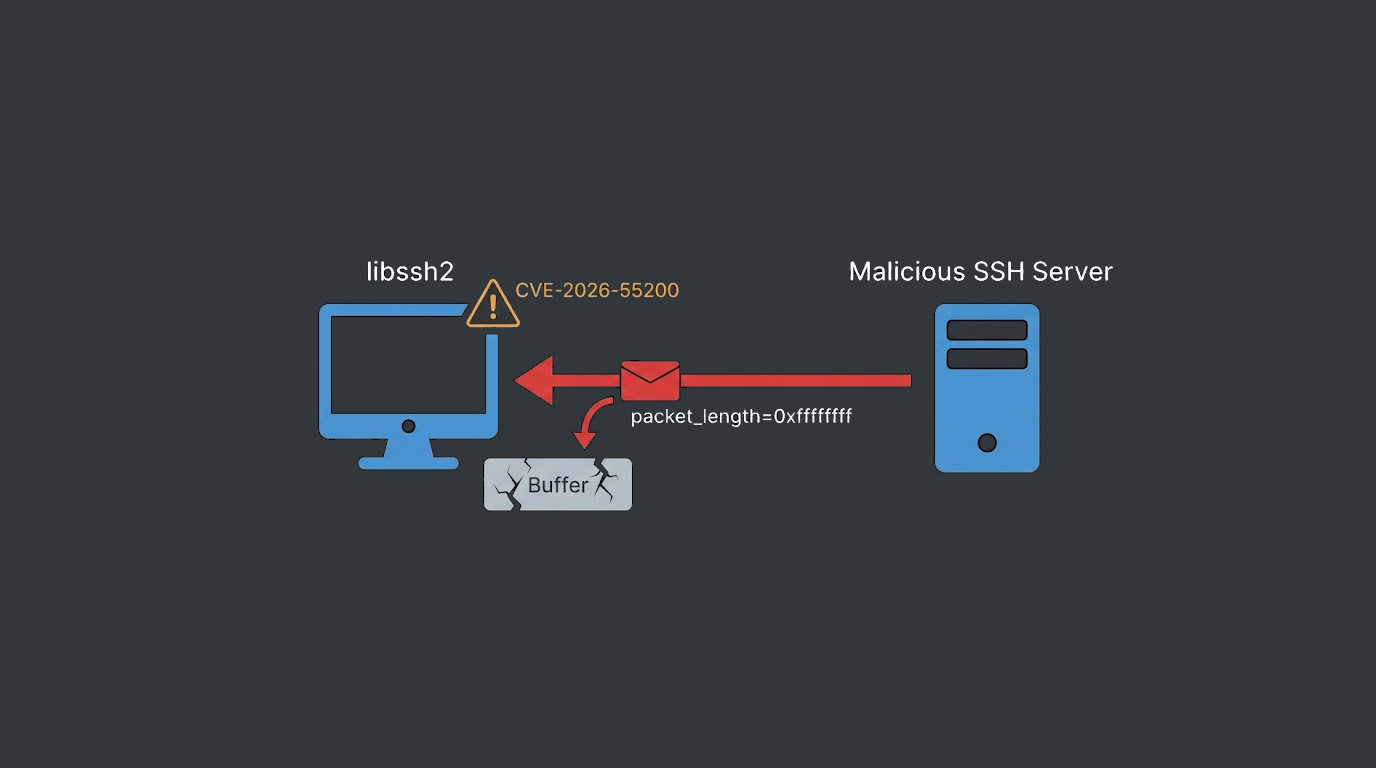
Proof of concept released to the public for CVE-2026-55200 – an extremely critical vulnerability in libssh2 where a malicious SSH server can cause me...
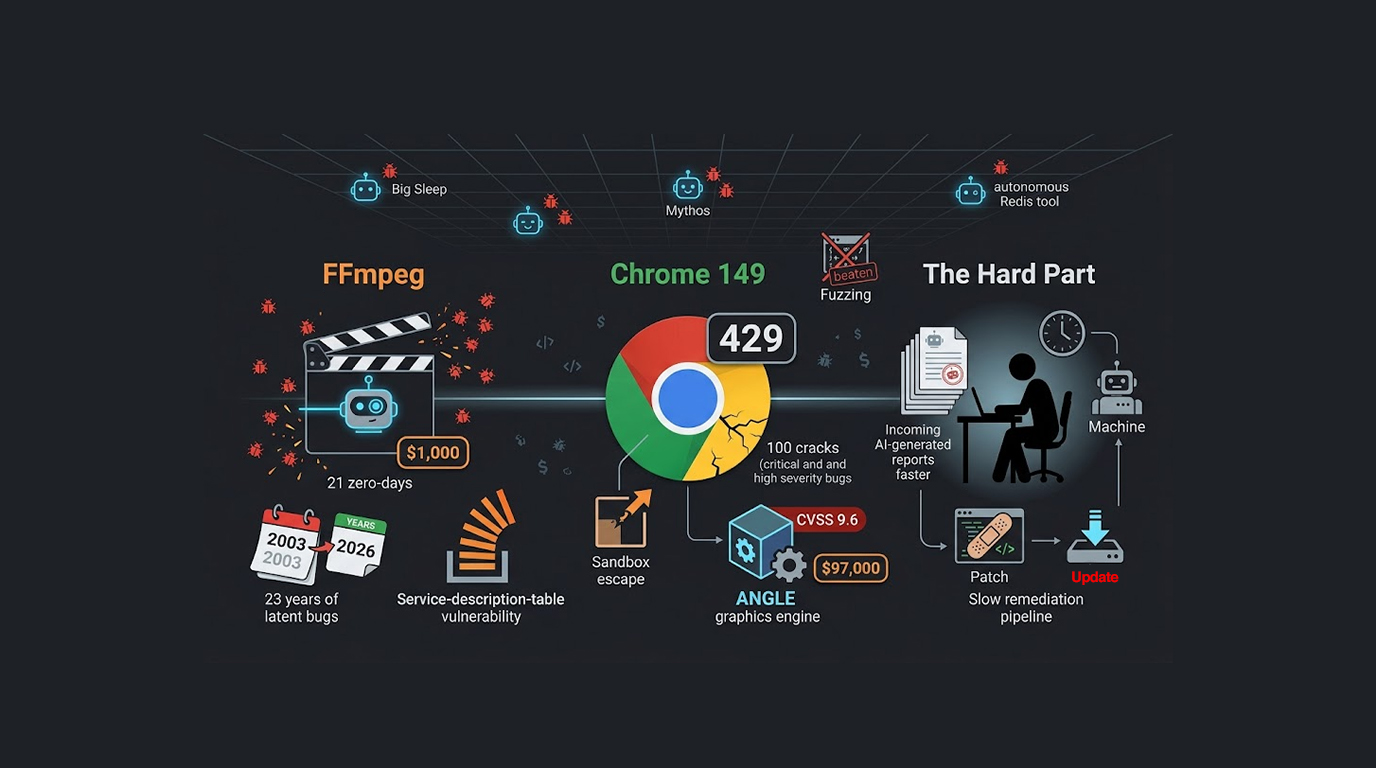
This week saw the arrival of two major security incidents. A security startup stated that 21 previously unknown vulnerabilities were discovered in FFmpeg (...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067