Fake Web3 Accelerator Pushes npm Malware at Founders
Your npm install might have handed a stranger your browser cookies, your wallet files, and a persistent backdoor, because researchers just documented a fak...
Found 14 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Your npm install might have handed a stranger your browser cookies, your wallet files, and a persistent backdoor, because researchers just documented a fak...
Threat actors have found a new way to turn a trusted platform into a malware delivery system, and this time they are using ChatGPT Custom GPTs to disguise...
A cluster of nearly 800 malicious packages has been published to the npm registry as part of a new campaign designed to deliver cross-platform malware targ...
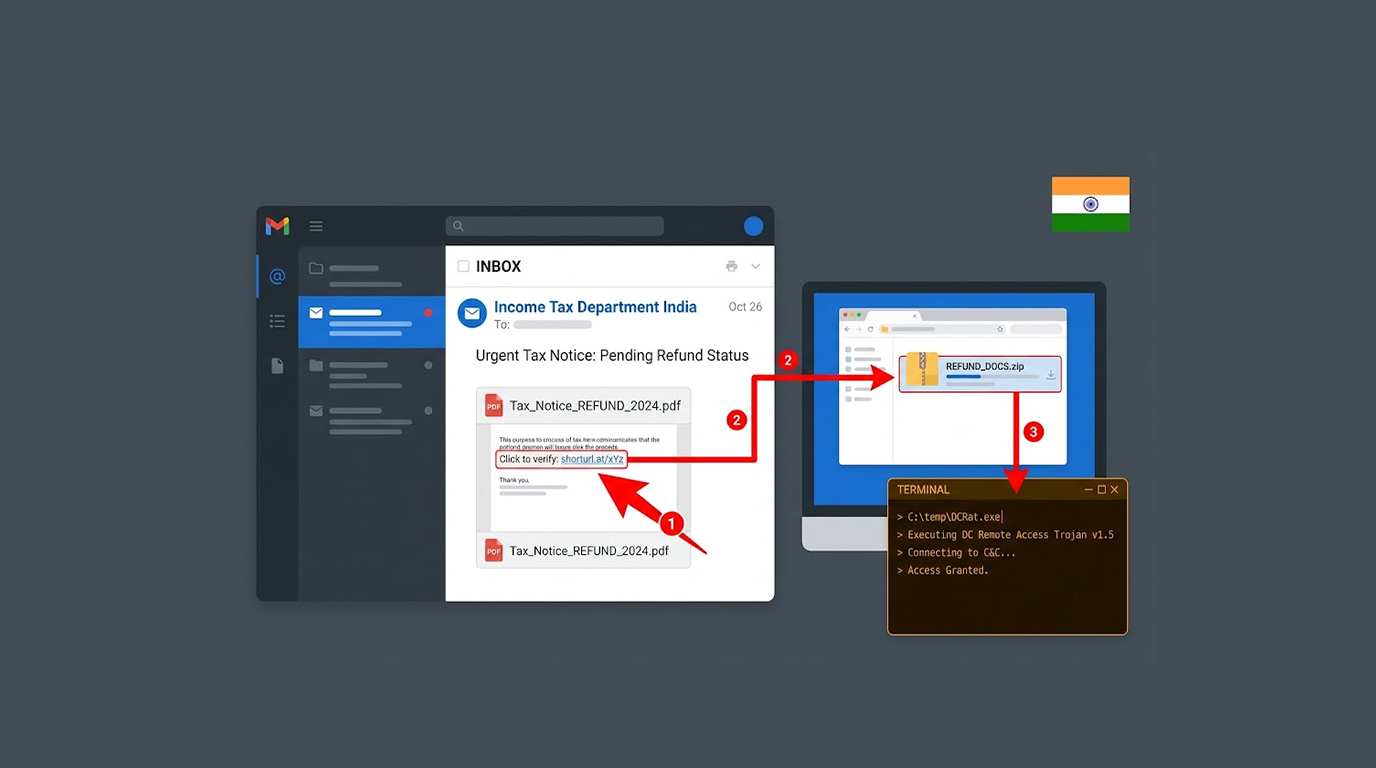
An activity cluster that is associated with China-nexus threat actors has been noticed targeting Indian taxpayers, tax professionals, and corporate financi...
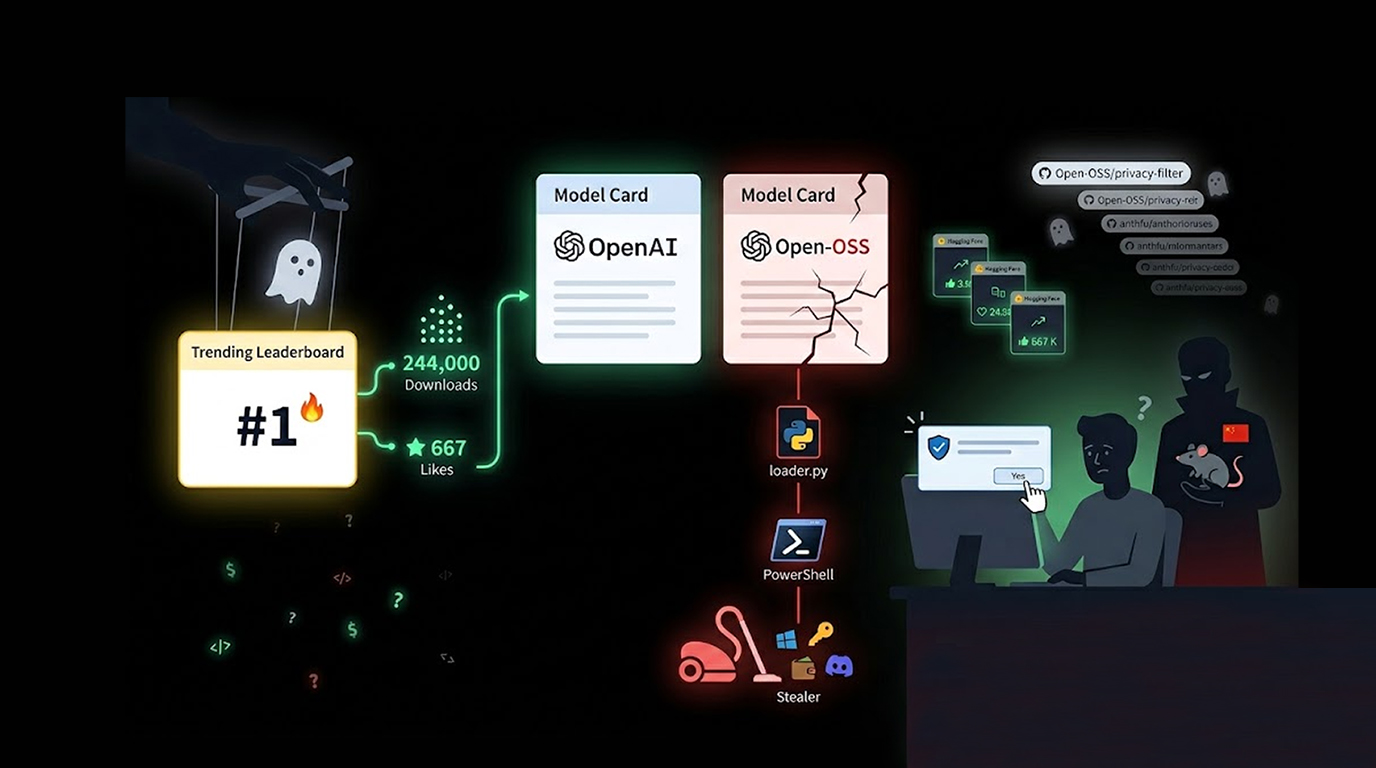
A malicious repository on Hugging Face ranked #1 on the platform by impersonating OpenAI's just-released Privacy Filter model while delivering a Rust-based...
You have run Cobalt Strike for years, it works, but it is also the most signatured tool on the market, every defender knows how to spot it Havoc is differ...
A China-based cybercriminal group known as Silver Fox (also referred to as SwimSnake / Valley Thief / Void Arachne) is currently using a typosquatting tech...
According to Elastic Security Labs’ cybersecurity experts, they identified a highly advanced sophistication ClickFix campaign using legitimate websit...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067